

Ring 1.0 is released
On July 21, Savoir-faire Linux (SFL) announced the release of version 1.0 of its Ring communication tool. It is a cross-platform (Linux, Android, macOS, and Windows) program for secure text, audio, and video communication. Beyond that, though, it is part of the GNU project and is licensed under the GPLv3. Given the announcement, it seemed like a quick trial was in order. While it looks like it has great promise, Ring 1.0 falls a bit short of expectations.
Privacy and security are two of the main attributes that Ring is striving for. To start with, Ring provides a peer-to-peer architecture that avoids a central server, which is done to maintain the privacy of the participants. The data is encrypted between the endpoints to thwart those in the middle who might want to listen in. Ring evolved from the SFLphone project, but moved away from SFLphone's centralized architecture, which is part of why the name has changed.
The network is coordinated via a distributed hash table (DHT) that provides distributed key-value data storage. Ring uses the OpenDHT library to implement its hash table, which can store signed and encrypted data using public-key cryptography. Operations like calling a user or listening for incoming calls are coordinated via entries into the DHT as described in the rather terse technical overview on the Ring wiki. In addition, there is more information about OpenDHT in an SFL blog post.
There is also an experimental blockchain-based name server. This "RingNS" server uses the Ethereum blockchain and maps a username to a RingID, which is what identifies a Ring user. The RingID is an SHA-1 fingerprint of the public key of the user. The RSA key pair for the user must be at least 4096 bits long. A bit more information about the use of the blockchain can be found in a blog post from November 2016. That was a busy month for the project, as it became an official GNU package and released its second beta version then.
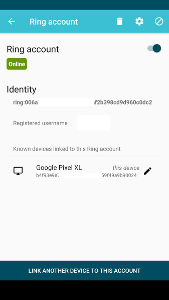
The RingIDs are not public, so users must exchange them (or usernames associated with them) in order to communicate. The RingID provides anonymity, if desired, as well as privacy, since a user cannot be contacted without using that ID. For users that don't have (or don't want) usernames, the Android app offers a QR-code mechanism to avoid exchanging 40 hex digits. The QR code can be scanned by an associate or the ID can be entered by hand.
I tested the Android app with a certain grumpy editor that I know. The text messaging function worked well, if a bit slowly, once we had established connectivity via our usernames. Video and audio calling, on the other hand, were not functional at all—a bit of video or a still image would occasionally slip through, but audio never made it. The "1.0" version number may be a bit misleading at this point.
Contributions are welcome, of course. The source code is managed in a Gerrit instance, but is also mirrored in the SFL GitHub repositories. There is also a mailing list for those interested.
There are official downloads available for Linux and Android, though the Google Play Store (or F-Droid once it gets updated) may be simpler for Android. Packages for Debian 9, three Ubuntu releases (16.04, 17.04, and 17.10), and two Fedora releases (25 and 26) are available. The community has contributed packages for Arch Linux and openSUSE, as well. Beyond that, packages for Windows (7, 8, 8.1, and 10) and macOS (10.10 and higher) are available too. Notably, there is no iOS version, nor any mention of why; it may be due to the GPLv3 license not being particularly welcome in Apple's app store.
As with other communication (and social networking) applications, the network effect is an important consideration. If the person you are trying to reach is not using Ring, it will be impossible to do so securely using the app (though it does have unencrypted SIP capability). Ring is also fairly new and has not been studied thoroughly (yet, hopefully), so any privacy claims are premature. It is nice to see a free software, privacy-focused communication tool, however; it certainly has the potential to be an important piece of the free-software toolbox.
| Index entries for this article | |
|---|---|
| Security | Encryption/Messaging |
The LWN site is currently under high scraper load, so comment display has been suppressed for anonymous users. If you are a human, you may read the comments by clicking the button below:
Note: you can avoid this step in the future by logging into your LWN account.