

Security
Web application scanning with skipfish
Web application security flaws are, as always, a hot area in security research, and it isn't surprising that a company which derives much of its income from the web would be interested in helping to secure it. Google has released several tools over the past couple of years—along with a Browser Security Handbook—many of which have been written by longtime security researcher Michal Zalewski. His latest release, skipfish, is an automated web application scanner that actively probes to find vulnerabilities.
Skipfish is a high-performance tool that can do several hundred to several thousand requests per second. Each of those requests tests a different kind of potential security flaw in an application. It spiders a web application and tries its tests on each of the pages it finds. For any complicated application, that will result in huge numbers of requests—and probably errors—but because of the post-processing it does to its results, it summarizes the reported problems in a fairly manageable way.
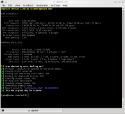
The code itself is 12,000 lines of C, which builds from a simple make as long as libidn is available to handle internationalized domain names. The program is command-line driven with top-like, continuously updating output (seen at right). Zalewski made some odd choices for colors in that output, making it hard to find a terminal color-scheme where it was readable. The recommended 100x35 terminal size is decidedly non-standard as well. Those nits aside, it is quite easy to get started with skipfish.
Understanding what one should do with skipfish is another story entirely. There is a large number of tests that are run, which are listed on the documentation page. That page also provides some examples of using the tool. As one might guess, there are a large number of options to handle different application needs like cookie values, HTTP authentication credentials, logout URLs to avoid, and so on. Before getting to that point, though, one must choose a dictionary.
Dictionaries in skipfish provide a starting point for the scanner to find additional URLs, files, and parameters that are used by the web application. There are four different dictionaries distributed with skipfish (minimal, default, extensions-only, and complete), and the tool will add what it learns to the dictionary as it runs. The dictionaries/README-FIRST file describes each dictionary as well as how the dictionaries are used. The minimal.wl dictionary is suggested as a good, lightweight starting point for skipfish experimentation.
And one gets the sense that a lot of experimentation will be required before any kind of skipfish-mastery is achieved. That said, a fairly short run of skipfish against a local development version of a reasonably complex web application turned up several obvious, though relatively minor, problems. There is also quite a bit more to go through in the report, so there are likely more problems awaiting discovery in even a small sample of skipfish's capabilities. One note of warning for those that have their application email with significant errors: either disable that, or you may get a chance to stress your mail server and/or be subjected to an inbox denial-of-service.
The report that skipfish produces is a summary of the problems, or
potential problems that it found. It is in HTML format, that, somewhat
amusingly, requires Javascript to be turned on to be useful. In fact, the
"known
issues" page mentions that due to "important security
improvements
" in Safari and Chrome, neither of those browsers will
display the report via the file: protocol—"put the report in a local WWW root and navigate to http://localhost/... instead; or use Firefox
".
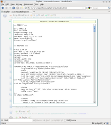
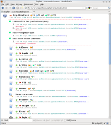
In the report, various categories of problems found are listed with color-coded icons to estimate the severity of the problem. Categories can be clicked on which will expose a list of the pages that exhibited the problem. For each of those, an HTTP trace can be examined (example shown at left). While some of the categories are fairly obvious, some are a bit more obscure and will require some investigation to determine whether there is truly a problem or not.
Like most, if not all, automated scanners, there will be plenty of false-positives reported, which means that the results will have to be sifted to find the real problems. Skipfish is aimed at minimizing false-positives, but it will still require an iterative approach. Limiting the search to the "interesting" parts of the application, without missing something important in the portions deemed "unimportant" will be somewhat tricky to get right.
Most web applications have vast numbers of pages that are governed by the same underlying code, so picking a truly representative sample of one of those pages is important. Otherwise, skipfish will spend an awful lot of time repetitively testing the same kinds of things against "/ExampleContent/1", "/ExampleContent/2", and so on. The same problem exists for any automated web scanner, of course.
As the documentation points out, there are other tools that do similar jobs
(Nikto and Nessus are given as examples), and
skipfish is "not a silver bullet
". But, clearly a lot of
thought has gone into it, and Zalewski has an excellent track record as
a finder of security vulnerabilities. Skipfish is certainly a tool that is
worth a long look.
Brief items
Mozilla: Plugging the CSS History Leak
The Mozilla security blog discusses their response to the leaking of browser history information via CSS link styling. "First of all, we're limiting what types of styling can be done to visited links to differentiate them from unvisited links. Visited links can only be different in color: foreground, background, outline, border, SVG stroke and fill colors. All other style changes either leak the visitedness of the link by loading a resource or changing position or size of the styled content in the document, which can be detected and used to identify visited links."
New vulnerabilities
brltty: privilege escalation
| Package(s): | brltty | CVE #(s): | CVE-2008-3279 | ||||||||
| Created: | March 31, 2010 | Updated: | April 19, 2010 | ||||||||
| Description: | The brltty daemon has an insecure library search path built into the the executable, allowing a local attacker who applies sufficient social engineering to run code as another local user. | ||||||||||
| Alerts: |
| ||||||||||
emacs: symlink race
| Package(s): | emacs22, emacs23 | CVE #(s): | CVE-2010-0825 | ||||||||||||
| Created: | March 30, 2010 | Updated: | August 30, 2010 | ||||||||||||
| Description: | From the Ubuntu advisory:
Dan Rosenberg discovered that the email helper in Emacs did not correctly check file permissions. A local attacker could perform a symlink race to read or append to another user's mailbox if it was stored under a group-writable group-"mail" directory. | ||||||||||||||
| Alerts: |
| ||||||||||||||
fcron: symlink attack
| Package(s): | fcron | CVE #(s): | CVE-2010-0792 | ||||||||||||
| Created: | March 29, 2010 | Updated: | January 1, 2014 | ||||||||||||
| Description: | From the CVE entry:
fcrontab in fcron before 3.0.5 allows local users to read arbitrary files via a symlink attack on an unspecified file. | ||||||||||||||
| Alerts: |
| ||||||||||||||
gnutls: arbitrary code execution
| Package(s): | gnutls | CVE #(s): | CVE-2010-0731 | ||||||||||||||||
| Created: | March 25, 2010 | Updated: | August 2, 2010 | ||||||||||||||||
| Description: | From the Red Hat advisory: A flaw was found in the way GnuTLS extracted serial numbers from X.509 certificates. On 64-bit big endian platforms, this flaw could cause the certificate revocation list (CRL) check to be bypassed; cause various GnuTLS utilities to crash; or, possibly, execute arbitrary code. (CVE-2010-0731) | ||||||||||||||||||
| Alerts: |
| ||||||||||||||||||
kernel: denial of service
| Package(s): | kernel | CVE #(s): | CVE-2010-0727 | ||||||||||||||||||||||||||||||||||||||||||||||||
| Created: | March 25, 2010 | Updated: | September 1, 2010 | ||||||||||||||||||||||||||||||||||||||||||||||||
| Description: | From the Mandriva advisory: The gfs2_lock function in the Linux kernel before 2.6.34-rc1-next-20100312, and the gfs_lock function in the Linux kernel on Red Hat Enterprise Linux (RHEL) 5 and 6, does not properly remove POSIX locks on files that are setgid without group-execute permission, which allows local users to cause a denial of service (BUG and system crash) by locking a file on a (1) GFS or (2) GFS2 filesystem, and then changing this file's permissions. (CVE-2010-0727) | ||||||||||||||||||||||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||||||||||||||||||||||
kernel: multiple vulnerabilities
| Package(s): | kernel | CVE #(s): | CVE-2010-1083 CVE-2010-1086 CVE-2010-1088 | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Created: | March 30, 2010 | Updated: | October 8, 2010 | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Description: | From the SUSE advisory:
CVE-2010-1083: A kernel information leak using user space USB devices could be used by local attackers with USB access to read recently freed kernel memory. CVE-2010-1086: A ULE decapsulation denial of service problem in DVB drivers was fixed that could be triggered by invalid DVB data packets. CVE-2010-1088: A NFS denial of service by following "automount" symlinks was fixed. | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
kvm: denial of service
| Package(s): | kvm | CVE #(s): | CVE-2010-0741 | ||||||||||||||||
| Created: | March 31, 2010 | Updated: | June 4, 2010 | ||||||||||||||||
| Description: | A flaw in how QEMU-KVM handles erroneous data allows a remote attacker to crash a guest system by sending specially-crafted data. | ||||||||||||||||||
| Alerts: |
| ||||||||||||||||||
moin: cross-site scripting
| Package(s): | moin | CVE #(s): | CVE-2010-0828 | ||||||||||||||||||||
| Created: | March 31, 2010 | Updated: | June 14, 2010 | ||||||||||||||||||||
| Description: | The moin wiki system suffers from a cross-site scripting vulnerability in its "Despam" action. | ||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||
moodle: cross-site scripting
| Package(s): | moodle | CVE #(s): | |||||||||
| Created: | March 29, 2010 | Updated: | March 31, 2010 | ||||||||
| Description: | From the Red
Hat bugzilla:
An XSS flaw was reported in the phpCAS library, where it would not properly sanitize the submitted URL before displaying it on the error page. This could allow an attacker to insert scripts or other malicious content on the error page. | ||||||||||
| Alerts: |
| ||||||||||
Mozilla products: multiple vulnerabilities
| Package(s): | firefox seamonkey thunderbird | CVE #(s): | CVE-2010-0174 CVE-2010-0175 CVE-2010-0176 CVE-2010-0177 CVE-2010-0178 CVE-2010-0179 | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Created: | March 31, 2010 | Updated: | January 27, 2011 | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Description: | The Firefox 3.0.19 and 3.5.9 (3.0.19 being the final planned 3.0.x update), Thunderbird 3.0.4, and SeaMonkey 2.0.4 updates fix a number of vulnerabilities. | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
openssl: multiple vulnerabilities
| Package(s): | openssl | CVE #(s): | CVE-2009-3245 CVE-2010-0433 | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Created: | March 25, 2010 | Updated: | April 12, 2011 | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Description: | From the Red Hat advisory: It was discovered that OpenSSL did not always check the return value of the bn_wexpand() function. An attacker able to trigger a memory allocation failure in that function could cause an application using the OpenSSL library to crash or, possibly, execute arbitrary code. (CVE-2009-3245) A missing return value check flaw was discovered in OpenSSL, that could possibly cause OpenSSL to call a Kerberos library function with invalid arguments, resulting in a NULL pointer dereference crash in the MIT Kerberos library. In certain configurations, a remote attacker could use this flaw to crash a TLS/SSL server using OpenSSL by requesting Kerberos cipher suites during the TLS handshake. (CVE-2010-0433) | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
sendmail: message spoofing
| Package(s): | sendmail | CVE #(s): | CVE-2006-7176 | ||||
| Created: | March 31, 2010 | Updated: | March 31, 2010 | ||||
| Description: | From the Red Hat advisory: the configuration of sendmail in Red Hat Enterprise Linux was found to not reject the "localhost.localdomain" domain name for email messages that come from external hosts. This could allow remote attackers to disguise spoofed messages. | ||||||
| Alerts: |
| ||||||
trac: unauthorized ticket modification
| Package(s): | trac | CVE #(s): | |||||||||
| Created: | March 30, 2010 | Updated: | March 31, 2010 | ||||||||
| Description: | From the Trac
changelog:
Trac 0.11.7 fixes a ticket validation issue that would allow unauthorized users to modify the status and resolution of a ticket. | ||||||||||
| Alerts: |
| ||||||||||
Page editor: Jake Edge
Next page:
Kernel development>>