

LWN.net Weekly Edition for September 18, 2008
LPC: Fitting into the kernel ecosystem
The first Linux Plumbers Conference started on September 17, 2008; the opening talk was a keynote by Greg Kroah-Hartman. He got the conference going with with a provocative sermon on how the development ecosystem works and the niche we all occupy within it. It was a fun talk - unless you happen to work for Canonical.He started with an apology to Canonical, though. In earlier talks, he had said that only eight kernel patches had ever come from Canonical. In fact, he has been corrected; the proper number is 100.
So, Greg asked, why is he picking on Canonical? His answer came in the form of a table of contributors to the kernel. It looked like this:
Distributor Changesets Red Hat 11,846 Novell 7,222 MontaVista 1,074 Debian 288 Gentoo 229 Mandriva 237 Wind River 207 rPath 186 Canonical 100
Then Greg asked: does anybody from Canonical want to say anything? Nobody did.
 Moving on to the Linux ecosystem. Greg put up a slide showing the larger
components of this ecosystem - the low-level stuff that makes Linux what it
is. Some of the largest components, beyond the kernel, were GCC,
binutils, X.org, and the man pages distribution. Looking at lines of
code, the kernel amounts to about 40% of the total. Other large components
are all significantly smaller.
It turns out that Greg has been doing repository data mining in a number of projects beyond the kernel. So, for projects like GCC, X.org, and binutils, he was able to put up tables listing the top contributors. The results varied somewhat, but there were a number recurring themes. Red Hat tends to be toward the top of the list on all of these projects; companies like IBM and Novell also appear regularly. CodeSourcery is a significant contributor to GCC and binutils. The U.S. National Security Agency contributes 2.1% of the patches into X.org; why is not clear. In all of these projects there are significant contributions from unpaid developers, but those contributions are overshadowed by those from paid developers.
And Canonical is always at the bottom of the chart - if it is there at all.
At this point Greg moved to a whiteboard to present his view of how the community works. At the development level, you have developers contributing to projects, which then release the code. There may be a few users at that level who feed back information (and maybe patches), but, in general, the biggest consumers of the project's releases are the distributors.
Distributors package everything and provide it to their users. At this point, another feedback loop comes into play: users feed their experiences and problems back to the distributor. Those distributors will respond to the user feedback, improving their products. The amount of feedback from the distributors to the upstream projects varies, but it tends to be small. For enterprise distributions, it is quite small; they are running ancient versions of everything and have little to do with current upstream. The community-oriented distributions, such as Fedora or openSUSE, tend to feed more changes back to their upstream sources.
Then, there is the matter of redistributors who base their products on another distributor's work; these are distributors like Ubuntu or CentOS. There are no contributions back to the community from that kind of distributor at all. They are not functioning as a part of the Linux ecosystem.
Greg finished up with what appears to be the message he came to the Linux Plumbers Conference to deliver: if you are a developer, if you want to be a part of the ecosystem, and if you work for a non-contributing company: quit. There are plenty of companies that understand the ecosystem and which need good people; at least one company, it seems, had wanted to set up a recruiting table at the conference. It is a very good time for people with community participation skills; there is no reason for anybody who wants to work in the community to stay on the outside.
[As a postscript, it is amusing to note that, while the conference did not allow companies to set up recruiting tables, nobody has prevented prospective employers from filling a prominently-placed whiteboard with information about available positions.]
Firefox 3 EULA raises a ruckus
End User License Agreements—or EULAs—are a mainstay of the proprietary software world that tend to rub free software advocates the wrong way. When a EULA is presented in a click-through window as part of the initial execution of a program, it can really raise some ire as Mozilla is finding out. Its plan to present a click-through license for Firefox 3 on Linux has not met with widespread approval; quite the reverse in fact.
The issue has been kicking around since at least last May, when Fedora folks noticed that Firefox 3 builds moved the EULA popup window from the installer—which Linux folks rarely see—to the first time Firefox is run. More recently the issue erupted in the Ubuntu community when a user filed a bug that reads, in part:
The predictable outcry followed, mostly because people who are used to free software have a visceral reaction to seeing a click-through EULA. For that reason alone it is a poor choice by Mozilla, at least on Linux. Windows users, who make up a substantial portion of the Firefox userbase, are generally unfazed by EULAs as they are confronted by them regularly—generally blithely clicking through with little or no hesitation.
There are a number of objections to the Mozilla EULA, starting with the current
text of the license. Mozilla Corporation chairperson Mitchell Baker agreed
with the critics of the license text, saying "the most important
thing here is to acknowledge that yes, the content of the license
agreement is wrong.
" New
license text is now available in draft form, but it still doesn't
address an underlying issue: do we need to consult a lawyer when we install
or run
free software?
One of the guiding principles of free software is that it doesn't limit what "end users" can do with the software, it only limits those who wish to distribute it. When a page or two of legalese—undoubtedly toned down from what the lawyers would really like—is presented to a new user, what exactly are they supposed to do with it? Users have rights under free software licenses, and it is important that they can find out about them, but it is fairly rare for a program, or even a distribution, to require a user to click through a copy of the license.
Mozilla's position is that they need to protect their trademarks as well as inform users about the web services used to try to detect phishing and malware sites. In answer to those who think a click-through EULA is unnecessary—often using Linux distributions as a counterexample—Baker points out:
So far, Mozilla does not seem willing to budge from its requirement to show the EULA as a click-through agreement. Fedora was able to get a waiver of sorts for Fedora 9 which allowed shipping Firefox 3 without the EULA while the projects worked out language they both could live with. In Fedora 9, Firefox opens to a page that describes the web services when it is run for the first time. Some kind of compromise along these lines for Linux distributions would seem to satisfy most of the concerns for both sides, but other than for Fedora 9, that solution has not been blessed by Mozilla.
Fedora Engineering Manager Tom "spot" Callaway has an excellent overview of the history as well as a nice analysis of the EULA. He notes that almost of all of the terms in the EULA are either covered by applicable laws or by the Mozilla Public License (MPL). None of that really matters though as distributions really only have two choices as outlined by Ubuntu leader Mark Shuttleworth:
That is the risk that Mozilla takes; if it is too heavy-handed in what it requires to call a browser "Firefox", distributions will take the code without the trademarks and call it "Iceweasel" as Debian has or "abrowser" which is the Ubuntu equivalent. The Iceweasel "fork" was made because Mozilla objected to Debian backporting security fixes into older browsers without its consent, while abrowser has come about because of the EULA issue. Given that Linux users were some of the earliest and most enthusiastic adopters of Firefox, it is truly unfortunate that many may have to run it under other names.
There is an issue that may be getting lost in the shuffle here as well. Fedora board member Jef Spaleta has expressed concerns about how to notify users about web services:
Web services clearly bring along a number of additional concerns. There are privacy issues to consider. In many places, particularly Europe, there are fairly stringent requirements regarding data collection and retention that are required to be communicated to users. How that will be done for free software that use these services is an open question. As Spaleta points out, Mozilla may be the only free software organization that is even looking at the problem.
The EULA mess is a situation that certainly could have been handled better by Mozilla. One hopes that some kind of compromise can be worked out so that users aren't poked in the eye with legal documents—that aren't even valid in many jurisdictions—and distributions don't feel like they need to fork to preserve their freedoms. Mozilla definitely has some legitimate interests to protect, but it needs to find a saner way to do that.
There is hope that is happening as Baker has described in an update on her blog:
More details are imminent, but it looks like this could all resolve amicably.
Review: Intellectual Property and Open Source
Free software inevitably runs into the body of law known collectively as "intellectual property." Many developers do their best to avoid the legal side of things whenever possible; others seem to like nothing better than extended debates on the topic. Regardless of one's own feelings in the matter, the fact remains that the legal system exists, it affects our lives, and that we can only be better off if we understand it. To that end, O'Reilly has published Intellectual Property and Open Source by Van Lindberg.The book starts off with a Lessig-like comparison between code intended for computers and legal code. The legal code base is not as clean as one might like:
Mr. Lindberg is clearly trying to write for programmers, so code-based analogies abound. Patents are like regular expressions - quite powerful in the technologies they can match, but you never really know what they will catch until you try them. Patent documents are structured like ELF program headers, and the patent system as a whole is a sort of memorization scheme (we get a Python Fibonacci number generator as an example here). Contracts are like a distributed version control system - they let anybody create their own, localized law. And so on.
 Roughly the first half of the core part of the book is dedicated to
explaining how the four main branches of intellectual property (patents,
copyright, trademarks, and trade secrets) work. The chapter on the patent system notes
some of the problems with software patents (in particular, the
industry's use of oral tradition and the late recognition of software patents makes most prior
art invisible to investigators), but, to a great extent, it seems to be
written for people who want to obtain patents, rather than those who feel
the need to defend themselves against software patents. It might have been
nice to get a treatment of the often-quoted idea that software developers
are better off not knowing about patents because that way they cannot be
accused of willful infringement, but that topic was not touched. There is
also no talk of the Open Invention Network or any other efforts to protect
the community as a whole.
The copyright chapter is a reasonably thorough treatment of the subject which notes how the scope of copyright has expanded over the years. The current situation is compared to an "allow by default" security policy where anything which can be said to have an expressive aspect gets copyright protection by default. Derivative works are discussed at length, leading to this interesting observation:
Just a few pages earlier, it is stated that joint ownership means that each author has full rights over the entire work and can do just about anything with it - like license it to others. A finding that the kernel was a joint work could lead to some unpleasant consequences; one hopes that Mr. Lindberg is not really saying that could happen.
The book mentions the abstraction-filtration-comparison test used by some courts to determine if one body of code is derived from another, but says nothing about how that test works. It would have been nice to learn a bit more, since that is an important part of how copyright cases are resolved in the US. Also nice would have been some discussion of the value of registration of copyrights.
The chapter finishes with this discouraging note:
The discussion of trademarks (compared to desktop shortcut icons) is pretty much as one would expect. The chapter is more concerned with obtaining and defending trademarks than balancing trademarks against the ideals of free software. There is not much to say about trade secrets, though the chapter does touch on what happens if unreleased code is incorporated into a free application. The author concludes that the open development process makes this kind of contamination less likely than with proprietary projects.
Next we move into a chapter on contracts and licenses which talks mostly about how contracts are formed and enforced. The book takes a strong position that all licenses are contracts; they are just a special form of contract which grants permission to use some sort of intellectual property. The other point of view (that licenses are distinct from contracts) is touched upon, but dismissed this way:
Later on, the author refers to the GPL in particular as a "Schrödinger's license" with a currently undetermined nature; it might be "just a license" after all. Clearly there is some confusion on this point. It is worth noting that the book predates the appeals court decision in the JMRI case, which makes the "it's a license" interpretation far more likely.
There is a chapter on the "economic and legal foundations of open source," talking about how the community works and, in particular, how free licenses work. There is little here which would be new to most LWN readers, but it might be good to hand to the corporate legal office. Speaking of that office, the next chapter talks about how to contribute to a project without getting into trouble with your employer. There is talk about proprietary information agreements, some important cases (including the Medsphere case, which you editor wishes had been more prominent on his radar), works for hire, and so on. The key advice from the author is to disclose your work and your ideas to your employer as soon as possible - preferably before beginning employment. This is a chapter that many free software developers should read.
Chapter 10 is about choosing a license for a free software project. The importance of the topic is stressed - as is the importance of not trying to write one's own license. The author recommends that most projects should limit themselves to considering the 2-clause BSD license, the Apache license (v2), the Mozilla Public License, the GPL or LGPL (versions 2 or 3, though GPLv3 is said to be "a better and surer foundation for future development"), or the Open Software License (v3).
Chapter 11 is about the issues involved in accepting patches from others. The author strongly recommends using some sort of signed contributor agreement or even copyright assignments. Getting assignments, he says, allows for "unified legal control," ease of relicensing, and the ability to do commercial licensing. It's probably good advice for a strongly corporate-controlled project, but may not fit with more community-oriented projects. Unfortunately, the book perpetuates this particular fiction:
And, to make it worse:
There are a few problems here. No single entity owns the entire Linux kernel, but that code has been quite vigorously defended against some strong legal challenges. (It is interesting, actually, that the author managed to write this entire book without mentioning SCO once.) Kernel developers have also been able to enforce the kernel's copyright numerous times. Meanwhile, a quick look at the BusyBox code is sufficient to turn up copyright assertions from far more than two developers. Unified ownership of a code base may be the right thing for some projects, but the reasons cited here are clearly not applicable.
That complaint notwithstanding, this chapter does contain useful information that should be kept in mind when accepting patches from others.
Chapter 12 is about the GPL in particular. There is a lot of talk about just what is a derived work under the GPL - does it apply to kernel modules, for example? Unfortunately, the answer is "we just don't know." So, while the chapter is a reasonable summary of how the GPL works, once again there will be little there for most LWN readers.
Chapter 13 gets into reverse engineering, providing a quick overview of how it can be done without getting into trouble. According to the book, reverse engineering is generally allowed in the US, even to the point of disassembling proprietary code to learn its secrets. There are a lot of pitfalls, though, and the DMCA changes the game significantly. This chapter is a good starting point, but anybody wanting to do reverse engineering in the US will probably want to learn rather more than what is on offer here.
The final chapter talks about the creation of a non-profit corporation to own and/or manage a code base. It's mostly about what's required to create a corporation and keep it in good standing. This information may be useful to some, but it seems a little out of place here. After that, there are 80 pages of license lists and the full texts of a number of free software licenses. Perhaps it's useful reference material, but it's all easily available online; it's not clear that dedicating nearly 25% of the book to this material was necessary.
The subtitle of this book is "a practical guide to protecting code," which makes one omission especially striking: there is not a word on how a project should deal with license violations. There is, by now, a fair amount of collective wisdom on how such problems should be approached, but it has not been collected here. There's also little talk on protecting projects against software patent problems, no talk of patent pools, and no talk of related issues like the Microsoft/Novell deal. Software patents have cast a big shadow over free software in the US, but the issue is not really touched upon in this book.
It is also worth noting that the book is very heavily based on US law, and the author never attempts to look beyond the border. Certainly it would never have been possible to cover intellectual property law worldwide, but this narrow focus is still a little puzzling. Much intellectual property law in the US is based on international agreements, so an understanding of those agreements would help with the larger picture. A mention of Berne Convention would not have been out of place, for example. The other problem is that free software tends to have little respect for borders; there are few projects which are limited to a single country. Even if a project is based in the US, the existence of contributors elsewhere in the world is almost certain. Free software is a global phenomenon; it is not sufficient to think about US law alone.
Despite these complaints, your editor has to say that this is a valuable book. It covers many of the basics of the law in a much clearer way than has been done before. Anybody who manages or contributes to a free software project (in the US, at least) should be familiar with the concepts discussed here. And certainly all of the people peppering the net with IANAL posts would be better informed after reading Intellectual Property and Open Source. This book should bring some light to a complex but crucially important part of the legal code which governs our actions, and that is a good thing.
Security
OpenSSH and keystroke timings
Theoretical security weaknesses have a tendency to move from the realm of theory to that of practice over time. Sometimes it is the result of more compute power being applied or better algorithms being developed, but a weakness is certainly not going to get stronger. So when Kevin Neff started discussing fixing a weakness in OpenSSH on the openbsd-misc mailing list, the folks writing it off as "theoretical" may have been jumping the gun.
When it is in interactive mode—a user typing into a terminal session for example—ssh sends each key pressed by the user in a separate packet. By observing the timing between packets, an observer may be able to determine something about what was typed just by using traffic analysis, without attempting to break the encryption. Researchers found that the inter-packet timing correlated well with the inter-keystroke timing, so that using statistical techniques they were able to reduce the search space for cracking a password by a factor of 50.
This weakness was outlined in a 2001 paper entitled Timing analysis of keystrokes and timing attacks on SSH" [PDF] which looked specifically at the timing-based attack:
The paper looked at the now-deprecated SSH1 protocol, which led some to conclude that it substantially invalidated the weakness. Damien Miller pointed out that it was likely to still be valid:
Pointing at the paper and discounting it because it is ssh1 only is sticking your head in the sand. It is usually easier to research attacks on simpler protocols and work up to more complicated ones later.
There is a fair amount of information that can be gleaned just by looking at the traffic generated over an encrypted session, especially if the attacker can gather a sizable amount of it. There are fairly clear patterns in interactive sessions that can be extracted and used alongside the inter-keystroke timing information to potentially garner lots of useful information. Darrin Chandler describes it this way:
Overall, the reception to making OpenSSH less susceptible to this kind of analysis was positive. It is clearly a difficult attack to mount, logistically if nothing else, but it is not impossible either. Better timing information or analysis techniques might make it easier over time as well and that is enough of a reason to look at ways to fix it.
Brief items
NoScript 1.8.1 and LWN logins
We have received several reports of readers being unable to log in to LWN.net this morning. It appears to be related to upgrading the NoScript Firefox plugin to version 1.8.1. A new feature, called "Automatic Secure Cookie Management", appears to interact badly with LWN's login code. Some workarounds are described in the FAQ. We apologize for any inconvenience.
Update: Peter Palfrader reports that whitelisting lwn.net for "unsafe" https cookies in NoScript Options -> Advanced - HTTPS -> Cookies -> Enable Automatic Secure Cookies Management fixes the issue.
New vulnerabilities
apache2: cross-site scripting
| Package(s): | apache2 | CVE #(s): | CVE-2008-2939 | ||||||||||||||||||||||||||||||||
| Created: | September 15, 2008 | Updated: | December 5, 2008 | ||||||||||||||||||||||||||||||||
| Description: | From the Mandriva advisory: A cross-site scripting vulnerability was found in the mod_proxy_ftp module in Apache that allowed remote attackers to inject arbitrary web script or HTML via wildcards in a pathname in an FTP URI (CVE-2008-2939). | ||||||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||||||
ipa: remote password exposure
| Package(s): | ipa | CVE #(s): | CVE-2008-3274 | ||||||||||||
| Created: | September 11, 2008 | Updated: | September 17, 2008 | ||||||||||||
| Description: | From the Red Hat alert: A flaw was found in the Red Hat Enterprise IPA installation procedure. The master Kerberos password was set up in the LDAP server in such a way that it was possible to retrieve the password via an anonymous LDAP connection. | ||||||||||||||
| Alerts: |
| ||||||||||||||
kernel: integer overflow
| Package(s): | kernel | CVE #(s): | CVE-2008-3276 | ||||||||||||||||||||||||||||||||
| Created: | September 11, 2008 | Updated: | November 5, 2008 | ||||||||||||||||||||||||||||||||
| Description: | From the SUSE alert: An integer overflow flaw was found in the Linux kernel dccp_setsockopt_change() function. An attacker may leverage this vulnerability to trigger a kernel panic on a victim's machine remotely. | ||||||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||||||
kernel: multiple vulnerabilities
| Package(s): | linux-2.6.24 | CVE #(s): | CVE-2008-3526 CVE-2008-3534 CVE-2008-3535 CVE-2008-3792 CVE-2008-3915 | ||||||||||||||||||||
| Created: | September 12, 2008 | Updated: | November 3, 2008 | ||||||||||||||||||||
| Description: | From the Debian advisory:
CVE-2008-3526: Eugene Teo reported a missing bounds check in the SCTP subsystem. By exploiting an integer overflow in the SCTP_AUTH_KEY handling code, remote attackers may be able to cause a denial of service in the form of a kernel panic. CVE-2008-3534: Kel Modderman reported an issue in the tmpfs filesystem that allows local users to crash a system by triggering a kernel BUG() assertion. CVE-2008-3535: Alexey Dobriyan discovered an off-by-one-error in the iov_iter_advance function which can be exploited by local users to crash a system, resulting in a denial of service. CVE-2008-3792: Vlad Yasevich reported several NULL pointer reference conditions in the SCTP subsystem that can be triggered by entering sctp-auth codepaths when the AUTH feature is inactive. This may allow attackers to cause a denial of service condition via a system panic. CVE-2008-3915: Johann Dahm and David Richter reported and issue in the nfsd subsystem that may allow remote attackers to cause a denial of service via a buffer overflow. | ||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||
kolab-server: password disclosure
| Package(s): | kolab-server | CVE #(s): | |||||
| Created: | September 15, 2008 | Updated: | September 17, 2008 | ||||
| Description: | From the Mandriva advisory: Gavin McCullagh of Griffith College Dublin reported an issue in Kolab v1 where user passwords were being recorded in the Apache log files due to Kolab using HTTP GET requests rather than HTTP POST requests. This would allow any users with access to the Apache log files to harvest user passwords and possibly other sensitive data. | ||||||
| Alerts: |
| ||||||
libxml2: denial of service
| Package(s): | libxml2 | CVE #(s): | CVE-2003-1564 | ||||||||||||||||
| Created: | September 11, 2008 | Updated: | December 4, 2009 | ||||||||||||||||
| Description: | From the Red Hat alert: A denial of service flaw was found in the way libxml2 processed certain content. If an application linked against libxml2 processed malformed XML content, it could cause the application to use an excessive amount of CPU time and memory, and stop responding. | ||||||||||||||||||
| Alerts: |
| ||||||||||||||||||
libxml2: buffer overflow
| Package(s): | libxml2 | CVE #(s): | CVE-2008-3529 | ||||||||||||||||||||||||||||||||||||||||
| Created: | September 11, 2008 | Updated: | August 11, 2009 | ||||||||||||||||||||||||||||||||||||||||
| Description: | From the Red Hat alert: A heap-based buffer overflow flaw was found in the way libxml2 handled long XML entity names. If an application linked against libxml2 processed untrusted malformed XML content, it could cause the application to crash or, possibly, execute arbitrary code. | ||||||||||||||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||||||||||||||
openssh: denial of service
| Package(s): | openssh | CVE #(s): | CVE-2008-4109 | ||||||||||||
| Created: | September 17, 2008 | Updated: | October 7, 2008 | ||||||||||||
| Description: | From the Debian advisory: It has been discovered that the signal handler implementing the login timeout in Debian's version of the OpenSSH server uses functions which are not async-signal-safe, leading to a denial of service vulnerability (CVE-2008-4109). The problem was originally corrected in OpenSSH 4.4p1 (CVE-2006-5051), but the patch backported to the version released with etch was incorrect. | ||||||||||||||
| Alerts: |
| ||||||||||||||
pam_mount: arbitrary mounting of filesystems
| Package(s): | pam_mount | CVE #(s): | |||||||||||||||||
| Created: | September 12, 2008 | Updated: | September 17, 2008 | ||||||||||||||||
| Description: | From the Fedora advisory: A security flaw in the pam_mount's handling of user defined volumes using the 'luserconf' option has been fixed in this update. The vulnerability allowed users to arbitrarily mount filesystems at arbitrary locations. | ||||||||||||||||||
| Alerts: |
| ||||||||||||||||||
postfix: denial of service
| Package(s): | postfix | CVE #(s): | CVE-2008-3889 | ||||||||||||||||||||||||||||
| Created: | September 11, 2008 | Updated: | November 4, 2008 | ||||||||||||||||||||||||||||
| Description: | From the Mandriva alert: A vulnerability in Postfix 2.4 and later was discovered, when running on Linux kernel 2.6, where a local user could cause a denial of service due to Postfix leaking the epoll file descriptor when executing non-Postfix commands. | ||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||
R-base: arbitrary file overwrite
| Package(s): | R-base | CVE #(s): | CVE-2008-3931 | ||||||||
| Created: | September 17, 2008 | Updated: | September 23, 2008 | ||||||||
| Description: | From the Mandriva advisory: A symlink vulnerability was found in the javareconf script in R that allows local users to overwrite arbitrary files (CVE-2008-3931). | ||||||||||
| Alerts: |
| ||||||||||
redhat-ds-base: multiple vulnerabilities
| Package(s): | redhat-ds-base | CVE #(s): | CVE-2008-2930 CVE-2008-3283 | ||||||||||||
| Created: | September 11, 2008 | Updated: | September 17, 2008 | ||||||||||||
| Description: | From the Red Hat alert:
Multiple memory leaks were identified in the Directory Server. An unauthenticated remote attacker could use these flaws to trigger high memory consumption in the Directory Server, possibly causing it to crash or terminate unexpectedly when the server ran out of available memory. (CVE-2008-3283) Ulf Weltman of Hewlett-Packard discovered a flaw in the way Directory Server handled LDAP search requests with patterns. A remote attacker with access to the LDAP service could create a search request that, when the search pattern was matched against specially crafted data records, caused Directory Server to use a large amount of CPU time. Directory Server did not impose time limits on such search requests. In this updated package, Directory Server imposes a configurable limit on the pattern-search query run time, with the default limit set to 30 seconds. (CVE-2008-2930) | ||||||||||||||
| Alerts: |
| ||||||||||||||
rsh: directory traversal
| Package(s): | rsh | CVE #(s): | CVE-2004-0175 | ||||
| Created: | September 12, 2008 | Updated: | September 17, 2008 | ||||
| Description: | From the CVE entry: Directory traversal vulnerability in scp for OpenSSH before 3.4p1 allows remote malicious servers to overwrite arbitrary files. NOTE: this may be a rediscovery of CVE-2000-0992. | ||||||
| Alerts: |
| ||||||
ssmtp: memory contents disclosure
| Package(s): | ssmtp | CVE #(s): | CVE-2008-3962 | ||||||||
| Created: | September 15, 2008 | Updated: | September 17, 2008 | ||||||||
| Description: | From the Red Hat bugzilla: The from_format function in ssmtp.c in ssmtp 2.62, in certain configurations, uses uninitialized memory for the From: field of an e-mail message, which might allow remote attackers to obtain sensitive information (memory contents) in opportunistic circumstances by reading a message. | ||||||||||
| Alerts: |
| ||||||||||
wireshark: multiple vulnerabilties
| Package(s): | wireshark | CVE #(s): | CVE-2008-3146 CVE-2008-3932 CVE-2008-3933 CVE-2008-3934 | ||||||||||||||||||||||||||||||||||||
| Created: | September 12, 2008 | Updated: | January 12, 2009 | ||||||||||||||||||||||||||||||||||||
| Description: | There are multiple buffer overflows in NCP dissector, an infinite loop in the NCP dissector, a crash could be triggered by zlib-compressed packet data, and also a crash via crafted Tektronix .rf5 file. | ||||||||||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||||||||||
wordnet: buffer overflows
| Package(s): | wordnet | CVE #(s): | CVE-2008-3908 | ||||||||
| Created: | September 16, 2008 | Updated: | October 7, 2008 | ||||||||
| Description: | From the CVE entry: Multiple buffer overflows in Princeton WordNet (wn) 3.0 allow context-dependent attackers to execute arbitrary code via (1) a long argument on the command line; a long (2) WNSEARCHDIR, (3) WNHOME, or (4) WNDBVERSION environment variable; or (5) a user-supplied dictionary (aka data file). NOTE: since WordNet itself does not run with special privileges, this issue only crosses privilege boundaries when WordNet is invoked as a third party component. | ||||||||||
| Alerts: |
| ||||||||||
wordpress: SQL column truncation
| Package(s): | wordpress | CVE #(s): | |||||||||
| Created: | September 12, 2008 | Updated: | September 17, 2008 | ||||||||
| Description: | WordPress 2.6.2 has been released to work around problems with SQL Column Truncation and the weakness of mt_rand(). See this advisory for more information. | ||||||||||
| Alerts: |
| ||||||||||
Page editor: Jake Edge
Kernel development
Brief items
Kernel release status
The current 2.6 development kernel is 2.6.27-rc6, released on September 9.
There have been numerous fixes merged into the mainline since 2.6.27-rc6, but with many kernel hackers including Linus off at the Kernel Summit, that may delay -rc7 somewhat.
No stable kernel releases have been made over the last week. 2.6.26.5 and 2.6.25.17 were both released September 7.
Kernel development news
Quote of the week
The 2008 Linux Kernel Summit
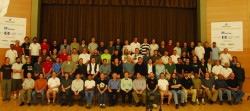
 The 2008 Linux Kernel Summit was held September 15 and 16 in
Portland, Oregon, immediately prior to the Linux Plumbers Conference. At
this invitation-only meeting, some 80 developers discussed a number of
issues relevant to the kernel and its future development. The following
reports were written by Jonathan Corbet, who attended the event and was a
member of its program committee.
This reporting was sponsored by LWN's subscribers; if you appreciate this kind of content, please consider subscribing to LWN and helping us create more of it.
Day 1
The sessions held on the first day were:
- Linux 3.0: should the developers
do a Linux 3.0 release with a focus on dumping older, unneeded code?
- Minisummit reports: reports from
gatherings of power management, wireless networking, and containers
developers.
- When should drivers be merged? A
wide-ranging discussion on the trade-offs between getting drivers into
the kernel quickly and waiting until they are up to kernel coding
standards.
- Filesystem and block layer
interaction; what contemporary file systems need to be able to get
the most out of storage devices.
- Cross-subsystem issues; how do we
evolve subsystems which are heavily used by several other parts of the
kernel?
- Tools, and the new Patchwork tool in
particular.
- Bootstrap code. Why does every
distributor throw together its own initrd/initramfs code, and can that
situation be improved?
- Kernel quality and release process, various discussions on how to produce better kernels and a near-decision to move to a one-week merge window.
Day 2
- Tracing. A lengthy discussion on
user requirements for kernel tracing and how those requirements might
eventually be met.
- Documentation. We always want more
and better documentation, but what documentation would be most useful
to the development community?
- There was a brief bug-fixing session aimed at the top entries on the
KernelOops.org. Over the course
of half an hour, the developers were able to fix 13 of the top 14
bugs. It was widely agreed that this was a productive use of time
which will probably be repeated at future events.
- More minisummit reports covering
virtualization, networking, and kernel bloat.
- All about threads; kernel thread pools
and threaded interrupt handlers in particular.
- Projects with large user-space
components; how can we make it easier for the direct rendering
infrastructure project to work with the mainline kernel?
- Rafael Wysocki led a section on the new suspend/resume
infrastructure. Most of that talk was concerned with the API, which
was covered here back in
March, so it will not be written up again now. Some changes will
likely be made; stay tuned to LWN for the details.
Linus did ask the crowd how many people were still unable to suspend their laptops. The number of hands raised was quite small; things have clearly gotten better in this area.
- Fixing the Kernel Janitors Project. How can we do a better job of bringing new developers into the kernel community?
The closing party (which was also the Linux Plumbers Conference opening party) was the venue chosen for the annual election of members to the Linux Foundation's Technical Advisory Board. The move out of the regular kernel summit sessions was intended to allow a wider group of people to participate in the election. It would appear to have been successful in that regard; there were record numbers of both candidates and voters. The board members elected this time around were James Bottomley, Kristen Carlson Accardi, Chris Mason, Dave Jones, Chris Wright, and Christoph Hellwig. Christoph was elected to a one-year term; all of the others will serve two-year terms.
Next year's kernel summit is currently scheduled for October 18 to 20 in Tokyo, Japan.
Patches and updates
Kernel trees
Core kernel code
Device drivers
Filesystems and block I/O
Security-related
Virtualization and containers
Benchmarks and bugs
Page editor: Jonathan Corbet
Distributions
News and Editorials
The openSUSE Project's first board elections
The openSUSE Project is about to hold it's first board election. The process is well underway, with the first phase nearly over. All members of the openSUSE project may vote and can run for the board positions, but there is a fast approaching deadline in which to register for this vote or to declare your intention to run for this election. In the last call for candidates, received a bit too late for last week's LWN issue, states that application deadline ends September 24th, 12:00 UTC.An election committee has been formed to oversee the elections. Four people, two from Novell and two from the community, will organize and oversee the election. Committee members Claes Backstrom, Andrew Wafaa, Marko Jung, and Vincent Untz have agreed not to run for this election so that they might remain impartial.
The initial openSUSE board was
appointed by Novell. Pascal Bleser, a member of that board, has written a
blog post about the openSUSE Board and the elections giving his view of
the what the board does and does not do. "One point that really must
be clarified (again) is that the Board is not responsible for taking
technical decisions. That's other people's job, e.g. AJ as the director of
openSUSE and platform, Coolo as the openSUSE distribution project manager,
or Michl as the openSUSE product manager.
" Pascal also has a followup
post answering some additional questions about the time commitments and
involvement expected of a board member.
Andreas Jaeger, also a member of the current board, has also written
about the board, how it's organized and what upcoming board members
might expect. "I'm part of the first openSUSE board and in my
opinion we're still bootstrapping it and forming it. Federico mentioned
that it took the GNOME board several years until they were really
functional - so this shaping of the board is not only in the openSUSE
project an evolutionary process that takes time and is influenced by
e.g. (constructive) criticism, praise, communication in general, and
decisions.
" New board members will be able to shape the board from
the inside. With a new board, community members can also help shape the
board with questions, comments and letting their expectations be known.
The board will consist of five members, a Novell appointed chairperson, two Novell employees and two community members (not employed by Novell). So far there are three Novell candidates and five non-Novell candidates. The list of candidates with pointers to their platforms can be found here.
We will soon be into the campaign period, which runs from September 25th to October 9th. During this time period will be blog entries from the candidates, interviews by the openSUSE news team, and a moderated Q&A session on IRC. There is also a feature in the openSUSE election in which each eligible voter may appoint a second openSUSE member to be eligible to vote. The option to appoint a second voter will be available during the campaign period and may allow a few people who missed the September 24th deadline to vote.
The actual election begins as the campaign period ends. Each eligible voter will be able to cast their votes once. No changes will be allowed. Votes will be stored anonymously in the electronic system. Ballots will be closed October 23rd, the winners announced once the election committee has had a chance to verify and count the votes.
If you care about the openSUSE project, this is a great time to get involved. Run for the board, vote in the election, and have a say in the shape of things to come.
New Releases
I: ALT Linux 4.0 Terminal
ALT Linux 4.0 Terminal has been released. The release notes are available in English. The release itself is available in English and Russian versions.CentOS 4.7 is released for i386 and x86_64
The CentOS development team has announced the release of CentOS 4.7 for i386 and x86_64. This is the seventh update to the 4.0 release and includes updates through September 12, 2008. Other architectures are still in progress.Introducing the Foresight Mobile Edition
The Foresight Linux Project has announced the first release of the Foresight Mobile Edition. "The Foresight Mobile Edition is the first release of Foresight for netbooks and ultra mobile PCs, such as the ASUS Eee PC, Intel Classmate, and Dell E netbook, and features a customized GNOME desktop optimized for smaller screens."
Lunar Linux 1.6.4-alpha3 released
Lunar Linux 1.6.4-alpha3 codename 'Lacus Autumni' is available for testing. "It has been a long wait, but finally a new release is in the works that will correct all the issues installing Lunar using the old ISO's. We have also decided to remove XOrg and XFCE that was available on the 1.6.2-beta2 release to shrink the ISO size a bit."
Syllable Server 0.3 released
Syllable Server 0.3 has been released. This is a new distribution, and the first release that focused on making the system actually usable as a server. "A number of popular servers were added and configured, and also several innovative REBOL software stacks. Out of the imaginary box, Syllable Server is now ready for such things as accepting remote SSH log-ins over the network, running a web server on the Cheyenne REBOL server, running an FTP server and several more." Syllable Server has been added to the General Purpose section of the list.
Distribution News
Debian GNU/Linux
Bits from the Debian GNU/Hurd porters
It has been three years since the last report, but the Debian GNU/Hurd project is moving along. Several releases have been made, the most recent was in December 2007. It would appear that many developers are using virtualization to the run the distribution: "Besides qemu, which can be very slow to run, a Xen DomU port for GNU Mach has been made available by Samuel Thibault. It requires a non-PAE hypervisor and some minor manual tweaking, but is otherwise quite functional and stable already, see its wiki page[4] for further information. This will make people running the Hurd less dependent on specific hardware, as a lot of newer computers do not work with the underlying GNU Mach kernel anymore." Click below for the full report.
report from the Emdebian/FAI Work Session in Extremadura 2008
The Emdebian (Embedded Debian) team met in Extremadura, Spain for discussion and bug fixing. Click below for the report.Call for testing of next Debian Installer release
The first release candidate of the Debian 5.0 (Lenny) installer is available for testing. "The installer has a lot of new and impressive features against last Etch release and Lenny beta 2. For a better view of the changes made on the installer since last beta, take a look on our release announcement draft. We are sure you are going to have a nice feeling about it. We count on you to help us!"
Distribution Newsletters
Misc Debian developer news (#10)
This issue of miscellaneous Debian developer news looks at PTS (Package Tracking System) news, a new machine for the MIPS porters, some personnel changes, people.debian.org moves to a new machine along with the delayed queue, and the Git user survey 2008.Fedora Weekly News, Issue 143
The Fedora Weekly News for September 7, 2008 is out. "This week Announcements trumpets the arrival of a new version of Bodhi, the freeze of Rawhide and some essential reading on the new package keys. In Developments we shock you with "Non-X System Consoles to be Removed". Virtualization alerts you to "Virt-manager 0.6.0 Released" and dives into how developers are "Laying the Groundwork for Xen Domain 0 Support". The ever entertaining Artwork beat examines "How to Select a Winning Theme" and SecurityAdvisories provides a handy list for your perusal."
OpenSUSE Weekly News/38
This issue of the OpenSUSE Weekly News covers the Last Call for openSUSE Board Candidates, openSUSE KDE Bug Squashing Days (20-21 September), Board election, openSUSE 11.0 survey, KDE in openSUSE 11.1 and beyond, and more.Ubuntu Weekly Newsletter #108
This week the Ubuntu Weekly Newsletter covers: Introducing Jaunty Jackalope, UI Freeze in place-Alpha 6 freeze ahead, Last push for Intrepid documentation, Ubuntu 9.04 Developer Summit Sponsorship, Status of Ubuntu Romanian Localization Team, Ubuntu Developer Week, MOTU, New Ubuntu Members, Intrepid Spanish Translation, New Ubuntu Cyclists Team, Atlanta Linux Fest 2008, Arizona LoCo participating in ABLEconf, Ohio Linuxfest, Berlin LoCo Bug Jams, Ubuntu-NI SFD 2008, Technical Board Meeting Summary, Server Team Meeting, and much more.DistroWatch Weekly, Issue 270
The DistroWatch Weekly for September 15, 2008 is out. "An issue largely dedicated to Ubuntu, our editorial looks at the increasingly assertive way Canonical handles its trademarks with relations to other Ubuntu-based distributions. In related news, Ubuntu debates ways to bypass a controversial Mozilla licensing requirement, Shuttleworth announces Ubuntu 9.04 "Jaunty Jackalope" with interesting innovations, and the Ubuntu Eee project launches a new product for the popular netbook from ASUS, incorporating a brand new desktop interface. Also in the news, openSUSE goes for a complete switch to KDE 4.x starting with version 11.2, Fedora announces the availability of package updates after a recent server crack, and Red Hat receives criticism from the Linux community over the lack of security information following the Fedora server compromise. Finally, if you are a translator or if you work in localising software applications, don't miss Linguas OS, a PCLinuxOS-based live CD that could greatly speed up your work."
Distribution reviews
OpenSolaris 2008.05 is robust and ready
Gary Sims reviews OpenSolaris 2008.05 on Linux.com. "OpenSolaris comes with some unique technologies, such as ZFS and DTrace, which can make it an attractive option for business. The Zetabyte File System (ZFS) is a powerful file system designed for high storage capacities. It goes beyond filesystems like ext3 and NTFS by combining a filesystem, volume management, and RAID into one package. DTrace is a system tracing tool that enables you to explore your system to understand how it works, track down performance problems across many layers of software, or locate the cause of aberrant behavior. You can learn more about it in the Solaris Dynamic Tracing Guide."
Page editor: Rebecca Sobol
Development
Audacity gets new functionality via Google Summer of Code
Audacity is a popular and award winning multi-track open-source and cross-platform audio editor project that is built on the wxWidgets GUI library. LWN looked at Audacity in 2006. The Audacity project announced its participation in the 2008 Google Summer of Code student code writing event on April 21, 2008. GSoC 2008 is wrapping up and the Audacity site notes the progress made this summer:
The Audacity GSoC projects page details the goals and achievements made by the students, we'll examine the results.
Руслан Ижбулатов
worked on adding FFmpeg support to Audacity in order to allow
importing and exporting of a wider variety of audio file types.
From the FFmpeg site:
"FFmpeg is a complete solution to record, convert and stream audio and video. It includes libavcodec, the leading audio/video codec library. FFmpeg is developed under Linux, but it can compiled under most operating systems, including Windows.
"
Audacity natively supports the WAV AIFF, MP3, Ogg Vorbis, and FLAC
formats, the FFmpeg library supports those, and adds support for the
GSM WAV, MP2, M4A (AAC), AMR, WMA, and many more formats.
The
Project Progress page has details on how to access this
new functionality.
The page also includes the full list of FFmpeg supported formats.
The FFmpeg library can linked and loaded dynamically at run time,
this allows it to be distributed as a separate package and
removes any CODEC licensing issues from Audacity.
Johannes Kulick added two new wxWidgets GUI classes and used
those in Audacity to improve the display of audio tracks.
His
project abstract states:
"Audacitys main user interface is the track panel. Its GUI architecture is written from scratch by the audacity team and as the team noticed the TrackPanel.cpp is a horrendous mess which is neither easy to maintain nor to extend.
There are the wxWidgets classes wxGridSizer and wxFlexGridSizer which fit well in the requirements of the track panel. They arrange its content in a table. While in wxGridSizer all rows have the same height and all columns have the same width, in wxFlexGridSizer classes each row can have its own height and each column can have its own width. This is the way the Track panel is arranged, too, but there is one more thing which is important: the ability to drag and drop each track and drag the height of each track as well. And here is the big disadvantage of the wxWidgets classes: they lack the ability of being dragable. If there were classes which have these ability this would be a big step to get a cleaner track panel architecture for Audacity.
So the project idea is that I will implement two classes wxDragGridSizer and wxDragFlexGridSizer which have the ability to do exactly these things.
"
The
Project Progress tracks the steps that were done to achieve
the end results and the
additional report covers extra work that was done
to extend support for the wxAUI (Advanced User Interface)
toolbar and window docking library.
Michael Chinen's project involved
on-demand/level-of-detail file loading for near-instant loading and editing of uncompressed files. The
Project Progress explains:
"The QuickLoad project added near-instant loading of PCM uncompressed files without waiting for waveform calculation to complete. Playing and editing is now possible on demand at any point in the track while the waveform image is still being calculated in the background.
" The Description section further clarifies the new capability:
"Previously, it might be necessary to wait several minutes for the file to load and be useable while the waveform computation was completed.
The waveform image will draw itself automatically during computation, but users can move the point in the file from which computation takes place, thus allowing them to view and edit any point in the file instantly.
"
This project also allowed for further improvements to Audacity:
"One of the reasons the Quickload project was approved was because the OD framework will provide a method in which other tasks, such as loading non-wav formats, processing effects, and exporting, can be made multithreaded. The current implementation of the OD framework is written generally so that this is possible, which means that future implementations of OD tasks will be done writing a minimum of code. Taking advantage of polymorphism, this kind of thing should get easier and easier as more tasks are made to support OD.
"
Mark Deutsch worked on adding
sticky labels that stay with the audio through cut and paste
operations. The
Project Progress
explains:
"Label Track Enhancements removed a long-standing limitation that Audacity's labels did not stick to the audio track and move and edit with them.
"
Further:
"The biggest single addition from this project was the concept of linking tracks. Two or more linked tracks form a group. When an action is performed in one track, the other tracks in the group mirror that action. For example, if a group consists of one audio track and one label track, deleting part of the audio track will also delete that part of the label track.
This linking is done implicitly, and depends on the layout of the tracks. A group is defined as a set of contiguous audio tracks followed by a contiguous set of label tracks.
"
The sticky labels addition also improves the way Audacity
handles insertions and other operations:
"This functionality doesn't only handle deletes, though. Inserting audio, whether through pasting or using the "Generate" functions also shifts the grouped tracks correspondingly. The "Change" functions (Change Speed/Tempo/Pitch) are also supported. Slowing down a track will insert silence into linked tracks to keep all the tracks sync'd. Similarly, speeding up a track inserts silence into that track to achieve the same result.
"
Lars Luthman was unable to finish the fifth project,
Support for the LV2 plugin architecture,
but he did organize the problem space and produce some code that
should be useful for future work.
The
Project Progress report shows what was accomplished, and the
main Audacity
projects document explains how it ended:
"The project which did not pass still had plenty of good coding work and skill behind it, indeed believed to be fully working on the linux platform. It was communication, possibly to modify the goals shortly after mid term, that really let it down.
"
The 2008 GSoC projects added a number of useful new capabilities to Audacity. The wxWidgets project also benefited from the work with some enhancements that can be used by other projects. Once again, GSoC proves itself as a program that can focus in on areas of open-source applications that need improvements, and produce useful results in a short time span. GSoC is successful in bringing the guidance of experienced mentors together with the coding muscle of inspired students.
System Applications
Database Software
MySQL 5.1.28-rc has been released
A release candidate for the MySQL version 5.1.28 DBMS has been announced. "Bear in mind that this is still a "candidate" release, and as with any other pre-production release, caution should be taken when installing on production level systems or systems with critical data."
phpMyAdmin 2.11.9.1 is released (SourceForge)
Version 2.11.9.1 of phpMyAdmin has been announced. "phpMyAdmin is a tool written in PHP intended to handle the administration of MySQL over the Web. Currently it can create and drop databases, create/drop/alter tables, delete/edit/add fields, execute any SQL statement, manage keys on fields. Welcome to this security update for phpMyAdmin 2.11.9."
PostgreSQL Weekly News
The September 14, 2008 edition of the PostgreSQL Weekly News is online with the latest PostgreSQL DBMS articles and resources.
Mail Software
The Python Replybot 5.0 announced
Version 5.0 of The Python Replybot has been announced. "This is the latest incarnation of my software to send auto-replies to email messages based on various criteria, with whitelisting and grace periods. It responds in the most RFC and de-facto standards friendly way possible, conforming to email best practices."
Networking Tools
lutz: 0.6 released (SourceForge)
Version 0.6 of lutz has been announced. "lutz is a small but full-featured Portscanner for Linux. Currently it supports only SYN Scanning, but ist very stable. Scanning of multiple host in cdir/subnet/ranges combination is also supported. Today i have released Version 0.6 of lutz. I've named that release lutz-ng becouse its a complete code redesign."
Package Management
Adding a signing key to RPM
Over at "orc_orc's sharp edge" blog, there is a good description of RPM signing keys, including how to verify keys before importing them. "The RPM package manager has long had the ability (similar to GnuPG) to receive GPG public keys into its trusted store, and then to test assertions about the presence, absence, and validity of a given signing. It can retrieve a remote key with the usual RPM network retrieval capabilities, or perhaps better to avoid MitM ('Man in the Middle') compromises across a network, from the local filesystem, or a local piece of immutable media, such as a CD which has had its md5sum verified."
Web Site Development
TurboGears 1.0.7 stable released
Version 1.0.7 stable of TurboGears, a rapid web development platform, has been announced. "This version brings some more bug fixes that could not but included in the last 1.0.6 release, and also fixes a bug which was introduced in the previous release when backporting some identity stuff from the 1.1 branch. All 1.0 users who want to stay in 1.0 before trying out our new 1.1 beta should upgrade to this 1.0.7 release directly without using 1.0.6."
Desktop Applications
Animation Software
Synfig Irregular News
The September 15, 2008 edition of the Synfig Irregular News covers the latest news from the Synfig 2D vector animation studio project.
Audio Applications
jack_capture 0.9.30 and Rollendurcmesserzeitsammler 0.0.7 released
Version 0.9.30 of jack_capture has been announced, many new features have been added. "jack_capture is a program for recording soundfiles with jack. Its default operation is to capture whatever sound is going out to your speakers into a file. (But it can do a number of other operations as well...)" Also, a new version of the Audio Rollendurchmesserzeitsammler, a conservative garbage collector, is out with some code improvements.
Business Applications
Chandler Server 1.1.0 released
Version 1.1.0 of Chandler Server has been announced. "Chandler Server is a server and Ajax web UI for managing and sharing calendars, events, and tasks. It implements open data standards including CalDAV, WebDAV, Atom, and Atompub. This release contains two significant features and four bug fixes. Any user can now delete their own account and data by using the settings dialog. Interoperability with some CalDAV implementations including iCal 3 should be improved by support for the CTAG draft standard."
opentaps 1.0.2 released (SourceForge)
Version 1.0.2 of opentaps has been announced. "This version contains a number of bug fixes compared to opentaps 1.0.1 and is recommended both as an incremental upgrade for users of opentaps 1.0.1 and for new deployments. opentaps is an open source ERP and CRM system which includes a full suite of business applications, mobility integration, and business intelligence."
Desktop Environments
GNOME 2.24.0 Release Candidate (2.23.92) released
Version 2.23.92 of the GNOME desktop has been announced. "It's the final countdown. Tadada da, tadada da da, tadada da, tadadadadada! Hrm. I might be missing a da or two. You're lucky that you can't hear me sing -- you'd be quite scared ;-) So here we are, with the release candidate for 2.24.0. It's this time of the development cycle, where we all look at what we achieved and start crying because it's so beautiful!"
GARNOME 2.23.92 announced
Version 2.23.92 of GARNOME, the bleeding edge GNOME distribution, has been announced. "We are pleased to announce the release of GARNOME 2.23.92 Desktop and Developer Platform. This is the GNOME 2.24 *cough* Release Candidate *cough*. Yes, indeed. This release is for everyone! Or, well, close to that. Build it, test it. And watch out for SVN."
GNOME Software Announcements
The following new GNOME software has been announced this week:- Brasero 0.8.2 (bug fixes and performance improvements)
- GLib 2.16.6 (bug fixes)
- gnome-main-menu 0.9.11 (new features, bug fixes and translation work)
- GParted 0.3.9 (new features, bug fixes and translation work)
- GTK+ 2.12.12 (bug fixes and translation work)
- gtkmm 2.13.8 (new features and bug fixes)
- Leo 4.5.1 (bug fixes and other improvements)
- Libgda 3.99.4 (new features, bug fixes, documentation and translation work)
- Sawfish experimental 1.3.4 (new features)
KDE Commit-Digest (KDE.News)
The September 7, 2008 edition of the KDE Commit-Digest has been announced. The content summary says: "A KPhotoAlbum developer sprint leads to various developments, including a new viewer and support for image "stacks". Initial lyrics support and a new "Albums" applet in Amarok 2.0. Support for export to OpenDocument text and HTML formats for certain file types in Okular. More functionality in the Plasma "Engine Explorer", an application for data engine development..."
KDE Software Announcements
The following new KDE software has been announced this week:- BeeDiff 1.9 (new feature)
- Beesoft Commander 4.0.08.beta (new features and bug fixes)
- KMyMoney 0.9.2 (new features, bug fixes and translation work)
- KSplasherX for KDE4 alpha 1 (initial release)
- libkdcraw 0.1.5 for KDE3 (new features, bug fixes and API changes)
- NoteFinder 0.1.2 (unspecified)
- SMILE 0.8.1 (new features, bug fixes and translation work)
- Social Networks Visualiser 0.46 (new features and bug fixes)
- Social Networks Visualiser 0.47 (bug fixes and performance improvements)
- Subversion Service Menus 0.1 (initial release)
- Tellico 1.3.4 (new features and bug fixes)
- Valknut 0.3.21 / 0.4.7 (bug fixes)
Xfce 4.6 alpha released
Version 4.6 alpha of the Xfce lightweight desktop environment has been announced. "After about 18 months of development, we are pleased to announce the release of Xfce 4.6 ALPHA, codename 'Pinkie'. Xfce 4.6 is going to be the next major release of the Xfce desktop environment. The previous release was 4.4 with the last bugfix release being 4.4.2 released in December 2007."
DRI2 Protocol Spec Draft v2 released
The DRI2 Protocol Spec Draft v2 has been announced. "I've added some discussion points with ISSUE: in the spec. The new stuff here is the XChangeWindowAttributes inspired DRI2CopyRegion, that'll let us better extend it in the future. I clarified and simplified the auth stuff, dropping the group concept. Also I'm still not convinced that the swap pipe stuff can't just be an xorg.conf option, or maybe an randr property on the display (preferred swap pipe or whatever). And most of all, I'd like to keep the first version simple, considering that we have a lot of options for extending this as we go."
Xorg Software Announcements
The following new Xorg software has been announced this week:- xf86-input-synaptics 0.15.2 (new features and bug fixes)
Electronics
CQRLOG: 0.5.1 (SourceForge)
Version 0.5.1 of CQRLOG has been announced. The software is: "An advanced ham radio logger based on Firebird database. Provides radio control based on hamlib libraries (currently support of 140+ radio types and models), DX cluster connection, QRZ callbook (web version), a grayliner, ON6DP QSL manager database etc. This is bugfix release, no new features added. ADIF import/export fixed."
Financial Applications
boox: version 0.4 beta released (SourceForge)
Version 0.4 beta of boox has been announced. "boox is a very simple Java API for double-entry book-keeping. Data is stored in a SQL database - boox has been developed and tested with postgresql, but should work with any other SQL database for which a jdbc driver is available."
Games
Ember 0.5.4 released
The WorldForge virtual world project has announced the release of Ember 0.5.4. "Ember is a 3d client for the WorldForge project. It uses the Ogre 3d graphics library for presentation and CEGUI for its GUI system. This release incorporates the results from the three Google Summer of Code projects. The entity creator is greatly expanded, with scripting functionality, theres now proper support for terrain modifiers and theres a working sound system in place."
Multimedia
Elisa Media Center 0.5.10 released
Version 0.5.10 of Elisa Media Center has been announced. "A very important and long awaited improvement of this release is the rewrite from scratch of the video, audio and slideshow players user interface. The team is proud to present a brand new look with a strong focus on aesthetics and extensibility; it is fully pluggable and new controls can easily be added via plugins. A fair number of bugs were also fixed during this cycle (14 bugs)."
Music Applications
Patchage 0.4.2 announced
Version 0.4.2 of Patchage has been announced. "Patchage is a graphical modular patch bay for audio/MIDI systems based on JACK, LASH, and ALSA. This release adds: - Support for the new LASH D-BUS interface (currently LASH SVN only) - Improved LASH GUI (from Nedko Arnaudov's ladi-patchage branch) - Quick/easy connection of groups of ports in one action (select all the ports and press enter) Also released in parallel are the two libraries Patchage depends on, raul 0.5.1 and flowcanvas 0.5.1."
Renoise 2.0 Beta 1 is available
Version 2.0 Beta 1 of Renoise has been announced. "Renoise 2.0 provides unprecedented granular control over audio, now with a range of new features targeting traditional recording artists and composers. A unique approach when compared with mainstream music sequencers, Renoise's streamlined workflow delivers professional results on Windows, Macintosh, or Linux. Why spend hours cobbling beats together with a mouse when you can do it in seconds with a few keystrokes?"
Video Applications
Dirac 1.0.0 released.
The Dirac video codec has released version 1.0. Dirac is a free software, royalty-free codec developed by the BBC. "The initial implementation of Dirac at resulted in a research implementation which is referred to as the Dirac codebase. It is now called dirac-research. It is a reference implementation and also a codebase for future algorithmic developments. Dirac 1.0.0 is the release of this codebase." Click below for the full announcement.
Miscellaneous
The GNU PDF project's new blog
The first edition of the GNU PDF developer blog has been launched. "This is the first weekly report about the development of the GNU PDF project. We plan to release this kind of report so that people can be aware of the progress and on-goings of the project."
Languages and Tools
C
Building the Debian archive with GCC 4.4
Martin Michlmayr reports on his efforts to build roughly 8000 packages from the Debian archive using GCC 4.4. His intent is to find any problems in GCC 4.4 before the release. "In total, I filed 28 new bugs and ran into 7 known issues. 64% of the bugs I filed have already been fixed and many of those that are still open have already received some attention. I'd like to thank the GCC community for such an outstanding job dealing with incoming bug reports and fixing compiler regressions." Click below for the full report.
GCC adds support for Picochip
The GCC project has announced support for the Picochip platform. "Picochip is a 16-bit processor. A typical picoChip contains over 250 small cores, each with small amounts of memory. There are three processor variants (STAN, MEM and CTRL) with different instruction sets and memory configurations and they can be chosen using the -mae option. This port is intended to be a "C" only port."
Caml
Caml Weekly News
The September 9-16, 2008 edition of the Caml Weekly News is out with new articles about the Caml language.
Java
OpenSwing: 1.7.4 released (SourceForge)
Version 1.7.4 of OpenSwing has been announced, it includes new capabilities and bug fixes. "OpenSwing is a component library that provides a rich set of advanced graphics components and a framework for developing java applications based on Swing front-end. It can be applied both to rich client applications and Rich Internet Applications."
Python
Jython 2.5 Alpha3 released
Version 2.5 Alpha3 of Jython, a Java implementation of Python, has been announced. "Jython 2.5 Alpha3 fixes a bug that caused installation problems for many Windows users, so Oti Humbel and Leo Soto came to the rescue with an assist by Geoffrey French. Oti also fixed standalone mode while he was there."
Python 2.6rc1 released
The first release candidate for Python 2.6 is out. The final release is still on track for October 1st. "You might notice that unlike earlier releases, we are /not/ releasing Python 3.0rc1 at this time. It was decided that 3.0 still needs time to resolve open issues and that we would not hold up the 2.6 release for this. We feel that Python 2.6 is nearly ready for its final release." Click below for the full release announcement.
Python-URL! - weekly Python news and links
The September 16, 2008 edition of the Python-URL! is online with a new collection of Python article links.
Tcl/Tk
Tcl-URL! - weekly Tcl news and links
The September 16, 2008 edition of the Tcl-URL! is online with new Tcl/Tk articles and resources.
Version Control
GIT 1.6.0.2 released
Version 1.6.0.2 of the GIT distributed version control system has been announced. Changes include numerous bug fixes and documentation updates.
Miscellaneous
OpenOpt 0.19 announced
Version 0.19 of OpenOpt has been announced, it includes new capabilities and bug fixes. The description states: "OpenOpt v 0.19, free (license: BSD) optimization framework (written in Python language) with connections to lots of solvers (some are C- or Fortran-written) is released."
Page editor: Forrest Cook
Linux in the news
Recommended Reading
Cassidy: Linux devotee tries to spread the word (Mercury News)
The San Jose Mercury News reports on the Lindependence movement; an effort to mass convert folks from Windows to Linux. "For his part, Cafiero is leading a revolution in the redwood-ringed town of Felton. He's been inspired by others around the country and with them he's dubbed the effort 'Lindependence 2008,' a scheme hatched to turn Felton into an all-Linux enclave."
End Runs Around Vista (BusinessWeek)
BusinessWeek takes a look at what various vendors are doing in light of Vista's problems, including a report that HP is considering making its own Linux distribution. "Still, the sources say employees in HP's PC division are exploring the possibility of building a mass-market operating system. HP's software would be based on Linux, the open-source operating system that is already widely available, but it would be simpler and easier for mainstream users, the sources say. The goal may be to make HP less dependent on Windows and to strengthen HP's hand against Apple (AAPL), which has gained market share in recent years by offering easy-to-use computers with its own operating system."
Companies
Canonical to fund upstream Linux usability improvements (ars technica)
ars technica reports on Canonical's efforts to improve the Linux desktop. "Ubuntu founder Mark Shuttleworth announced Wednesday that his company, Canonical, will hire professional designers and interaction experts to improve the usability of the Linux desktop software ecosystem. They will work closely with upstream developers to bring a better experience to users of the open source operating system. The charismatic frontman of the Ubuntu phenomenon made headlines for his keynote at OSCON earlier this year when he called for the open source software community to take on Apple and Microsoft and turn Linux into a platform that delivers superior usability and attractiveness."
Lenovo halts online sales of Linux-based PCs (ComputerWorld)
ComputerWorld reports that Lenovo is discontinuing sales of pre-installed Linux systems. "Lenovo Group Ltd. is cutting back on sales of desktops and laptop systems with the Linux operating system pre-installed. The PC maker said yesterday that it will no longer take online orders for computers pre-loaded with any flavor of Linux. Ray Gorman, a spokesman for the company, said that it will continue offering such machines only through its own or partner direct sales teams. "Our commitment to Linux has not changed," said Gorman in an e-mail to Computerworld. "What's changed is that customers will no longer be able to order Lenovo ThinkPads and ThinkCentres with pre-installed Linux via the lenovo.com Web site.""
Business
A New Model: Open Source Software After It's Acquired (InformationWeek)
Here's a lengthy InformationWeek article on corporations and their management of (and acquisition of) open source projects. "Over the past 24 months, a premium has been placed on open source code, as it moved from the backwater of the enterprise to the mainstream. In the process, open source has become big business. The idea: Develop open source code quickly; make it available for free download in hopes of winning early market momentum; rake in some technical support revenues as the code develops an enterprise following; and cash in via an acquisition by a deep-pocketed vendor."
Linux at Work
KDE Congratulates CERN's Large Hadron Collider (KDE.News)
KDE.News congratulates the CERN LHC project on its first day of operation. "Today was Big Bang Day at CERN as the world's largest science experiment was turned on. Like all good technology enthusiasts the KDE developers have been keeping up with the progress of the Large Hadron Collider in Switzerland. We are pleased to see that like all world class physicists the first ever ATLAS results come from KDE. Their impressive control centre is also making excellent use of KNotes. Just as good, the world has not yet been sucked into a black hole."
Resources
Java Sound & Music Software for Linux, Part 2 (Linux Journal)
Dave Phillips continues his look at Java sound and music applications. "In this second part of my survey I list and briefly describe some of the Java sound and music applications known to work under Linux. Java applications show up in almost every category found at linux-sound.org and the Applications Database at linuxaudio.org. The scalability of the language is well-demonstrated throughout those pages where one can find everything from highly specialized mini-applications to full-size production environments. Of course I can't cover or even present the entire range of Java soundapps, but this survey should give readers a good idea of Java's potential in the sound and music software domain. Again the presentation is in no special order."
Linux Scalability in a NUMA World (Linux Magazine)
Linux Magazine looks at Non-Uniform Memory Access (NUMA) systems and Linux. It describes how to determine the NUMA topology and then how to tell Linux how to best use the processors based on the workload. "The overall performance of a NUMA system depends on the proportion of memory accesses made by all processors to local (directly connected) memory. Each access a task makes to remote memory reduces the performance of that task. It may also reduce the performance of other tasks, by causing contention for remote memory connections."
Reviews
Easystroke Makes Mouse Gestures Easy in Linux (Lifehacker)
Lifehacker has a review of Easystroke which is a program to record and manage mouse gestures. "Once it's launched, you'll see the Easystroke icon sitting in your system tray. Assuming you're using a three-button mouse (trackpad gestures can be a bit tricky), hold down your middle/scroll button and make some gestures around the screen. Easystroke's icon will change to represent what you just did, and you'll get a feel for how responsive the program is."
10 interesting open source software forks and why they happened (Pingdom)
Royal Pingdom looks at ten successful software forks. "Much of the open source software that is in popular use today was born from other projects. We thought it would be interesting to take a look at the history of some of these software forks and find out WHY they happened in the first place. We looked at the WHY because software forking is often seen as somewhat of a waste of development resources and isnt considered a good thing. Sometimes the results can be great, though, as many of the examples below clearly show."
Miscellaneous
Polk Community College and USF get grant for Linux curriculum (Orlando Business Journal)
Orlando Business Journal reports on an NSF grant for the development of Linux courses. "Polk Community College and the University of South Florida Polytechnic have received an $812,726 grant from the National Science Foundation to develop a four-year curriculum for Linux computer system administration. The grant funds will be issued to the two institutions over three years. Cliff Bennett, director of PCC's network engineering technology program, said the grant will let the schools develop a program that "will produce graduates skilled in open-source Linux system administration.""
Page editor: Forrest Cook
Announcements
Non-Commercial announcements
EFF: Court affirms 4th Amendment protects location information
Electronic Frontier Foundation reports that a US court has decided that a warrant is required before accessing cell phone location records. "San Francisco - In an unprecedented victory for cell phone privacy, a federal court has affirmed that cell phone location information stored by a mobile phone provider is protected by the Fourth Amendment and that the government must obtain a warrant based on probable cause before seizing such records."
Openmoko OpenLab Opens the Path for Open Learning
National Tsing Hua University of Taiwan has decided that Openmoko will be used as a major teaching and researching platform in its curriculum. "Starting this coming semester students at the university will have the opportunity to work at Openmoko's OpenLab on campus at Tsing Hua. The full lesson plans take students from powering on the device to writing complete mobile applications. All content developed during the course as well as the course content itself is released under a creative commons share-alike license."
Commercial announcements
Azingo To Offer Adobe Flash Lite on Linux Mobile Phones
Azingo has announced the availability of Adobe Flash Lite support on its mobile Linux platform. "Mobile Linux company Azingo continues to deliver on its promise of providing a complete Internet experience on mobile devices with its announcement today of Adobe® Flash Lite 3.1 support on Azingo Mobile. Azingo has integrated Adobe Flash Lite into its advanced mobile browser enabling the display of animated web content and videos and making Adobe Flash available on a Linux mobile platform."
Microsoft and Novell deliver Joint Virtualization Solution
Microsoft Corp. has announced a Linux/Windows virtualization system. "Microsoft Corp. and Novell Inc. are announcing the availability of a joint virtualization solution optimized for customers running mixed-source environments. The joint offering includes SUSE(R) Linux Enterprise Server from Novell(R) configured and tested as an optimized guest operating system running on Windows Server 2008 Hyper-V, and is fully supported by both companies' channel partners, including Dell Inc., which will test and validate this offering at the Microsoft and Novell joint Interoperability Lab in Cambridge, Mass."
Sun's Project Kenai
Sun Microsystems has launched Project Kenai, a hosting system for free software projects. This announcement talks about why the company felt the need to create another hosting service. "Kenai is a recognition by Sun that, as the largest open source company in the world, we need to take control of our own destiny. We need a place to nurture and grow our open source communities that we ourselves can control; we need to demonstrate credibility in building on top of more traditional LAMP/SAMP web stacks (not just Java EE); and we need to show viability of Sun technologies and hardware for next-generation web applications."
Wyse and Novell announce first enterprise-class Linux thin client
Wyse Technology and Novell have announced the availability of Wyse Enhanced SUSE(R) Linux Enterprise. "Wyse Technology, the global leader in thin computing, and Novell today announced the joint delivery of Wyse Enhanced SUSE(R) Linux Enterprise, the next-generation of Linux* operating system designed for thin computing environments and available only on Wyse desktop and mobile thin client devices. Wyse Enhanced SUSE Linux Enterprise is a powerful combination of Wyse's extensive experience in thin computing and the ease of use, flexibility and security of SUSE Linux Enterprise."
Contests and Awards
Plat'Home unveils winners of "Will Linux Work?" contest
Plat'Home has announced the winners of the "Will Linux Work?" contest. "For five weeks, Plat'Home challenged the Linux community to propose interesting and challenging scenarios to run Plat'Home OpenMicroServer. Participants were asked to push a normal server's limits and suggest ideas that would test and reveal if Linux really could work in any environment. OpenMicroServers will be awarded to the following four participants who will be given one month to test their scenarios and report their results back to Plat'Home".
Education and Certification
Beginning Computer Programming with HLA and PYTHON
A free online Python course has been announced. "Beginning Computer Programming with HLA and PYTHON will provide the beginner with a tremendous jump start in understanding. The newbie will readily appreciate the benefits of the High Level instructions in Python and HLA and the benefits of Low Level instructions in Assembly after just a little 'hands on' use of each. The reason for these free online Google Docs is to provide a fun and user friendly, but solid and quickly productive foundation for new programmers."
Meeting Minutes
Perl 6 Design Meeting Minutes (use Perl)
The minutes from the August 6, 2008 Perl 6 Design Meeting have been published. "The Perl 6 design team met by phone on 06 August 2008. Larry, Jerry, Nicholas, Jesse, and chromatic attended."
Perl 6 Design Meeting Minutes (use Perl)
The minutes from the August 20, 2008 Perl 6 Design Meeting have been published. "The Perl 6 design team met by phone on 20 August 2008. Larry, Allison, Patrick, Jerry, and Jesse attended."
Calls for Presentations
German Perl-Workshop 2009 cfp
A call for papers has gone out for the 2009 German Perl-Workshop. "From February 25th 2009 to February 27th 2009 (Wednesday til Friday) the 11th German Perl Workshop will take place in Frankfurt am Main at the "House of the Youth" ("Haus der Jugend"). The Workshop targets all serious Perl users. Our Workshop is in need of your talk. Usually talks are 5, 20 or 40 minutes long. All topics which have to do with Perl or anything concerning Perl in any way could possibly be of interest for a talk at the Workshop."
SCALE 7x Issues Call For Papers
SCALE 7x, the 7th Annual Southern California Linux Expo, has issued a call for papers. SCALE 7x will be held on February 20 - 22, 2009 at the Los Angeles Airport Westin. The deadline for submissions is November 30, 2008.Call for Papers: SCSS 2008
A call for papers has gone out for the Fourth International Conference on Systems, Computing Sciences and Software Engineering (SCSS 2008). The event takes place online on December 5-13, 2008, the submission deadline is October 15. "SCSS 2008 provides a virtual forum for presentation and discussion of the state-of the-art research on Systems, Computing Sciences and Software Engineering."
TwinCity Perl Workshop cfp (use Perl)
use Perl has announced a call for papers for the "Vienna.pm has set aside a budget of 1000 Euro to invite speakers to the Twin City Perl Workshop." The event takes place in Vienna and Bratislava on November 7 and 8, 2008. The submission deadline is September 21.
Upcoming Events
The OpenSAF Developer Days
The OpenSAF Developer Days event has been announced. "Responding to strong interest and feedback from the open source community, the OpenSAF Project today announced the final program for its upcoming open source "Developer Days 2008" conference. The event will be held in Munich, Germany, on October 15 and 16, 2008, and is free of charge. The conference is designed to gather all parties interested in high availability software and its development in an open source environment."
Texas Regional Unconference
The Python Texas Regional Unconference will be held in Austin, TX on October 4-5, 2008. "Like last year, this Unconference is intended to be a FREE event for Pythoneers from all over the Texas region to gather and share experiences and developments. Again, the topics to be presented are purely up to the participants."
Events: September 25, 2008 to November 24, 2008
The following event listing is taken from the LWN.net Calendar.
| Date(s) | Event | Location |
|---|---|---|
| September 22 September 25 |
Storage Developer Conference 2008 | Santa Clara, CA, USA |
| September 23 September 25 |
4th International Conference on IT Incident Management and IT Forensics | Manheim, Germany |
| September 24 September 25 |
OpenExpo 2008 Zürich | Winterthur, Switzerland |
| September 25 September 27 |
Firebird Conference 2008 | Bergamo, Italy |
| September 26 September 27 |
PGCon Brazil 2008 | Sao Paulo, Brazil |
| September 26 | Far East Perl Workshop 2008 | Vladivostok, Russia |
| September 26 September 28 |
ToorCon Information Security Conference | San Diego, CA, USA |
| September 27 September 28 |
WineConf 2008 | Bloomington, MN, USA |
| September 29 October 3 |
Netfilter Workshop 2008 | Paris, France |
| September 29 September 30 |
Conference on Software Language Engineering | Toulouse, France |
| September 30 October 1 |
BA-Con 2008 | Buenos Aires, Argentina |
| October 1 October 3 |
Vision 2008 Embedded Linux Developers Conference | San Francisco, USA |
| October 2 October 3 |
ekoparty Security Conference | Buenos Aires, Argentina |
| October 3 October 4 |
Open Source Days 2008 | Copenhagen, Denmark |
| October 4 | PyArkansas 2008 | Central Arkansas, USA |
| October 4 October 5 |
Texas Regional Python Unconference 2008 | Austin, TX, USA |
| October 7 October 10 |
OWASP NYC AppSec 2008 Conference | New York, NY, USA |
| October 7 | Openmind 2008 | Tampere, Finland |
| October 7 October 10 |
Linux-Kongress 2008 | Hamburg, Germany |
| October 7 | Red Hat Government Users and Developers Conference | Washington, DC, United States |
| October 10 October 12 |
Ohio LinuxFest 2008 | Columbus, Ohio, USA |
| October 10 October 12 |
PostgreSQL Conference West 08 | Portland, OR, USA |
| October 10 October 12 |
Skolelinux Developer Gathering | Oslo, Norway |
| October 11 October 12 |
Pittsburgh Perl Workshop | Pittsburgh, PA, USA |
| October 11 October 12 |
MerbCamp | San Diego, CA, USA |
| October 13 October 14 |
Linux Foundation End User Collaboration Summit | New York, USA |
| October 13 | Skolelinux User Conference | Oslo, Norway |
| October 15 October 16 |
OpenSAF Developer Days | Munich, Germany |
| October 17 October 18 |
European PGDay 2008 | Prato, Italy |
| October 18 October 19 |
Maker Faire Austin | Austin, TX, USA |
| October 19 October 24 |
Colorado Software Summit 2008 | Keystone, CO, USA |
| October 20 October 24 |
15th Annual Tcl/Tk Conference | Manassas, VA, USA |
| October 21 October 23 |
Web 2.0 Expo Europe | Berlin, Germany |
| October 21 October 24 |
Systems | Munich, Germany |
| October 22 October 24 |
Hack.lu 2008 | Parc Hotel Alvisse, Luxembourg |
| October 22 October 24 |
Encuentro Linux | Concepción, Chile |
| October 24 October 26 |
Free Society Conference and Nordic Summit | Gothenburg, Sweden |
| October 25 October 26 |
T-DOSE 2008 | Eindhoven, the Netherlands |
| October 25 | Ontario Linux Fest 2008 | Toronto, Canada |
| October 26 October 31 |
IBM Information On Demand 2008 | Mandalay Bay - Las Vegas, Nevada, USA |
| October 27 October 30 |
Embedded Systems Conference - Boston | Boston, USA |
| October 29 November 1 |
10th Real-Time Linux Workshop | Colotlán, Jalisco, Mexico |
| November 3 November 7 |
ApacheCon US 2008 | New Orleans, LA, USA |
| November 5 November 7 |
OpenOffice.org Conference 2008 | Beijing, China |
| November 6 | NLUUG autumn conference: Mobile Applications | Ede, Netherlands |
| November 6 November 7 |
Embedded Linux Conference Europe 2008 | Ede, Netherlands |
| November 7 November 8 |
TwinCity Perl Workshop 2008 | Vienna, Austria |
| November 7 November 9 |
UKUUG linux conference | Manchester, UK |
| November 8 November 9 |
Hackers to Hackers Conference 05' | Sao Paulo, Brazil |
| November 8 November 9 |
FOSS.my | Kuala Lumpur, Malaysia |
| November 10 November 14 |
Python Bootcamp with Dave Beazley | Atlanta, GA, USA |
| November 11 November 14 |
DeepSec IDSC 2008 | Vienna, Austria |
| November 12 November 14 |
php|works 2008 | Atlanta, GA, USA |
| November 12 November 13 |
PacSec Applied Security Conference | Tokyo, Japan |
| November 13 November 14 |
International Hacking and Security Conference | Seoul, Korea |
| November 14 November 16 |
OpenSQL Camp 2008 | Charlottesville, VA, USA |
| November 16 November 20 |
Middle East IT Security Conference | Dubai, UAE |
| November 19 November 20 |
Linux Foundation Japan Symposium | Tokyo, Japan |
| November 20 November 21 |
FreedomHEC Taipei 2008 | Taipei, Taiwan |
| November 22 | The phpnw08 conference | Manchester, UK |
| November 22 | PGDay Rio de la Plata | Buenos Aires, Argentina |
| November 22 | Mandriva 2009 Installfest | Everywhere, World |
If your event does not appear here, please tell us about it.
Event Reports
RailsConf Europe 2008 Spreads the Power of Rails
O'Reilly has published a report on the recently held RailsConf Europe 2008. "The third annual RailsConf Europe September 2-4 in Berlin gave the dynamic European Rails community exactly what it asked for: Technical tools to match its advancing skills. From the ambitious novice to the experienced programmer, Europe's Rails users said they wanted in-depth sessions and real-world solutions that would give them an edge in innovation and productivity. Co-presenters Ruby Central and O'Reilly Media gave them what they wanted."
Web sites
O'Reilly launches StartWithXML
O'Reilly has announced the launch of the StartWithXML project. "The enormous success of the Kindle and the iPhone has undeniably fueled the XML revolution. Smart publishers are scrambling to make more of what they produce--books, magazines, newspapers, and more--readily available for reading on these popular devices. Indeed, without XML, delivering content across multiple channels, devices, and digital formats profitably would be impossible. To help publishers adjust to today's publishing environment, make better use of innovative, up-to-the-minute resources, and profit from the many new markets for their content, O'Reilly Media has teamed up with Idea Logical Company to launch "StartWithXML: Why and How.""
Audio and Video programs
Two Django Workshop videos announced
Linux Magazine has announced the availability of two new Django web platform workshop videos. Topics include the Django Video Workshop with Douglas Napoleone and Programming with the Python Django Web Framework.
Page editor: Forrest Cook