

LWN.net Weekly Edition for July 10, 2008
SELinux and Fedora
Red Hat has undoubtedly done more to make SELinux usable than any other organization, but has it actually reached the point where it can be enabled by default for all desktops? The Fedora project clearly thinks so. Not only is SELinux enabled, but the installer no longer has an option to disable it or to put it into "permissive" mode. Most of the posts in a thread on the fedora-devel mailing list see that as the right choice, but some are not so sure.
Jon Masters started things off by making a request to restore the installation option, giving several reasons summing up with:
His reasons were unconvincing to many as he was not considered to be a "normal" desktop user; the things he was doing were much more technical than the users that are being targeted by the SELinux policies distributed with Fedora 9. The problems he reported were resolved quickly, but the fact remains that there are paths through Fedora—even just using desktop applications—that will result in SELinux-caused failures. The Red Hat SELinux team is very responsive, but users will get frustrated quickly if things they are trying to do fail in mysterious (to them) ways.
Alan Cox argues against providing an installation choice because he doesn't think users have enough context to make a sensible choice. He likens it to a car with multiple choices for safety features:
"Would you like the seatbelts to work ?"
"Shall I enable the airbag ?"
When push comes to shove, Masters and a few others see the default of SELinux installed in "enforcing" mode as being too restrictive. It is likely to cause users to become annoyed with Fedora as a whole because one or more paths through the applications have not yet been tested. That, unfortunately, is the crux of the issue: SELinux policies are being developed in a reactive manner based on testing applications and adding exceptions for actions they perform.
As a security tool, SELinux is a good choice, because it essentially denies everything by default. Policies are added that will allow certain actions for users and applications. Its complexity is legendary, however, which is why Red Hat (and others) have made a substantial effort to make it work semi-invisibly. They started by generating policies for network-facing services and have now moved into securing desktop applications, particularly programs like web browsers which are increasingly the target of attacks.
SELinux has three modes, disabled, which turns off SELinux, permissive, which just logs attempts to do things that violate the policies, and enforcing, which disallows any access that is denied by the policies. When getting applications to work with SELinux, permissive mode is typically used. The log messages are analyzed to determine what changes should be made to the policies or to the application so that they work together. If there are features that were not tested in the application that require additional privileges, the first user that tries that feature in enforcing mode will run into trouble.
When that happens, SELinux can be put into permissive mode with a simple GUI or configuration file change, followed by a reboot. One of the problems is that users may very well not know that SELinux is the source of their problem. There are tools, like SETroubleShoot, that can help alert users, but it is still a frustrating, hard to comprehend problem at times. Once the user has "fixed" the problem by disabling SELinux, they are unlikely to turn it back on.
It is a difficult choice, but Fedora is firmly on the side of forcing non-technical users into using SELinux, at least until it breaks. More technical users will know about SELinux and, perhaps, be able to make more informed choices. One of Red Hat's SELinux developers, James Morris, neatly sums up the reasons it is important to continue pushing SELinux:
[...] Punting the decision to the end user during installation is possibly the worst option. It's our responsibility as the developers of the OS to both get security right and make it usable. It's difficult, indeed, but not impossible.
There are efforts underway to add easier ways for users to report SELinux log messages, perhaps even in an automated way, so that policy or application problems get identified and fixed more quickly. While it may not be easy for long-time Linux users to adjust to an SELinux-enabled system, it is getting to the point where average users, who never use the command line, rarely run into problems. And those are just the kind of users who need the level of security that SELinux can provide.
Questions and answers with Stormy Peters
Those who have followed the GNOME project over the last few years have seen the wishlist item for a "business manager" or "executive director" for the GNOME Foundation; the subject was especially likely to come up during Foundation board elections. This position has remained unfilled for some time, seemingly a result of uncertain funding and the difficulty of finding the right person. These problems would appear to be in the past now; on July 7, the GNOME Foundation announced that this position would be filled by Stormy Peters, formerly of OpenLogic.Stormy now has the challenge of helping an energetic and independent-minded development community build on its success and achieve its ambitious goals for the future. We asked her a few questions about how she thought that might go; here's what we got back.
LWN: This is a new position, in that the GNOME Foundation has never had an executive director before. So people may be wondering what you'll actually be doing. How do you expect to be spending your time in this position?
A year from now, what do you hope your biggest accomplishments will be?
Next year, it seems reasonably likely that there will be a combined GNOME/KDE developers conference in Europe. What are your thoughts on the current state of cooperation with KDE, and how do you think it could be improved?
One high-profile GNOME goal was 10x10 - 10% of the desktop market by 2010. In mid-2008, it seems fairly clear that this goal will not be achieved. Do you think that the desktop remains a suitable target for free software, or should GNOME deemphasize the traditional desktop in favor of other goals?
Though the GNOME Foundation is not intended to control the technical direction of the project, it clearly cannot be without influence there. Are there technical directions you would like to see the development community take, directions which would help to convince manufacturers to incorporate GNOME technologies and contribute to GNOME development?
In the past you have spoken about how introducing money into free software development can have a demotivating effect on developers. Do you fear that sort of problem as GNOME becomes more commercially successful? How would you hope to avoid that kind of difficulty?
Thanks to Stormy for being kind enough to answer our questions in the middle of what must have been a highly busy time at GUADEC in Istanbul.
Notes on the Viacom ruling
Google's purchase of YouTube always seemed questionable to some observers: it looked as if Google were buying itself a whole new source of copyright lawsuits. One of the benefits of that purchase came through on July 2, when a U.S. District Court ordered Google to hand over its complete set of YouTube traffic logs, containing information about every video viewed on the service. See Groklaw for the full text of the order. If this order stands (and it appears that Google will not appeal it), millions of users worldwide will have their viewing data handed over to a litigious entertainment industry company. There's a couple of important implications to draw from this turn of events, so LWN will venture a little far afield and take a look.The data involved includes, for each video viewed, the time, which video was involved, which YouTube user account was used, and the IP address the request came from. Viacom claimed that the privacy of YouTube users is not threatened by this release of data, and the court agreed. But account names can be correlated across sites, and IP addresses (especially time-correlated IP addresses) can easily identify exactly who was watching a particular video. Viacom promises it would never use this data to launch enforcement actions against individuals; the fact that the company feels the need to make that promise suggests that Viacom feels it could use this data to that end.
One other interesting aspect of the ruling which has been commented upon less is this: Google has also been ordered to hand over every video which has been removed from the site. Once again, that is a great deal of data. It also drives home the point that, on a site like YouTube, nothing is really removed: all of those "removed" videos are still there, waiting for some company with enough lawyers to go after it.
All of this data is to be handed over regardless of what jurisdiction the users thought they were in. Nobody's privacy or data retention laws apply here. This is a worldwide compromise of personal data.
So lesson number one is obvious: attending to one's personal security requires being very careful about the data tracks that one leaves on other peoples' servers. Regardless of any site's privacy policy or any country's data sharing laws, that data is there for the grabbing. The course of events which led to the compromise of vast amounts of video-viewing data can also lead to the disclosure of electronic mail, accounting data, online chat sessions, purchase histories, software downloads, or which edgy Second Life neighborhood one likes to hang out in. Indeed, records of video viewing activity are more strongly protected in the U.S. than many other types of data; other types of information may well prove easier to get. What we leave on remote machines seems to stay there indefinitely, and it's an open book for those with sufficient legal power on their side.
[PULL QUOTE: If you gather together that much information on the behavior of many millions of people, somebody, somewhere, is going to try to get their hands on it. END QUOTE] The second lesson is for anybody running a publicly-available server, as many LWN readers do. The video activity database being grabbed by Viacom is said to be about 12 terabytes deep - before getting into the "removed" videos. It should not be surprising that a data stash of that size would attract this kind of action. If you gather together that much information on the behavior of many millions of people, somebody, somewhere, is going to try to get their hands on it. How could it possibly be any other way?
Not enough people are asking this question: why does Google/YouTube hold that much data about its users? Why does it retain the ability to replay their actions years after the fact? And why do "removed" videos not go away? If that data did not exist in the first place, there would be no question of disclosing it to an attacking corporation. A company which keeps that amount of data around is prioritizing whatever commercial value it sees in that data over the privacy and security of its users. And, by inviting raids from corporations (which we hear about) and governments (which we might not hear about), such companies are not helping their own security either.
So there are strong arguments for simply not retaining all that data in the first place. Naturally, some governments are doing their best to force that kind of retention, but that's a different battle. In the absence of legal constraints, a standard policy mandating short data retention periods makes a lot of sense. It behooves all of us to think about what kind of data we leave lying around - either through our activities or by facilitating the activities of others - and to keep it to a minimum. The most secure data is data which does not exist.
Security
Secrecy and the DNS flaw
By now, most folks will have seen reports of the design flaw discovered in DNS as it has seen fairly widespread coverage, even in the non-technical press. It is rare to see such a coordinated disclosure and security update amongst that many of the big players in the computer industry. While fixes abound, the actual problem has yet to be disclosed, which has both positives and negatives.
Responsible disclosure policies dictate that vulnerabilities be kept secret until all affected vendors can create an update. Because this flaw is in the design of DNS, most implementations were affected. This still doesn't quite explain the roughly six months between the discovery of the problem and the release of the fix. Evidently it took a meeting of the minds at the Microsoft campus in March to decide upon the right course of action. Once the fixes were done, presumably they were released on the next "patch Tuesday"—Microsoft's monthly security update day.
Normally, once fixes are available, information about the vulnerability is released. But, for a number of reasons, that has not happened in this case. One of the main reasons is that DNS is an essential internet service and it will take time for affected users to patch their systems. In addition, there have been no reports of this flaw being exploited "in the wild", reducing the pressure to divulge it.
Security researcher Dan Kaminsky discovered the flaw and he has yet another, "blatantly selfish" reason for keeping it quiet as he would like to be able to announce it at Black Hat in Las Vegas in early August:
None of these seem like horrible reasons to keep the vulnerability quiet for a time (roughly 30 days), but they do leave some DNS implementations and worried administrators without the information they need to evaluate the situation. Administrators do not know what traffic patterns or other symptoms to look for to determine if exploits are being attempted. Smaller, less prominent DNS implementations were not included in the collaboration, thus they don't have enough information to decide whether they are vulnerable or not.
A perfect example is Dnsmasq, a lightweight DNS server for smaller networks. Dnsmasq is often used in embedded Linux distributions targeted for home wireless routers. Simon Kelley, Dnsmasq developer, was asked about the vulnerability; his response speaks volumes:
Kelley has since released a patched version, but it is still unknown whether it is needed or, really, if it even fixes the problem. It is difficult to know for sure that a security hole has been closed if information about the hole is not available. This points to the problems that can come from withholding vulnerability information.
Based on the patches and some information from Kaminsky and others, it is clear that this is a cache poisoning vulnerability. Since source port randomization is the change that was applied to alleviate, but not eliminate, the flaw, we can surmise that Kaminsky found a way to reduce the number of spoofed replies that need to be sent to something tractable. According Internet Systems Consortium, developers of the BIND DNS server, the only true solution is DNSSEC, which implies that the current fixes only make cache poisoning less likely, not impossible.
Source port randomization is a technique that has been advocated by Daniel J. Bernstein (i.e. djb) for many years. He implemented it in his djbdns name server long ago. Essentially, it chooses a random source UDP port for each query that the name server makes, which has the effect of increasing the randomness that an attacker needs to be able to predict before being able to poison the cache.
While the market share of Dnsmasq may be miniscule, there are certainly other DNS implementations that are also concerned. In addition, we are relying on those who are "in the know" to be on the lookout for suspicious traffic that might indicate the vulnerability being exploited. Kaminsky is certainly under no obligation to reveal anything, but one wonders if the safest course would have been for him to provide details now, even at the expense of his "thunder".
Brief items
Dan Kaminsky Discovers Fundamental Issue In DNS: Massive Multivendor Patch Released (Securosis.com)
Dan Kaminsky has found a flaw in the design of DNS that can allow cache poisoning as an article at Securosis.com details. This has lead to a CERT advisory as well as a coordinated release of patched DNS servers from all affected vendors. Evidently source port randomization is helpful in alleviating the problem. "The issue is extremely serious, and all name servers should be patched as soon as possible. Updates are also being released for a variety of other platforms since this is a problem with the DNS protocol itself, not a specific implementation. The good news is this is a really strange situation where the fix does not immediate reveal the vulnerability and reverse engineering isn't directly possible." That last claim seems rather strong, time will tell, but it makes sense to be prepared to upgrade affected servers as soon as distributions make them available.
Mozilla Foundation developing a model for a security metric (heise online)
An article at heise online describes Mozilla's new security metrics project, which is an attempt to measure the relative security of Firefox. "One of the main factors cited is how long Firefox users are exposed to a threat while a hole remains unpatched. The developers say they want to use the security metric derived from the results to identify any problematic stage in the development and patch process."
New vulnerabilities
bind9: DNS cache poisoning
| Package(s): | bind9 | CVE #(s): | CVE-2008-1447 | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Created: | July 8, 2008 | Updated: | March 16, 2010 | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Description: | From the Debian advisory: Dan Kaminsky discovered that properties inherent to the DNS protocol lead to practical DNS cache poisoning attacks. Among other things, successful attacks can lead to misdirected web traffic and email rerouting. | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
glib2: buffer overflow
| Package(s): | glib2 | CVE #(s): | CVE-2008-2371 | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Created: | July 3, 2008 | Updated: | April 9, 2010 | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Description: | The glib2 library has a heap-based overflow that is caused by incorrect option handling in pcre. | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
jetty: multiple vulnerabilities
| Package(s): | jetty | CVE #(s): | CVE-2007-5615 CVE-2007-5614 CVE-2007-5613 | ||||||||||||
| Created: | July 7, 2008 | Updated: | February 17, 2009 | ||||||||||||
| Description: | From the Red Hat bugzilla: For CVE-2007-5613: "Cross-site scripting (XSS) vulnerability in Dump Servlet in Mortbay Jetty before 6.1.6rc1 allows remote attackers to inject arbitrary web script or HTML via unspecified parameters and cookies." For CVE-2007-5614: "Mortbay Jetty before 6.1.6rc1 does not properly handle "certain quote sequences" in HTML cookie parameters, which allows remote attackers to hijack browser sessions via unspecified vectors." For CVE-2007-5615: "CRLF injection vulnerability in Mortbay Jetty before 6.1.6rc0 allows remote attackers to inject arbitrary HTTP headers and conduct HTTP response splitting attacks via unspecified vectors." | ||||||||||||||
| Alerts: |
| ||||||||||||||
linuxdcpp: denial of service
| Package(s): | linuxdcpp | CVE #(s): | CVE-2008-2953 CVE-2008-2954 | ||||||||||||||||
| Created: | July 3, 2008 | Updated: | December 9, 2008 | ||||||||||||||||
| Description: | From the Red Hat
bug report:
CVE-2008-2953: Linux DC++ (linuxdcpp) before 0.707 allows remote attackers to cause a denial of service (crash) via "partial file list requests" that trigger a NULL pointer dereference. CVE-2008-2954: client/NmdcHub.cpp in Linux DC++ (linuxdcpp) before 0.707 allows remote attackers to cause a denial of service (crash) via an empty private message, which triggers an out-of-bounds read. | ||||||||||||||||||
| Alerts: |
| ||||||||||||||||||
mercurial: unauthorized access
| Package(s): | mercurial | CVE #(s): | CVE-2008-2942 | ||||||||||||
| Created: | July 3, 2008 | Updated: | July 18, 2008 | ||||||||||||
| Description: | From the National Vulnerability Database: Directory traversal vulnerability in patch.py in Mercurial 1.0.1 allows user-assisted attackers to modify arbitrary files via ".." (dot dot) sequences in a patch file. | ||||||||||||||
| Alerts: |
| ||||||||||||||
openldap: denial of service
| Package(s): | openldap | CVE #(s): | CVE-2008-2952 | ||||||||||||||||||||||||||||||||||||||||
| Created: | July 3, 2008 | Updated: | October 17, 2008 | ||||||||||||||||||||||||||||||||||||||||
| Description: | From the National Vulnerability Database: liblber/io.c in OpenLDAP 2.3.41, 2.3.42, and possibly other versions allows remote attackers to cause a denial of service (program termination) via crafted ASN.1 BER datagrams, which triggers an assertion error. | ||||||||||||||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||||||||||||||
php: multiple vulnerabilities
| Package(s): | php | CVE #(s): | CVE-2007-1649 CVE-2008-2107 CVE-2008-2108 CVE-2008-2829 | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Created: | July 4, 2008 | Updated: | June 1, 2009 | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Description: | From the CVE entries:
PHP 5.2.1 allows context-dependent attackers to read portions of heap memory by executing certain scripts with a serialized data input string beginning with S:, which does not properly track the number of input bytes being processed. (CVE-2007-1649) The GENERATE_SEED macro in PHP 4.x before 4.4.8 and 5.x before 5.2.5, when running on 32-bit systems, performs a multiplication using values that can produce a zero seed in rare circumstances, which allows context-dependent attackers to predict subsequent values of the rand and mt_rand functions and possibly bypass protection mechanisms that rely on an unknown initial seed. (CVE-2008-2107) The GENERATE_SEED macro in PHP 4.x before 4.4.8 and 5.x before 5.2.5, when running on 64-bit systems, performs a multiplication that generates a portion of zero bits during conversion due to insufficient precision, which produces 24 bits of entropy and simplifies brute force attacks against protection mechanisms that use the rand and mt_rand functions. (CVE-2008-2108) php_imap.c in PHP 5.2.5, 5.2.6, 4.x, and other versions, uses obsolete API calls that allow context-dependent attackers to cause a denial of service (crash) via a long IMAP request, which triggers an "rfc822.c legacy routine buffer overflow" error message. (CVE-2008-2829) | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
phpMyAdmin: cross-site scripting
| Package(s): | phpMyAdmin | CVE #(s): | CVE-2008-2960 | ||||||||
| Created: | July 7, 2008 | Updated: | February 2, 2009 | ||||||||
| Description: | From the NVD Entry: Cross-site scripting (XSS) vulnerability in phpMyAdmin before 2.11.7, when register_globals is enabled and .htaccess support is disabled, allows remote attackers to inject arbitrary web script or HTML via unspecified vectors involving scripts in libraries/. | ||||||||||
| Alerts: |
| ||||||||||
pidgin: buffer overflow
| Package(s): | Pidgin | CVE #(s): | CVE-2008-2927 | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Created: | July 9, 2008 | Updated: | December 7, 2009 | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Description: | The MSN protocol handler in pidgin contains an integer overflow vulnerability. | ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||||
poppler: memory management bug
| Package(s): | poppler | CVE #(s): | CVE-2008-2950 | ||||||||||||||||||||||||||||||||
| Created: | July 9, 2008 | Updated: | September 12, 2008 | ||||||||||||||||||||||||||||||||
| Description: | Poppler (prior to version 0.6.3-r1) contains "a memory management issue" which can be exploited (via a specially crafted PDF file) to run arbitrary code. | ||||||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||||||
ruby: directory traversal vulnerability
| Package(s): | ruby | CVE #(s): | CVE-2008-1891 | ||||||||||||||||||||
| Created: | July 3, 2008 | Updated: | October 10, 2008 | ||||||||||||||||||||
| Description: | From the National Vulnerability Database: Directory traversal vulnerability in WEBrick in Ruby 1.9.0 and earlier, when using NTFS or FAT filesystems, allows remote attackers to read arbitrary CGI files via a trailing (1) + (plus), (2) %2b (encoded plus), (3) . (dot), (4) %2e (encoded dot), or (5) %20 (encoded space) character in the URI, possibly related to the WEBrick::HTTPServlet::FileHandler and WEBrick::HTTPServer.new functionality and the :DocumentRoot option. | ||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||
ruby: integer overflow
| Package(s): | ruby | CVE #(s): | CVE-2008-2376 | ||||||||||||||||||||||||||||||||||||||||||||||||||||
| Created: | July 3, 2008 | Updated: | December 17, 2008 | ||||||||||||||||||||||||||||||||||||||||||||||||||||
| Description: | Ruby has an integer overflow vulnerability in in the rb_ary_fill() function. | ||||||||||||||||||||||||||||||||||||||||||||||||||||||
| Alerts: |
| ||||||||||||||||||||||||||||||||||||||||||||||||||||||
sipp: buffer overflows
| Package(s): | sipp | CVE #(s): | CVE-2008-2085 | ||||||||
| Created: | July 9, 2008 | Updated: | July 9, 2008 | ||||||||
| Description: | The sipp tool suffers from multiple buffer overflows which enable denial of service attacks and possible remote code execution vulnerabilities. | ||||||||||
| Alerts: |
| ||||||||||
squid: denial of service
| Package(s): | squid | CVE #(s): | CVE-2004-0918 | ||||||||
| Created: | July 3, 2008 | Updated: | July 9, 2008 | ||||||||
| Description: | From the National Vulnerability Database: The asn_parse_header function (asn1.c) in the SNMP module for Squid Web Proxy Cache before 2.4.STABLE7 allows remote attackers to cause a denial of service (server restart) via certain SNMP packets with negative length fields that causes a memory allocation error. | ||||||||||
| Alerts: |
| ||||||||||
vsftpd: denial of service
| Package(s): | vsftpd | CVE #(s): | CVE-2008-2375 | ||||||||||||||||
| Created: | July 9, 2008 | Updated: | July 30, 2008 | ||||||||||||||||
| Description: | Another denial of service vulnerability based on a memory leak has been found in vsftpd; this one is exploitable by way of invalid authentication attempts. | ||||||||||||||||||
| Alerts: |
| ||||||||||||||||||
webkit: memory corruption
| Package(s): | WebKit | CVE #(s): | CVE-2008-2307 | ||||||||
| Created: | July 9, 2008 | Updated: | November 24, 2008 | ||||||||
| Description: | WebKit suffers from a memory corruption issue in its JavaScript array handling code, leading to denial of service problems and the potential for remote code execution. | ||||||||||
| Alerts: |
| ||||||||||
Page editor: Jake Edge
Kernel development
Brief items
Kernel release status
The current 2.6 development kernel is 2.6.26-rc9, released on July 5. "Enough changes that we needed another -rc, and the regression list isn't emptying fast enough either (probably because a number of people, including reporters, are vacationing)." Along with the fixes there's a new driver for cameras which implement the standard USB video class spec. The long-format changelog has the details.
A few dozen changesets have been merged since 2.6.26-rc9, as of this writing. They are mostly fixes, but there is also a printk() extension which allows for higher-level format string specifiers; see below for details.
The current -mm kernel is 2.6.26-rc8-mm1. Recent changes to -mm include the MMU notifiers patch, a new alloc_pages_exact() function for more efficient large allocations, a lot of checkpatch.pl tweaks, and a patch series ending with "revert-revert-revert-revert-linux-next-revert-bootmem-add-return-value-to-reserve_bootmem_node.patch" that one probably doesn't want to know about.
The current stable 2.6 release is 2.6.25.10, released on July 2.
"It contains a number of assorted bugfixes all over the tree. And
once again, any users of the 2.6.25 kernel series are STRONGLY encouraged
to upgrade to this release.
"
Kernel development news
Quotes of the week
Quotes of the week part 2: the firmware flamewar
On a technical basis alone, we would never disconnect a crucial component such as firmware, from the driver. The only thing charging these transformations, from day one, is legal concerns.
When it comes to _modules_, doing that would introduce a certain amount of complexity which just doesn't seem necessary -- if you can load modules, then you have userspace, and you can use hotplug for firmware too. Especially given that so many modern drivers already _require_ you to do that, so the users understand it, and the tools like mkinitrd already cope with it -- checking MODULE_FIRMWARE() for the modules they include and including the appropriate files automatically. [...]
You need to stay sober for long enough to say 'Y' when it asks you if you want to build the required firmware into the kernel. And we even made that the _default_ now, for the benefit of those who can't stay sober that long. (Perhaps we'll make 'allyesconfig' the default next?)
The current development kernel is...linux-next?
One of the development process advantages brought by git (and by BitKeeper before it) is the ability to see the up-to-the-second, bleeding-edge status of Linus's tree. So any developer who wants to know where the front edge of development lies can grab that tree and make patches fit into it. But the value of the mainline repository for development would appear to be less than it once was. The mainline is no longer where the action is.Consider, for example, this response from Andrew Morton after finding that a patch posted to linux-kernel would not compile for him:
He followed up with this statement:
So the message would appear to be clear: development work should be done against the linux-next tree rather than against the mainline kernel. There are some clear advantages to having work done in this way. Patches developed against linux-next should merge cleanly during the next merge window. Developers will be testing each other's trees as they work, causing bugs to turn up earlier in the process. And, of course, Andrew won't have to complain about patches which fail to build for him - at least, not as often.
Linux-next is a somewhat strange base on which to try to develop, though. It is built anew every day from over 100 subsystem trees, each of which can, itself, change from one day to the next. So linux-next is a moving target, just like the mainline is. But, unlike the mainline, linux-next has no consistent or coherent history. Every day's linux-next tree is a completely new creation with a unique - and transient - history.
Consider a developer who bases some work on a mainline release - 2.6.26-rc9, say. That developer's work will be derived from a specific commit in the mainline tree, known as b7279469d66b55119784b8b9529c99c1955fe747 in this case. The history from 2.6.26-rc9 is well defined, and that series of patches can be merged into any other repository which also contains 2.6.26-rc9; the identity of that commit is consistent and immutable across all repositories. With such a development tree, it is (relatively) easy to track the mainline as it advances, and to merge one's work when the time comes. A git tree based on the mainline sits on a solid foundation.
It is not possible to base a tree on linux-next in the same way. Development can begin at a specific commit, but tomorrow's linux-next tree may not contain that commit at all. The various component trees will have advanced independently of the previous day's linux-next tree, which can, in itself, complicate things. But the process of making all those trees come together can involve tasks like moving patches from one tree to another, or fixing intermediate patches which break things. That makes the end result better, but at the cost of rebasing those trees. Rebasing completely rewrites the development history, causing the old history to disappear from the tree. So a patch series based on the previous history loses its foundation.
And, since linux-next is built from its components every day, a patch developed on top of linux-next may, when integrated into that tree, be merged somewhere in the middle of the sequence; in other words, the patch will be merged into a tree which differs considerably from the tree on which it was developed. As Stephen Rothwell, the maintainer of the linux-next tree, put it:
Another interesting aspect of linux-next development involves API changes. The longstanding rule in kernel development is that internal kernel interfaces can be changed if there is a good reason to do so, but that the person making the change is obligated to fix all in-tree code broken by that change. If an API change is introduced into linux-next, though, the developer is simply not able to fix any code which enters linux-next by way of the other subsystem trees. If the developer does get patches into those trees for the API change, they can no longer be built on top of kernels which lack that change - the mainline, for example. API changes have, in other words, become harder to do - a situation which some may see as a good thing.
What all this means is that API changes must be handled through techniques like the creation of backward-compatibility layers; those layers can then be removed a development cycle or two later once the transition is complete. Or changes can be split up and added to individual subsystem trees; that, however, can lead to interesting ordering dependencies between the trees. In some cases, we are seeing 2.6.27 changes being merged into 2.6.26 in stub form as a way of making all of the pieces fit together.
Then, there is the simple matter that developers like to have a stable base upon which to create their code. The linux-next tree, since it contains large amounts of relatively new code, will also contain its share of new bugs. That makes developers, who are often having enough trouble just tracking down their own bugs, somewhat grumpy. Development against the mainline tends to have a lower probability of forcing developers to look for bugs which are not of their own making.
Many of these complaints have an easy answer: the pain which comes from making all the pieces fit together in linux-next must be faced at some point anyway. The real difference is that linux-next allows those problems to be dealt with at leisure, while the older "merge everything in the mainline" model compressed much of that work into the merge window. How beneficial that really is will be seen for the first time in the 2.6.27 merge window; if linux-next is serving its intended function, 2.6.27 should come together with rather less hassle than its immediate predecessors did.
But, regardless of the value provided by linux-next for integration and testing purposes, the fact remains that it is a difficult platform upon which to develop patches. That process is somewhat like building a house on a sand bar; overnight the tide comes in and completely reshapes the land underneath you. That is why most (possibly all) of the subsystem trees used to assemble linux-next are, themselves, based on the mainline.
The solution to that problem will have to evolve over time. The linux-next tree is a new institution which is still finding its proper place in the development process. Easier ways to develop patches against the linux-next tree will certainly be worked out; it may well turn out that quilt-like tools work better for this task than git. But, for now, linux-next is an excellent integration and testing resource, but it has not quite yet managed to become the true Linux kernel development tree.
Multiqueue networking
One of the fundamental data structures in the networking subsystem is the transmit queue associated with each device. The core networking code will call a driver's hard_start_xmit() function to let the driver know that a packet is ready for transmission; it is then the driver's job to feed that packet into the hardware's transmit queue. The result is a data structure which looks vaguely like this:

"Vaguely" because the list of sk_buff structures (SKBs - the internal representation of packets) does not exist in this form within the kernel; instead, the driver maintains the queue in a way that the hardware can process it.
This is a scheme which has worked well for years, but it has run into a fundamental limitation: it does not map well to devices which have multiple transmit queues. Such devices are becoming increasingly common, especially in the wireless networking area. Devices which implement the Wireless Multimedia Extensions, for example, can have four different classes of service: video, voice, best-effort, and background. Video and voice traffic may receive higher priority within the device - it is transmitted first - and the device can also take more of the available air time for such packets. On the other hand, the queues for this kind of traffic may be relatively short; if a video packet doesn't get sent on its way quickly, the receiving end will lose interest and move on. So it might be better to just drop video packets which have been delayed for too long.
On the other hand, the "background" level only gets transmitted if there is nothing else to do; it is well-suited to low-priority traffic like bittorrent or email from the boss. It would make sense to have a relatively long queue for background packets, though, to be able to take full advantage of a lull in higher-priority traffic.
Within these devices, each class of service has its own transmit queue. This separation of traffic makes it easy for the hardware to choose which packet to transmit next. It also allows independent limits on the size of each queue; there is no point in filling the device's queue space with background traffic which is not going to be transmitted in any case. But the networking subsystem does not have any built-in support for multiqueue devices. This hardware has been driven using a number of creative techniques which have gotten the job done, but not in an optimal way. That may be about to change, though, with the advent of David Miller's multiqueue transmit patch series.
The current code treats a network device as the fundamental unit which is managed by the outgoing packet scheduler. David's patches change that idea somewhat, since each transmit queue will need to be scheduled independently. So there is a new netdev_queue structure which encapsulates all of the information about a single transmit queue, and which is protected by its own lock. Multiqueue drivers then set up an array of these structures. So the new data structure can, with sufficient imagination, be seen to look something like this:
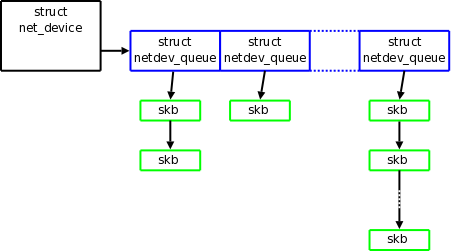
Once again, the actual lists of outgoing packets normally exist in the form of special data structures in device-accessible memory. Once the device has these queues set up for it, the various policies associated with each class of service can be implemented. Each queue is managed independently, so more voice packets can be queued even if some other queue (background, say) is overflowing.
David would appear to have worked hard to avoid creating trouble for network driver developers. Drivers for single-queue devices need not be changed at all, and the addition of multiqueue support is relatively straightforward. The first step is to replace the alloc_etherdev() call with a call to:
    struct net_device *alloc_etherdev_mq(int sizeof_priv,
                                         unsigned int queue_count);
The new queue_count parameter describes the maximum number of transmit queues that the device might support. The actual number in use should be stored in the real_num_tx_queues field of the net_device structure. Note that this value can only be changed when the device is down.
A multiqueue driver will get packets destined for any queue via the usual hard_start_xmit() function. To determine which queue to use, the driver should call:
u16 skb_get_queue_mapping(struct sk_buff *skb);
The return value is an index into the array of transmit queues. One might well wonder how the networking core decides which queue to use in the first place. That is handled via a new net_device callback:
u16 (*select_queue)(struct net_device *dev, struct sk_buff *skb);
The patch set includes an implementation of select_queue() which can be used with WME-capable devices.
About the only other required change is for multiqueue drivers to inform the networking core about the status of specific queues. To that end, there is a new set of functions:
    struct netdev_queue *netdev_get_tx_queue(struct net_device *dev,
                                             u16 index);

    void netif_tx_start_queue(struct netdev_queue *dev_queue);
    void netif_tx_wake_queue(struct netdev_queue *dev_queue);
    void netif_tx_stop_queue(struct netdev_queue *dev_queue);
A call to netdev_get_tx_queue() will turn a queue index into the struct netdev_queue pointer required by the other functions, which can be used to stop and start the queue in the usual manner. Should the driver need to operate on all of the queues at once, there is a set of helper functions:
    void netif_tx_start_all_queues(struct net_device *dev);
    void netif_tx_wake_all_queues(struct net_device *dev);
    void netif_tx_stop_all_queues(struct net_device *dev);
Naturally, there are a few other details to deal with, and the multiqueue interface is likely to evolve somewhat over time. At one point, David was hoping to have this feature ready for inclusion into 2.6.27, but that goal looks overly ambitious now. It does seem that much of the ground work will be merged in the next development cycle, though, meaning that full multiqueue support should be in good shape for merging in 2.6.28.
Enhanced printk() merged
A change very late in the development cycle for 2.6.26 provides a framework for extending printk() to handle new kinds of arguments. Linus Torvalds just merged the change—after -rc9—presumably partially because he knew he could trust the author, but also because it should have no effect on the kernel. It will provide for better debugging output once code is changed to take advantage of it.
The core idea is to extend printk() so that kernel data structures can be formatted in kernel-specific ways. In order to get some compile-time checking, the %p format specifier has been overloaded. For example, %pI might be used to indicate that the associated pointer is to be formatted as a struct inode, which could print the most interesting fields of that structure. GCC will be able to check for the presence of a pointer argument, but because it does not understand the I part, cannot enforce that it is a pointer of the right type.
Extending printk() in this manner allowed Torvalds—who authored the patch—to add two new types to printk(): %pS for symbolic pointers and %pF for symbolic function pointers. In both cases, the code uses kallsyms to turn the pointer value into a symbol name. Instead of a kernel developer having to read long address strings and then trying to find them in the system map, the kernel will do that work for them.
The %pF specifier is for architectures like ppc and ia64 that use function descriptors rather than pointers. For those architectures, a function pointer points to a structure that contains the actual function address. By using the %pF specifier, the proper dereferencing is done.
As an example of how the augmented printk() could be used, Torvalds converted printk_address(). The CONFIG_KALLSYMS dependency and the kallsyms_lookup() were removed, essentially leaving a one-line function:
printk(" [<%016lx>] %s%pS\n", address, reliable ? "": "? ", (void *) address);
If kallsyms is not present, the new printk() just reverts
to printing the address in hexadecimal, which allows the special case
handling to be done there.
The clear intent is to allow additional extensions to printk() to support other kernel data structures. The change to vsprintf(), which underlies printk(), actually allows for any sequence of alphanumeric characters to appear after the %p. The new pointer() helper function currently only implements the two new specifiers, but others have been mentioned.
The mostly likely additions are for things like IPv4, IPv6, and MAC addresses. Torvalds specifically mentions using %p6N as a possibility for IPv6 addresses. Some would rather have seen a different syntax be used, %p{feature} was suggested, but that would conflict with some current uses of %p in the kernel. Torvalds is happy with his choice:
The patch took an interesting route to the kernel, with much of the discussion evidently going on in private between Torvalds, Andrew Morton, and others before popping up on the linuxppc-dev and linux-ia64 mailing lists. The patch itself has not been posted to linux-kernel in its complete form, but was committed on July 6. While it is a bit strange to see such a change this late in the development cycle, it is a change that should have no impact as there are no plans to actually use the new specifiers in 2.6.26.
Patches and updates
Kernel trees
Architecture-specific
Core kernel code
Development tools
Device drivers
Documentation
Filesystems and block I/O
Memory management
Networking
Security-related
Virtualization and containers
Benchmarks and bugs
Miscellaneous
Page editor: Jonathan Corbet
Distributions
News and Editorials
Fedora takes Linux to college
The idea of Linux in the classroom is nothing new. From a grassroots push for district-wide adoption in secondary schools, to a plan to offer the One Laptop Per Child program in every developing country, the FOSS community is always looking for ways to encourage schools to use Linux. Recently, however, there's a new movement afoot that's aimed at snapping up a segment of computer users before they spend their money on computers with commercial operating systems. Linux is headed to college.
For the last few weeks, volunteer members of Fedora's marketing team have been kicking around ideas on ways to encourage college students to give Linux a try and draw new users into the Fedora fold. Rather than approach university IT departments running Windows to convince them to switch operating systems, the team hopes to create a groundswell of college-aged users who will march into classrooms and lecture halls with Fedora-laden laptops and eagerly dive into work-study projects that focus on Linux development.
Jack Aboutboul, Red Hat's Community Engineer and the main impetus behind the tentatively-named Campus Ambassador program, says though it is similar to Fedora's existing Ambassador program, the new program will have a different governance model and slightly different goals. Students from Auburn, Texas A&M, Berkeley, and other U.S. colleges, as well as team members attending universities in other countries, have already shown an interest in assuming the role of Campus Ambassadors, and have agreed to speak at campus events about the benefits of Fedora and of Linux in general.
Taking the idea a step further, many Fedora team members would like to see the development of promotional material designed with college students in mind, such as posters that encourage students in the art department to volunteer their skills creating artwork for Linux distros. As one Fedora marketing team member notes, "How many marketing majors are aware that there are real life marketing opportunities for them within the Fedora project while they are still students? Reaching these students should be one focus of any campus outreach."
At least one school, Cabrillo College in Santa Cruz County, California, is already hard at work promoting Fedora on its campus. In addition to forming a GNU/Linux Users Group (LUG) and holding regular installfests, the LUG is also creating its own Fedora-based distro called Seahawk GNU/Linux, named after the school mascot. LUG President Larry Cafiero explains, "Not that the world needs yet another distro, mind you, but we're using the project as a teaching tool more than an actual distro that will take the world by storm." He says that not only do students gain hands-on familiarity with Linux, but "those who get introduced to GNU/Linux through the school-based distro get a sort of introduction to Fedora as well."
Since Fedora already has a strong Ambassador Program, the question of why a separate university Ambassadorship is necessary has come up. Essentially, it boils down to a difference in how users will be mentored. In the typical Ambassador arrangement, Fedora users simply evangelize Linux and encourage people to give Fedora a try while offering assistance and tips along the way. Marketing team member Chris Tyler sees the role of Campus Ambassador as more finely-tuned and as a "a matchmaker between a student, a potential need (project), and community resources." Tyler says that there are many benefits to this arrangement, including the opportunity for students to work on projects with a larger user base which, will therefore have a bigger real-world impact than student projects that remain inside the walls of the school.
Team member Jeff Spaleta says finding projects with a long shelf life is vital to keeping students interested in Linux, and good for the long-term health of the community. "If students as part of their degrees need to work on a year or semester-long project, I want Fedora to be obvious place to look for compelling things to work on, with an aim towards well scoped projects that have a good chance for long lived utility,
" he says. "I hate seeing good academic projects die because there was no real plan to hand them off outside of that academic group which incubated them.
"
Team members seem to be in agreement that the Ambassador program is a winning situation for everyone. Students get hands-on experience — and, in some cases, a grade — for participating in a software development project. Computer technology departments can offer a wider learning environment with little to no investment, Fedora may garner new users, and the Linux community as a whole grows.
In an effort to move the Campus Ambassador project forward, Jack Aboutboul plans to formally present the idea at a Community Architecture meeting later this month.
New Releases
Gentoo Linux 2008.0 released
Gentoo Linux 2008.0 is out. "Code-named 'It's got what plants crave,' this release contains numerous new features including an updated installer, improved hardware support, a complete rework of profiles, and a move to Xfce instead of GNOME on the LiveCD."
Foresight 2.0.3 Released
The Foresight team has announced the latest release of Foresight. Foresight 2.0.3 GNOME Edition is a minor release, featuring the latest release of GNOME, 2.22.3, which has a new login manager for users, as well as a number of bug fixes and updates.Ubuntu 8.04.1 LTS released
The first maintenance release to the Ubuntu "Hardy" release is available. They've fixed a number of issues, but not all of them... "While we have fixed a number of audio-related issues, including a scheduler problem that caused audio stuttering under load, other audio playback problems may still exist, because so far we have been unable to verify a targeted fix that does not cause regressions for other users."
openSUSE Build Service 1.0
The openSUSE project has announced the 1.0 release of its build service. "The 1.0 release provides all the features necessary to support building openSUSE in the public build systems and allowing direct contributions to openSUSE from all contributors. Developers can now submit contributions to openSUSE directly at build.opensuse.org." The service can also be used to build packages for several other distributions.
Distribution News
Fedora
Rawhide users: brace for a new RPM
Fedora Rawhide users are about to be treated to an "alpha snapshot" of the crucial RPM utility. This is a good thing in the long run; RPM development has been stalled for far too long. But the developers are warning that life could be interesting in the short term. "BACKUP YOUR RPMDB, NOW! We're not aware of any baby-eating bugs in rpm but I'd be shocked if there were no new bugs at all... Better safe than sorry.Fedora Board Recap 2008-JUL-01
Click below for a look at the July 1st meeting of the Fedora Board. Topics include Board Elections, Guarding Privacy and Trademark Guidelines.
Gentoo Linux
New Gentoo council elected
Elections for Gentoo council are finished. The newly elected council members are Donnie Berkholz, Mark Loeser, Diego Pettenò, Petteri Räty, Luca Barbato, Markus Ullmann, and Tobias Scherbaum.
Distribution Newsletters
Ubuntu Weekly Newsletter #98
The Ubuntu Weekly Newsletter for July 5, 2008 covers: Ubuntu 8.04.1 LTS released, Intrepid Alpha 2 due out Thursday, Ubuntu Brainstorm, Two new Ubuntu Teams, Kubuntu Intrepid News, Ubuntu Nicaragua TV show, Launchpad 1.2.6 released, Launchpod episode #6, New Ubuntu Forums Interviews Host, Ubuntu-UK podcast #9, and much more.OpenSUSE Weekly News/29
This issue of the OpenSUSE Weekly News looks at openSUSE 11.1 Roadmap, Novell Client for Linux Public Beta for openSUSE 10.3, People of openSUSE: Jan-Simon Möller, John Anderson: Find duplicate files by content not name, Lukas Ocilka: Package Search and One Click Install in YaST, Miguel de Icaza: Moonlight 0.7 is now Available, and several other topics.Fedora Weekly News Issue 133
The Fedora Weekly News for July 5, 2008 looks at Planet Fedora articles "Func and Certmaster 0.20 Released", "Transifex receives some updates", "Inkscape tutorials", "New Fedora business cards", and "Bug Triage meeting", plus Fedora reviews, Help Wanted at the Utah Open Source Conference, Development articles "SELinux Eats Babies, Confines Wives, Gives Birth", "Help Wanted: Samba4, Heimdahl, OpenChange", "Java, So Many Free Choices", "Fedora 9 Now Officially Supported On Itanium/IA64", and "Running As Root", and several other topics.DistroWatch Weekly, Issue 260
The DistroWatch Weekly for July 7, 2008 is out. "What were the most exciting Linux events of the first half of 2008? The continued success of Linux on ultra-portable laptops? The arrival of KDE 4? The miscellaneous distribution releases? Our lead article takes a quick look at the most interesting events in the Linux world that shaped the year so far. In the news section, the first stable release of Gentoo Linux in 14 months hits the download servers, Ubuntu receives high marks from French legislators, Xandros acquires Linspire and its software assets, PC-BSD releases the first BSD with integrated KDE 4.1, and OpenBSD prepares for the forthcoming release of symbolic importance - version 4.4. Also not to be missed, news about Ikki Boot, a compilation CD with an excellent collection of rescue utilities, and the latest distro statistics from this site's web server logs. Finally, we are pleased to announce that the recipient of the DistroWatch.com's monthly donation for June 2008 is the MythDora project."
Debian Misc developer news (#9)
This edition of Misc developer news has some advice on quilt usage, plus update-grub starts using UUIDs by default, wxwidgets2.8 upload to unstable, and Volunteers needed to handle update of release notes.
Distribution meetings
Next Ubuntu Developer Summit
The next Ubuntu Developer Summit (UDS) has been scheduled for December 8 - 12, 2008 at the Google Campus, Mountain View, California, USA. The primary topic will be version 9.04. See the UDS wiki for more information.
Interviews
People of openSUSE: Joe Brockmeier
Here's a People of openSUSE interview with Joe Brockmeier, openSUSE community manager. "What especially motivates you to participate in the openSUSE project? I want to see openSUSE become a more independent project, to allow external contributors to have a strong voice in its development and direction, and I want to see as many people as possible introduced to Linux through openSUSE."
Page editor: Rebecca Sobol
Development
What's coming in OpenSSH 5.1
OpenSSH is an important
tool for remote connectivity:
"OpenSSH is a FREE version of the SSH connectivity tools that technical users of the Internet rely on. Users of telnet, rlogin, and ftp may not realize that their password is transmitted across the Internet unencrypted, but it is. OpenSSH encrypts all traffic (including passwords) to effectively eliminate eavesdropping, connection hijacking, and other attacks. Additionally, OpenSSH provides secure tunneling capabilities and several authentication methods, and supports all SSH protocol versions.
"
On July 6, 2008 a
call for testing was issued for OpenSSH version 5.1:
"OpenSSH 5.1 is almost ready for release, so we would appreciate testing
on as many platforms and systems as possible. This release is one of
the biggest in recent years, with two hackathons' worth of improvements
and fixes for some of our most recalcitrant bugs.
"
A large number of new features are being added to the OpenSSH suite of utilities. Some of the feature highlights include:
- Experimental SSH fingerprint visualization (see this paper [pdf]) will produce visual representations of host keys for quick key validation.
- The sshd daemon will get a new extended test mode with capabilities for dumping the configuration and testing match rules.
- A "df" command has been added to the sftp client for displaying server filesystem information.
- There will be a new mechanism for disabling further session requests between ssh and sshd.
- The ssh-keygen command will get a new -l option that will allow searching for a host in the known_hosts file.
- ssh and sshd will better support port forward destination hosts with multiple forward addresses.
- Some basic interoperability tests have been added for Twisted Conch.
- Configuration file changes:
- Classless Inter-Domain Routing (CIDR) address/masklen matching will be added to sshd_config "Match address" blocks and authorized_keys "from" restrictions.
- A new sshd_config AllowAgentForwarding option will control authentication agent forwarding.
- The sshd_config MaxSessions option will give finer grained control to the number of multiplexed sessions.
- sshd_config "Match group" blocks will get new support for group negation.
- sshd_config match blocks will now support the MaxAuthTries option.
- Performance improvements.
- Documentation improvements.
- Bug fixes.
For those who would like to experiment with the new features, a series of snapshot releases are available for download.
System Applications
Database Software
PostgreSQL Weekly News
The July 6, 2008 edition of the PostgreSQL Weekly News is online with the latest PostgreSQL DBMS articles and resources.
Filesystem Utilities
g4l: verison 0.26 released (SourceForge)
Version 0.26 of g4l has been announced. "G4L is a hard disk and partition imaging and cloning tool. The created images are optionally compressed and transferred to an FTP server instead of cloning locally. Latest changes with 0.26: added mdev as hotplug program, updated ntfs-3g, kernel 25.9, busybox 1.11.0 with patches to 7/02/2008, g4l30 script that shows partition size and type, added sfdisk and fsck programs."
Interoperability
Samba Team Releases Samba 3.2
Version 3.2 of Samba has been announced. "Samba 3.2 builds upon the success of Samba 3.0 by modernizing and enhancing the code whilst still retaining compatibility with all existing Samba installations."
LDAP Software
python-ldap 2.3.5 released
Version 2.3.5 of python-ldap has been announced, it includes several bug fixes. "python-ldap provides an object-oriented API to access LDAP directory servers from Python programs. It mainly wraps the OpenLDAP 2.x libs for that purpose. Additionally it contains modules for other LDAP-related stuff (e.g. processing LDIF, LDAPURLs and LDAPv3 schema)."
Mail Software
Vacation 1.2.7.0 released
Version 1.2.7.0 of vacation has been announced, Chris Samuel has stepped up as the maintainer of the SourceForge version "This is a complete rebase of the current Vacation code base from the closely related version at http://savannah.nongnu.org/cvs/?group=vacation which had been released under the two clause BSD license (no advertising clause). This means Vacation finally links legally with the GPL's GDBM (something I don't believe people previously realised)!"
Web Site Development
dobrado: 0.10 released (SourceForge)
Version 0.10 of dobrado has been announced. "Dobrado is an easy to use online website creator. There are no templates, just drag and drop content anywhere on the screen. This release of Dobrado allows the system to be used as a wiki, with user defined copy and edit permissions, and undo/redo from history log."
scgi 1.13 announced
Version 1.13 of scgi has been announced, some new capabilities have been added. "The SCGI protocol is a replacement for the Common Gateway Interface (CGI) protocol. It is similar to FastCGI but is designed to be easier to implement. The scgi package includes implementions of the SCGI protocol for Python, Apache 1 and Apache 2."
Desktop Applications
Audio Applications
jack_capture V0.9.19, Snd-ls V0.9.8.17 and Rollendurcmesserzeitsammler V0.0.4
New versions of jack_capture, Snd-ls and Rollendurcmesserzeitsammler have been announced. "jack_capture is a program for recording soundfiles with jack. Snd-ls is a distribution of Bill Schottstaedt's sound editor SND. The Audio Rollendurchmesserzeitsammler is a conservative garbage collector providing general ways to efficiently allocate and use memory inside a realtime audio thread without having to manually free it later."
SLV2 0.6.0 announced
Version 0.6.0 of SLV2, a library for accessing LV2 audio plugins, is out with several new capabilities and bug fixes.
Desktop Environments
GNOME 2.22.3 released
Version 2.22.3 of the GNOME desktop environment has been announced. "This is the third update to GNOME 2.22. This includes all the bug fixes, all the new translations, updated documentation and other improvements made by the various GNOME teams since the last stable release."
GARNOME 2.22.3 released
Version 2.22.3 of GARNOME, the bleeding edge GNOME distribution, has been announced. "It includes a wealth of new application releases, updated translations and bug fixes as part of this GNOME release -- as well as updates and fixes after the GNOME freeze and a host of third-party GNOME packages."
GNOME Software Announcements
The following new GNOME software has been announced this week:- Brasero 0.7.91 (new features and bug fixes)
- cluttermm 0.7.0 (new features and bug fixes)
- GLib 2.16.4 (bug fixes and translation work)
- GLib 2.17.3 (bug fixes and translation work)
- glibmm 2.16.4 (bug fix)
- gnome-mag 0.15.1 (bug fix and translation work)
- GTK+ 2.13.4 (new features, bug fixes and translation work)
- Guile-Gnome-Platform 2.16.1 (bug fixes and documentation work)
- MonoDevelop 2.0 Alpha 1 (new features)
KDE Commit-Digest (KDE.News)
The June 1, 2008 edition of the KDE Commit-Digest has been announced. The content summary says: "Amarok 2 gets basic video playing support, and a connection to Librivox public domain audio books. Major porting to KDE 4 continues in K3b. More work on "Fuzzy Search" integration in Digikam. The start of support for sound effects in KGoldRunner, and the addition of a sound feature in KPresenter. Improvements in the msword-odf and kpr-odf import facilities in KOffice..."
KDE Software Announcements
The following new KDE software has been announced this week:- Darkstat Plasma Applet 0.01 (initial release)
- digiKam 0.9.4-rc2 (new features and bug fixes)
- digiKam 0.10.0-beta1 (new features and bug fixes)
- eXaro 1.0.0 (bug fixes and translation work)
- GLAN 0.5.2 (unspecified)
- Kate LaTeX typesetting plugin 0.1 (initial release)
- kdebluetooth4 0.1 (initial release)
- KlamAV 0.44 (new features and bug fixes)
- Kopete Antispam Plugin 0.3 (new features)
- KopeteLogMerge 0.0.1 (initial release)
- KPackageKit 0.1-b3 (third beta)
- KRename 3.9.1 (new features and bug fixes)
- NoteFinder 2.6 (new features)
- NoteFinder 2.7 (new feature)
- SMILE 0.3.1 (bug fixes and performance improvements)
- TorK 0.29.1 (bug fixes)
- trix 0.94 (bug fix)
Xorg Software Announcements
The following new Xorg software has been announced this week:- libXfont 1.3.3 (bug fixes)
- libXft 2.1.13 (bug fixes)
- libXrandr 1.2.3 (bug fixes)
- libXxf86vm 1.0.2 (bug fixes)
- randrproto 1.2.2 (bug fixes)
- xf86-video-mga 1.4.9 (new features and bug fixes)
- xtrans 1.2.1 (bug fixes)
Financial Applications
SQL-Ledger version 2.8.16 released
Version 2.8.16 of SQL-Ledger, a web-based accounting system, has been announced. Changes include: "Added quantity, warehouse when checking for obsolete parts Added array initialization for perl 5.10. Fixed sales invoice import to separate invoices by invoice number for the same customer. Fixed wrong number assignment when printing/posting vendor invoice. Fixed several formatting errors when number format set to European format. Added default ship to address for generated purchase orders."
Games
New WorldForge releases
The WorldForge virtual world project has announced several new software releases. Ember 0.5.3: "Ember is a 3d client for the WorldForge project. It uses the Ogre 3d graphics library for presentation and CEGUI for its GUI system. This release fixes a couple of memory leaks and improves memory handling overall, as well as some problems with Ogre 1.4.8+ and CEGUI 0.6.1+."
WOMBAT 0.1.0:
"Im happy to announce the first alpha release of WOMBAT.
WOMBAT provides a nicer web frontend to the WorldForge media repository.
"
WOMBAT 0.1.1:
"Thanks to Thomas Ingham aka. magnethead, WOMBAT now uses CSS instead of tables for layout elements. While he was at it, Tom also revamped the colour scheme.
"
Multimedia
Oggz 0.9.8 Released
Version 0.9.8 of Oggz a collection of tools for working with Ogg media, has been announced. "This release adds a new oggz-chop tool, which can be used to serve time ranges of Ogg media over HTTP."
Music Applications
Patchage 0.4.1 released
Patchage version 0.4.1 has been released. "Patchage is a graphical modular patch bay for audio/MIDI systems based on JACK, LASH, and ALSA. This release fixes several bugs, and adds support for the new Jack D-Bus control interface. Two libraries which Patchage depends on are also released in parallel: raul 0.5.0 and flowcanvas 0.5.0."
rakarrack: 0.2.0 is released (SourceForge)
Version 0.2.0 of rakarrack has been announced. "Rakarrack is a jack guitar FX processor emulator. Lineal and Parametric EQ, Distortion, Overdrive, Echo, Chorus, Flanger, Phaser, Compressor, Reverb, WahWah, Alienwah, NoiseGate, Harmonizer, Musical Delay, Pan, Cabinet. Tuner and MIDI Converter. Seven new effects including Harmonizer, Musical Delay, Cabinet emulation, NoiseGate, AutoPan/Extra Stereo, WahWah, AlienWah. Better look with new widgets, color customization. More MIDI control."
PDA Software
palmBTremote: Version 0.2 available (SourceForge)
Version 0.2 of palmBTremote has been announced, it features some code cleanup. "palmBTremote contains both client and server side components to allow remote control of totem and MythTV from your palmOS device over bluetooth."
Science
FreeEOS-2.2.1 has been released (SourceForge)
Version 2.2.1 of FreeEOS has been announced. "FreeEOS is a software library for calculating an equation of state for conditions in stellar interiors. The latest stable version of this library source code, FreeEOS-2.2.1, has been released on 2008-07-08. The new release fixes all known bugs in FreeEOS-2.2.0".
Speech Software
PocketSphinx: 0.5 release (SourceForge)
Version 0.5 of PocketSphinx has been announced. "Sphinx is a speaker-independent large vocabulary continuous speech recognizer released under a BSD style license. It is also a collection of open source tools and resources that allows researchers and developers to build speech recognition systems. The newest stable version of PocketSphinx is now available. This release is about 50% smaller and up to 18% faster than the previous one, and introduces a new, re-entrant and "modern" API."
Languages and Tools
Caml
Caml Weekly News
The July 8, 2008 edition of the Caml Weekly News is out with new articles about the Caml language.
Haskell
Shells
CODESH: 1.4.0 released (SourceForge)
Version 1.4.0 of CODESH has been announced. "CODESH (COllaborative DEvelopment SHell) is an automatic persistent logbook for sessions of personal command line work. It records what and how is being done, for private use/reuse and for sharing selected parts with collaborators. It is an intelligent shell that automatically logs user's shell sessions. Sessions are uniquely tagged and stored in local or distributed backend repositories (ASCII flat file or Subversion or CVS based) and can be extracted and reproduced at any time by the user who created the session or by collaborators located anywhere in the world. The focus of this version is the distributed computing (remote) aspects of CODESH."
IDEs
eric 4.1.6 released
Version 4.1.5 of eric, a Python IDE written using PyQt4 and QScintilla2, is out with bug fixes.
Test Suites
Linux Desktop Testing Project 1.2.0 released
Version 1.2.0 of the Linux Desktop Testing Project, a test automation framework for desktop applications, has been announced. "This release features number of important breakthroughs in LDTP as well as in the field of Test Automation. This release note covers a brief introduction on LDTP followed by the list of new features and major bug fixes which makes this new version of LDTP the best of the breed,"
Version Control
GIT 1.5.6.2 announced
Version 1.5.6.2 of the GIT distributed version control system has been announced, numerous bug fixes are included. "There still are a handful more fixes queued for 'maint' so we might see another maintenance release, 1.5.6.3, not too far in the future."
Miscellaneous
Google releases Protocol Buffers
Google has announced the release of its "Protocol Buffers" code under the Apache license. "Protocol Buffers allow you to define simple data structures in a special definition language, then compile them to produce classes to represent those structures in the language of your choice. These classes come complete with heavily-optimized code to parse and serialize your message in an extremely compact format." In other words, it's another XDR/RPC/pickle implementation, but tuned to Google's performance needs.
Page editor: Forrest Cook
Linux in the news
Recommended Reading
First Look: OpenMoko's Linux-based open smartphone platform (ars technica)
ars technica has posted a detailed look at the software choices available for the OpenMoko FreeRunner phone. "There are currently three separate software stacks that are available for OpenMoko handsets. The original OpenMoko software environment was built on top of GNOME Mobile and Embedded technologies including the GTK+ toolkit. As the FreeRunner launch date approached and the development priorities began to shift towards a stronger emphasis on mainstream consumer adoption, OpenMoko reevaluated its approach and decided to build a new stack on top of Trolltech's proven Qtopia mobile environment. The third stack, which will implement the FreeSmartphone.org APIs, is part of a long-term framework initiative that OpenMoko hopes will eventually ameliorate the problems created by fragmentation and redundancy while still offering developers a full range of choices."
Linux Adoption
Invitrogen buys into Novell's SUSE Linux (c|net)
c|net reports on Invitrogen's switch to servers running SUSE Linux. "Invitrogen is a billion-dollar supplier to pharmaceutical and biotechnology companies, with 4,700 employees worldwide and a history of supplying many of the world's leading laboratories in groundbreaking research like the discovery of the AIDS virus. To help promote its innovative work, Invitrogen announced this week that it is standardizing on Novell's SUSE® Linux Enterprise for its servers."
Move Your Business from Windows to Linux (PC World)
It often seems that the mainstream technical press focuses on various "problems" with Linux, either technical or otherwise, which is what makes this PC World article stand out. It is a basic introduction to Linux for businesses that might be looking to switch from Windows, especially for the cost savings. "If that feels like a waste of your small business's precious IT budget, and you're still looking for an alternative to Windows Vista, look no further than Linux. The latest distributions are free, easy to install, and highly customizable; they harness your existing hardware without overtaxing it; and they include a wealth of productivity applications and utilities. You may already have a closet Linux expert on staff, but if you don't, paid support is usually available at rates far less than Microsoft's."
Legal
Reiser leads police to wife's body (MercuryNews)
This MercuryNews article would appear to bring an end to the speculation on whether Hans Reiser was really guilty. "Accompanied by heavily armed Oakland police, software programmer Hans Reiser on Monday led authorities to the body of his missing wife, buried in a shallow grave in the Oakland hills."
Resources
GNU/Linux free software tools to preserve your online privacy, anonymity and security (FSM)
Free Software Magazine looks at some free software tools to protect freedom. "Whether you are online or offline, freedom matters. Like good health you never think about it or miss it until it is under threat or actually gone. If you love freedom, you probably love free software and it has given us some terrific tools with which to defend freedom. In this article I will give an overview of some of the available resources (Freenet, Wikileaks and Tor) to protect dissident opinion, facilitate whistle blowing and promote the safe and anonymous development of free software."
Reviews
KDE 4.1 Beta 2: Two Steps Forward, One Step Back (Datamation)
Datamation reviews the second KDE 4.1 beta. "However, if the second beta of 4.1 is any indication, it will be only partly successful in quieting user dissent. On the one hand, KDE 4.1 includes the first 4.x versions of several major KDE applications, which goes a long way toward improving the user experience. And, in both other programs as well as the desktop, the second beta sports countless improvements in functionality and design. On the other hand, not only are many of the interface changes that people complain about still there, but the new Folder View raises a whole new set of issues about how users organize their desktops."
KOffice 2 Alpha 8 Reviewed (TechWorld)
TechWorld takes a look at KOffice 2.0 Alpha 8. "KOffice 2.0 Alpha 8 ships as a suite of applications. In addition to the familiar word processor (KWord), spreadsheet (Kspread) and charting (Kchart), and presentation applications (KPresenter), KOffice has a wealth of tools for content design, manipulation and display. For the creative professional, there's Krita a fully-fledged graphic design and image manipulation tool, Karbon14 a Scalable Vector Graphics editor, and Kivio for flowcharts and diagrams. Also included is Kexi for database development (touted as "Microsoft Access for Linux"), and KPlato for project management. Other tools are KnetAttach, a network folder wizard, Kformula for mathematical formula editing, and a thesaurus." (Found on KDE.News)
Acer's Linpus Linux Lite (Fedora) ultra portable laptop piles the pressure on Microsoft (FSM)
Free Software Magazine reviews the Acer Linpus Linux Lite ultra portable laptop. "It is due to launch here in the UK in early July with the GNU/Linux version with a price tag of £199. (Yes, surprise, surprise, theyre offering Windows XP too.) Given the specification (Intel atom N270 chip, 8.9 inch screen, webcam, 1024 x 600 resolution, 8GB SSD, three USB ports, VGA, and two SD card slots, two mini PCI slots (one for the WiFi and one for upcoming Wimax or HSDPA), Ethernet port, touchpad, 802.11b/g WiFi and a default 512MB of memory with a spare slot to add more) the Aspire One represents stonking good value for money."
Page editor: Forrest Cook
Announcements
Non-Commercial announcements
BitNami.org hits 150,000 downloads
The BitNami project has announced reaching the 150,000 download mark. "The BitNami project, sponsored by BitRock, released a new modular architecture for its open source application stacks. It is now easier than ever to install and configure applications such as Wordpress, Drupal, eZ Publish on Windows, Linux, OS X or Solaris."
Commercial announcements
Purple Labs acquires mobile browser business from Openwave
Purple Labs has announced the acquisition of Openwave Systems' mobile software business. "Purple Labs, a French developer of Linux-based mobile software, today announced that it has completed its acquisition of the mobile client software business of California-based Openwave Systems, in an asset sale valued at more than $32 million. The browser and messaging products acquired in the deal are among the best-selling mobile applications in the world, having already shipped in more than 1.5 billion mobile phones. Following the acquisition, Purple Labs now supplies mobile browser software to all of the top 5 phone manufacturers, which together produce over 80% of the worlds mobile phones."
New Books
The Software Test Engineer's Handbook--New from Rocky Nook
Rocky Nook has published the book The Software Test Engineer's Handbook by Graham Bath and Judy McKay.
Resources
Linux Gazette #152
Issue #152 of the Linux Gazette has been published. Topics include: "* Mailbag * Talkback * 2-Cent Tips * News Bytes, by Deividson Luiz Okopnik * Review of the Plat'Home OpenBlockS, by Ben Okopnik * Apertium: Open source machine translation, by Jimmy O'Regan * Joey's Notes: Access Control Lists, by Joey Prestia Our monthly column of basic Linux advice and education * Wireless Configuration for Desktops, by Muthaiah Ramanathan Five easy steps to configure a PCI wireless card in desktops running GNU/Linux * A slightly advanced Introduction to Vim, by Pranesh Srinivasan * XKCD, by Randall Munroe * HelpDex, by Shane Collinge * Ecol, by Javier Malonda"
Contests and Awards
Nominations open for Pwnie Awards 2008
Nominations are open for the 2008 Pwnie Awards. "The Pwnie Awards ceremony will return to the BlackHat USA 2008 conference in Las Vegas. Last year's inagural event was a lot of fun, and we hope it will only get better. What should you expect from this year's ceremony? Exciting new categories, an inspirational acceptance speech by the winner of the Lamest Vendor Award and a special sing-along lead by HD Moore!" Nominations are due by July 14.
Education and Certification
Opera brings Web standards to classrooms worldwide
Opera Software has announced a web standards education program. "Opera today launched a sweeping education initiative aimed at supporting and enhancing Web standards education and training in secondary schools, colleges, universities and businesses worldwide. The first planned step in this initiative is the Opera Web Standards Curriculum, a complete curriculum of learning material to provide a thorough understanding of client-side Web design and development from the ground up. These materials are available completely free under a Creative Commons license from http://www.opera.com/wsc/."
Calls for Presentations
2008Q3 Call for Grant Proposals (use Perl)
use Perl has announced a call for grant proposals. "The Perl Foundation is looking at giving some grants ranging from $500 to $3000 in August 2008. In the past, we've supported Adam Kennedy's PPI and Strawberry Perl, Nicholas Clark's work on Perl internals, Jouke Visser's pVoice, Chris Dolan on Perl::Critic and many others (just check http://www.perlfoundation.org/grants for more references). You don't have to have a large, complex, or lengthy project. You don't even have to be a Perl master or guru. If you have a good idea and the means and ability to accomplish it, we want to hear from you! Do you have something that could benefit the Perl community but just need that little extra help? Submit a grant proposal by July 31."
Linux.conf.au 2009 Call for Papers
A call for papers has gone out for Linux.conf.au. "Linux.conf.au has announced the opening of the call for papers on Friday 4th July 2008, giving the open source software community the chance to present at one of the world's premier technical conferences. Hobart TAS, Australia-- (4th July 2008) ---- The call for papers will remain open for a month, after which the best papers will be selected by an expert panel."
Call for Papers for the MEITSEC 2008 is now open
A call for papers for the 2008 MEITSEC conference has been announced. "The Call for Papers for the MEITSEC 2008 to be held in Dubai is now open. MEITSEC 2008 will be held at the Etisalat Academy from 16 to 20 November 2008. The event will consist of three-day pre-conference workshops, and a two-day conference and exhibition." The submission deadline is July 31.
Power management microconf at Plumbers Conference, CFP
A Power management microconf has been announced, papers are being accepted until July 20. "As a complement to the PM miniconf at OLS, there will be a power management microconference as part of the Linux Plumbers Conference in Portland between September the 17th and 19th. Rather than looking at purely kernel or userspace issues, the focus of the conference will be on the interaction between the two. We're interested in discussion of what needs to be exposed by the kernel to facilitate maximum power savings, and also what userspace needs to do to take advantage of that."
Upcoming Events
Akademy 2008 Talks Program Published (KDE.News)
KDE.News has announced 2008 Akademy conference program. "Track themes include research, applications and community. There are keynotes from Frank Karlitschek of the Open Desktop sites, Sebastian Nyström of Nokia, Cliff Schmidt of KDE users Literacy Bridge. Lightning talk sessions include a Plasma Frenzy and an Akonadi Rumble with KDAB's Till Adam. It is a packed programme to start off the week, the rest of which will be filled with BoFs, Tutorials and an Embedded and Mobile Day."
Connecting California to Improve Patient Care in 2008 (LinuxMedNews)
LinuxMedNews has announced the Connecting California to Improve Patient Care in 2008 conference. The event "will occur on Friday July 18, 2008 -- 9:00 A.M. to 4:15 P.M. Ukiah Valley Conference Center, 200 S. School St., Ukiah, California Conference Cost - $35 (includes lunch). This looks like one of those small conferences that end up becoming very important."
Linux Installfest workshop in Davis, CA - July 19th
The Linux Users' Group of Davis will hold the next Linux Installfest workshop in Davis, California on Saturday, July 19.Events: July 17, 2008 to September 15, 2008
The following event listing is taken from the LWN.net Calendar.
| Date(s) | Event | Location |
|---|---|---|
| July 14 July 18 |
PHP 5 & PostgreSQL Bootcamp at the Big Nerd Ranch | Atlanta, USA |
| July 18 July 20 |
RubyFringe | Canada, Toronto |
| July 19 | Firebird Developers Day | Piracicaba-SP, Brazil |
| July 19 July 25 |
Ruby & Ruby on Rails Bootcamp at the Big Nerd Ranch | Atlanta, USA |
| July 19 July 20 |
LugRadio Live 2008 - UK | Wolverhampton, United Kingdom |
| July 20 | OSCON PDXPUG Day | Portland, OR, USA |
| July 21 July 25 |
O'Reilly Open Source Convention | Portland, OR, USA |
| July 21 July 22 |
Ubuntu Live - cancelled | Portland, Oregon, USA |
| July 23 July 26 |
Ottawa Linux Symposium | Ottawa, Canada |
| July 26 | PyOhio 2008 | Columbus, OH, USA |
| July 26 July 27 |
EuroSciPy2008 | Leipzig, Germany |
| August 1 | LLVM Developers' Meeting | Cupertino, CA, USA |
| August 3 August 9 |
DebCamp 2008 | Mar del Plata, Argentina |
| August 4 August 7 |
LinuxWorld Conference & Expo | San Francisco, CA, USA |
| August 9 August 16 |
Akademy 2008 | Sint-Katelijne-Waver, Belgium |
| August 9 August 17 |
Linuxbierwanderung (Linux Beer Hike) | Samnaun/Compatsch, Switzerland |
| August 10 August 16 |
Debian Conference 2008 | Mar del Plata, Argentina |
| August 11 August 15 |
SAGE-AU'2008 | Adelaide, Australia |
| August 12 August 14 |
Flash Memory Summit | Santa Clara, CA, USA |
| August 13 August 15 |
YAPC::Europe 2008 | Copenhagen, Denmark |
| August 18 | Debian Day | Buenos Aires, Argentina |
| August 19 August 24 |
SciPy 2008 Conference | Pasadena, CA, USA |
| August 20 August 22 |
Jornadas Regionales de Software Libre | Buenos Aires, Argentina |
| August 23 August 24 |
FrOSCon 2008 | Saint Augustin, Germany |
| August 26 August 29 |
WebGUI Users Conference 2008 | Madison, WI, USA |
| August 27 August 30 |
Drupalcon Szeged 2008 | Szeged, Hungary |
| August 28 August 30 |
Utah Open Source Conference 2008 | Salt Lake City, UT, USA |
| September 2 September 4 |
RailsConf Europe 2008 | Berlin, Germany |
| September 5 September 7 |
FUDCon Brno 2008 | Brno, Czech Republic |
| September 6 September 7 |
DjangoCon 2008 | Mountain View, CA, USA |
| September 7 September 10 |
Workshop on Open Source Software for Computer and Network Forensics | Milan, Italy |
| September 7 September 14 |
Python Game Programming Challenge | Online |
| September 8 | Encontro Nacional de openSUSE | Porto, Portugal |
| September 9 September 11 |
EFMI STC 2008 | London, England |
| September 12 September 14 |
The UK Python Conference | Birmingham, England |
If your event does not appear here, please tell us about it.
Page editor: Forrest Cook