

LWN.net Weekly Edition for October 8, 2026
Welcome to the LWN.net Weekly Edition for October 8, 2026
This edition contains the following feature content:
- Coping with the onslaught of kernel security bugs: how the kernel's security team is handling the flood of LLM-assisted bug reports.
- Last rites for Gentoo's Chromium package: challenges in packaging Chromium for the distribution have finally taken their toll on Gentoo's volunteer packagers.
- Beyond the &: making smart pointers as flexible as built-in references for Rust.
- An update on the Sashiko patch-review system: Roman Gushchin highlights how the review system works as well as improvements being made.
- Analyzing Rust programs with Charon: toward providing a stable API for accessing internal information from the Rust compiler.
- Evolving the LAVD scheduler from gaming to servers: how the LAVD scheduler continues to improve.
- Python's two modules for random numbers: all random-number generators are not created equal.
This week's edition also includes these inner pages:
- Brief items: Brief news items from throughout the community.
- Announcements: Newsletters, conferences, security updates, patches, and more.
Please enjoy this week's edition, and, as always, thank you for supporting LWN.net.
Coping with the onslaught of kernel security bugs
By now it is no secret that large language models (LLMs) have made it easy for people to identify security bugs, and that has resulted in a flood of bug reports to almost every free-software project, including the kernel. At the 2026 edition of Kernel Recipes, Greg Kroah-Hartman took the stage to talk about how the kernel's security team is handling this deluge. His core message was "don't panic".
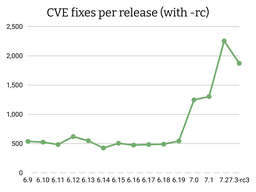 Kroah-Hartman started with a plot of the number of kernel CVE
numbers that were fixed with each release; a version of that plot appears
to the right. The trend is clear: after running at a steady rate of about
500 fixes per release, that number has suddenly quadrupled. Not that long
ago, he said, the old rate, being about 50 fixes per week, seemed
incredible. Now the kernel project is fixing 33 CVEs per day.
Something has changed; that something is, of course, the advent of LLMs.
The good news is that the preparation work done in the kernel community has
paid off, and the tooling is able to scale to this level of activity.
Other projects are in a panic, but "
we're doing fine, and could go
faster
".
Nobody should panic, he emphasized, this flood is not a big problem. There
is a lot of coverage in the press, and a lot of "doom marketing
",
but we should just ignore it. As an example of how this marketing works,
he recounted an episode where he got a phone call informing him that the
Mythos LLM had found 79 Linux kernel vulnerabilities. After being
concerned initially, he obtained access to the raw data, which he is now
able to talk about. This set of alleged vulnerabilities was found by
looking at old bug fixes and finding other places with similar problems,
mirroring work by people like Julia Lawall and Sasha Levin in the past.
Of those 79 bugs, 24 had no detail beyond "something crashed
".
Another 14 were simply not bugs, and three were the result of made-up data
and were fake from the beginning. There were 15 that were real bugs — but
they had already been fixed in the current kernel release. That last set,
he said, is typical of these tools; they are sycophantic and will work hard
to find bugs if asked. They will even read the mailing lists to find and
report bugs that have been fixed by others. This pattern of "finding" bugs
that others have already reported is quite common.
That leaves 26 that were actual bugs needing attention — almost. Six of those were duplicates. And, he noted, the total doesn't add up to 79; LLMs are not always good at basic math. So 20 bugs needed fixes; of those, seven were only exploitable by way of a malicious filesystem image, something that the kernel community has long documented as not actually being a security issue. Two bugs required the ability to inject a malicious packet into the middle of the network stack, something that can only be done by root, so these were not real bugs. Two others only affected NOMMU systems (those without a memory-management unit); one of those was in io_uring. Nobody, he suspects, uses io_uring on NOMMU systems. He has fixed both bugs, but the fixes are not upstream yet, nobody really cares much about security on NOMMU systems. There were two minor IPv6 issues, and one that allowed a malicious local user to compromise the system via the GPU — but that user would already be capable of doing far worse.
The end result is that this exercise resulted in ten real bug fixes, in a project that is merging a little over ten patches every hour. So addressing it represented one hour of the kernel community's work.
The real problem
The problem that we should be worried about, he said, is the mean time to exploit — the time between the discovery of a bug and the appearance of exploits for it. In 2018, that time was 63 days; in 2026 it is 7 days. So this problem is real, but the biggest problem is that people are just not updating their systems. Running old software is a luxury many of us do not have anymore.
 The bill is finally coming due for many years of underinvestment; our
software simply was not designed for perfect security. Now we're going to
have to grind through this phase of bug discovery. But this is something
we have seen before; the advent of fuzzers years ago also resulted in a
flood of bugs needing fixes. We did the work, dealt with those bugs, and
the flow of fuzzer-discovered bugs eventually dropped considerably. When
you fix all the bugs, he said, the reports stop.
As an example, consider rsync. Andrew Tridgell worked his way through all of the reported bugs (taking some grief along the way), and now all of the code scanners declare that rsync is clean.
He paused for a moment to reflect on the recent reports of communications within Microsoft suggesting that at least some executives there were concerned that their models were stealing much of the data they absorbed. A report from LG Research, he said, suggested that only 20% of the data used at LG for model training was legally obtained. We may not like how these tools were created, but we can make use of them to help make our software better.
That said, not everybody is working toward that goal. There are people flooding the kernel lists with patches, often hundreds per day; these patches are untested at best. We should just ignore them. The best models, he said, are still wrong 50% of the time, so we should just assume that 50% of LLM-generated patches are wrong. We do not have to just accept them. There are some patterns that can often be seen in LLM-generated code. For example, the models often want to replace, incorrectly, calls to mutex_unlock() with mutex_destroy(). They generate highly verbose and useless changelogs, and add far too many comments to the code.
When people have tried to create bots that are better at creating kernel
code, they have often started by training those bots on the kernel's
development history. But that history demonstrates a lot of patterns that
the community has long since left behind; it is full of bad examples. What
those bots produced, he said, was "bad code that cursed
".
Maintainers should not fear to push back when they see this kind of code.
Often the best question to ask is "how did you test it?". One should also
bear in mind that these systems leak; anything they tell you will be told
to others as well. Anything you upload into them will be handed out to
others. That is how researchers continually "discover" bugs that were
publicly reported a day earlier.
The future for these tools, he said, is not bright. For years, Coverity developed a code-scanning tool that produced many high-quality reports, and it was deterministic as well. But the company never managed to make money; people are not willing to pay for this kind of tool. The current tools, he predicted, will meet the same fate. Nobody wants to pay for code-quality tools when they work well, they certainly won't pay for tools with a 50% error rate.
Adaptation
So how is the kernel community adapting to this situation? One useful effort has been improving the documentation of the kernel's threat model; sometimes, the bots actually read that material, and patch submitters can be pointed to it in the remaining cases. The security-related documentation now requires that maintainers be copied on security reports; any sort of attempt to keep a lid on this information is doomed to fail. Reporters are also requested to submit an initial fix with their report; they can always ask their LLM to create that patch, and it helps kernel developers come up with a proper fix. He said that there is also now funding for a full-time developer to work on reports sent to security@kernel.org.
Developers and maintainers can push back on both bug reporters and patch
submitters; if they don't respond to questions, developers do not have to
respond to them. For their own testing, he said, developers should run local
models; they are good enough for the job, and non-public information should
never be uploaded to a non-local system. And, of course, "fix the
bugs
".
A useful tool for developers wanting to run models on their own code is
Chris Mason's kres; he
also suggested reading this
article by Willy Tarreau on how to use local models to find code bugs.
For managers, he said, the "Securing Open Source in the Age of AI" document from the OpenSSF should be required reading.
He concluded by saying that the flow of bug reports does not look like
it is slowing down in the near future; it is going to be "a rough
18 months
". But, when the dust settles, our code will be better than
it was before, and that is a good thing.
The video of this talk is available on YouTube.
[Thanks to the Linux Foundation, LWN's travel sponsor, for supporting my travel to this event.]
Last rites for Gentoo's Chromium package
Chromium, the open-source upstream project for Google's Chrome web browser, is the browser of choice for many Linux users. It has also gained a reputation as being difficult for Linux distributions to package and build: Chromium has a complex build system, the project bundles many of its dependencies, and it has frequent releases. All of that, plus user complaints, has led the maintainers of the Gentoo Chromium package to give up on trying to maintain the package.
Gentoo focuses on allowing users to build their own software from source
using the Portage
software-management tool. Gentoo packagers create ebuild files, which are text
files written in a Bash-like syntax that contain the information needed by
Portage to build the software. Users then build packages themselves using emerge, which is the
command-line interface for Portage. A
recent ebuild for Chromium illustrates the complexity of the package.
Gentoo does offer prebuilt binary packages for some software via its Binhost project. However, building from source gives users the flexibility to declare USE flags to set compile-time options or change a package's configuration. For example, a user may wish to specify which optional libraries are linked with a package, or whether to install the accompanying documentation. With Chromium in particular, a user might employ the -bundled-toolchain USE flag (which tells Portage not to use the bundled toolchain) in order to use their system's version of Clang to compile Chromium rather than the bundled version included by the upstream project. That is optional for Gentoo users on x86-64 systems, but -bundled-toolchain is required for users on other architectures, since Chromium's bundled toolchain is only shipped for x86-64.
It is worth noting that Chromium is currently not available as a binary package from Gentoo due to problems with building the package with proprietary codecs.
Last rites
Many distributions, including Arch Linux, Debian, and Fedora, use the term "orphan" to refer to packages that have been abandoned by their maintainer; the developer announces that a package has been orphaned, and other contributors have the opportunity to claim maintainership of it if they wish to do so. Gentoo's terminology is a bit more dramatic: a package maintainer announces "last rites" for a package on the gentoo-dev-announce mailing list to notify the project that it will be unmaintained, and as an opportunity to allow other developers to claim maintainership.
After a developer has declared last rites, the package's ebuild is masked in Gentoo's ebuild repository to ensure that users will not accidentally install a package that is no longer being maintained. Users who have the package installed and attempt an upgrade will receive a warning that it has been masked. Chromium package maintainer Sam James declared last rites for the Chromium package on September 24, after a lengthy conversation in a bug report filed by Roman Žilka.
On September 9, Žilka had complained that the latest stable version of the Chromium ebuild was outdated:
The latest stable www-client/chromium (and google-chrome and possibly others) is 151.0.7922.169, which contains a catastrophic 602 known vulnerabilities of all severities. Measures need to be taken by somebody qualified that this doesn't keep happening in packages as important as these.
He had attached an ebuild for a newer version of Chromium to the bug report, but noted that it would not work if a user tried to compile Chromium with the -bundled-toolchain USE flag.
James replied, "Chromium
is horrible to maintain as a source package. It is easily the package in Gentoo
that burns through maintainers the most.
" Complaining about its maintenance
isn't helpful, he said, and added that the maintainers have come close to
giving Chromium last rites several times over the years due to the difficulty in
keeping it up to date. He also noted that he had mentioned this to Žilka before,
and said that it would be welcome if he wanted to assist with the package.
Indeed, Žilka had filed a similar
bug in August complaining about the number of vulnerabilities present in the
Chromium ebuild; James had replied then that the package had always
been difficult to maintain, "and now they've added Go
" as a dependency as
well. Prior to that, Žilka had shown up in a bug report filed
by Matt Jolly about Chromium vulnerabilities to complain
that "the update process needs fixing, so that events like these don't happen
again in packages as critical as these!
"
Jolly had replied
that the maintainers are a team of volunteers who do their best, but "build
failures, human factors ('I messed up assigning the bug and automation didn't
pick it up'), and my own limited free time are the biggest causes of
delays
". The best way to change the situation, he said, would be for Žilka to
volunteer his help.
Trial and error
There are various third-party repositories, called overlays,
that provide additional and alternative ebuilds for Gentoo. On
September 11, Nick Reale said that he had tried ebuilds for
a newer version of Chromium from the Bentoo and Fireburn overlays, but he
couldn't get either one to work. A few days later he reported success with Bentoo's
ebuild and a specific set of USE flags. There was some follow-on discussion from
Reale and François Valenduc about various incantations they were able to use to
compile an updated version of Chromium on Gentoo from other ebuilds.
On September 18, Valenduc commented that version
153.0.8010.47 of Chromium was out, and that version was already available in
Arch Linux, openSUSE, SUSE, and Ubuntu. "We are still waiting for Gentoo
despite all the proposals made here.
"
James replied
that none of the maintainers have had a chance to look into
the problems with the Chromium package yet. He said that the patches and
ebuilds that had been submitted with the bug report were "useful and
appreciated, but it's not as simple as just grabbing it and committing
it
". Users would complain, he said, if the maintainers had not tested the
ebuilds and it broke on their systems.
It'll get done when it's done, but it's more likely to be last-rited if nobody is interested in handling it in the way these things have to be done (which goes beyond just attaching ebuilds).
Valenduc said that he was
not able to maintain the package, "but taking the ebuild from the bentoo
overlay was not that difficult [...] It's just frustrating to see no updates in
Gentoo.
" James replied that
just because the ebuild worked for Valenduc did not mean it had all USE flags
working. He added that no one had submitted a patch to the Gentoo ebuild, which
meant that the maintainers would need to reverse-engineer the changes by diffing
the ebuilds and work out what had been modified. "All of that is a
non-trivial amount of work and while having some ebuild to start with is useful
for that, it doesn't mean one can just git add && git commit &&
git push it.
" Valenduc acknowledged that he could not
test all possible USE flags, since it took between 15 and 16 hours to compile
Chromium on his laptop.
On September 24, Žilka commented: "This is
ridiculous
". A few minutes later, James replied "OK then
", and
issued the last rites for
the package.
Can we keep it?
Maciej S. Szmigiero asked if
it would be possible to keep the ebuild in Gentoo's repository and just declare
that it was maintained at "best effort" level. "Removing buildable/patchable
Chromium is a huge loss for a Gentoo desktop.
" James said that he did not think
that was possible. He had already explained that Chromium was being maintained by
volunteers, and that explanation had not been accepted.
People were free to maintain the ebuild in another repository, he said, but
that meant they would have to do the work themselves or accept someone doing it
to a lower standard. He pointed out that the ebuilds from the Bentoo overlay had
been cited in the discussion, but creation of those ebuilds seemed to be
"heavily automated
" and had missed some fixes in the Gentoo
version. "Copying ebuilds works fine until it doesn't.
"
James added that someone could still pick up the Chromium package before the
end of the last-rites period on October 24, or that the package could be
restored in the future. He did not want to see that, though, unless there was a
plan for sustainable maintenance. "Chromium has a history of burning out
maintainers in Gentoo because of the high rate of churn upstream, though some of
the contents of this bug don't help motivation at all either.
"
Matt Whitlock wondered if the developer-burnout factor could be reduced by eliminating most of the USE flags for Chromium, or if the maintainers stopped unbundling third-party libraries.
Basically, what I am asking is: can we give up _all_ of the flexibility to which we have grown accustomed in www-client/chromium, in exchange for a package that is actually maintainable but that is still built from sources by a toolchain that is not distributed as opaque binaries?
He added later that part of
the problem was that the upstream project developers "do not test
their builds with any of their allegedly 'optional' features disabled
". That
left the responsibility with the downstream package maintainers. "In the case
of Chromium, keeping all the toggle switches working (despite chronic neglect
from upstream) is a monumental, nigh-insurmountable task.
"
Complexity
That was a good question, James said, but part of the recent
complexity with Chromium was the addition of Rust and Go dependencies. The
packagers had to do some wrangling to ensure that the Go build did not require
network access, which is forbidden with Gentoo ebuilds, but that was not the
only problem. He said that Google developers seem to keep using experimental
Rust features that break on new releases as well. On top of that, "yet
another problem is that upstream's CI to produce release tarballs isn't
reliable
". One of the Gentoo Chromium maintainers had sent patches to fix
that, to little avail. "It took ages to get [the patches] reviewed, and it's
broken again a few times since. They didn't seem to notice or care that it
either wasn't producing tarballs or was producing incomplete ones
."
Jolly added some of his
observations about problems with maintaining Chromium for Gentoo. He said
that maintaining Chromium can take more than six hours each week, and that was
counting only compilation time on a fast PC with "an absurd amount of
RAM
". Compilation time is even longer for 64-bit Arm machines.
It's a commitment to volunteer at least a business day's worth of your free time each week when you include rebasing patches, cherry-picking fixes, iterating on `ebuild ... clean compile`, plus trying to identify and fix any new bugs, working out how much you violate Gentoo policy by not unbundling more of the browser, spending time on automation to save time and mistakes later, etc. There's immense pressure to keep builds up-to-date, especially in the age of hundreds of weekly browser CVEs.
He included a "pre-emptive FAQ
" in his reply about the last rites for
Chromium, and what it would require to restore the package. He said that there
were no insurmountable technical issues to maintaining Chromium, but it would
need multiple maintainers with a broad set of skills—including familiarity
with C, C++, Go, JavaScript, and Rust. "There are also a huge number of NIH
[not invented here] Google tools that you'll [have to] develop skills for and never be
able to use anywhere else - you have been warned
."
Using Google's toolchain would be simpler, but it would also restrict the
ebuild to x86-64, he said. "We'd lose arm64, ppc64, and the RISC-V overlay -
better to just rip the band-aid off now as it doesn't materially make the
situation better
". He added that he would be willing to review commits and offer
advice to anyone who wanted to maintain the source ebuild, but he felt that at
least three people would be needed. "History has shown that one maintainer
isn't working, and we've had the release cycle shorten twice since I started
maintaining the package in 2023; it was bad then, and it's worse now.
"
The release cadence for Chromium is aggressive, to say the least. Chromium has multiple channels including stable, beta, and development. There is a new major branch of the browser roughly every two weeks via the stable channel, and a new version is shipped every week.
Getting Chromium
For now, it appears that Gentoo users will need to search elsewhere for a suitable Chromium ebuild, choose a different browser, or find a different distribution method to acquire Chromium. For example, Gentoo users could install the Flatpak from Flathub, but it is an unverified package built by a third party—not by the Chromium upstream project. The Flatpak is also of no help for users who are not on x86-64 or 64-bit Arm systems.
It is technically possible for Chromium users to build and compile the browser on their own using the upstream's instructions, but it does not appear that the Chromium project cares a great deal about making that easy to do. It does have a page on getting the code but the links to instructions for Linux (as well as macOS and Windows) return a 503 error. Searching for instructions turns up this page, though it is undated so it is unclear if it is the most up-to-date. Assuming the instructions are current and correct, building Chromium using those directions is quite an ordeal. Users can download pre-built binaries from the project, but only for x86-64 systems.
Other distributions continue to supply Chromium packages, of course, though
their approach does not provide the same flexibility as Gentoo's. Fedora's
package
(which is described as "A WebKit (Blink) powered web browser that Google
doesn't want you to use
") is at version 154.0.8037.92—one version
behind the upstream (154.0.8037.97) release that was published on
October 1. Likewise, the package in Debian's security repository is the
same version (currently) as Fedora's and the information
page shows that there are at least 11 known CVEs addressed in
154.0.8037.97. Keeping up with Chromium is not an easy task.
Perhaps Gentoo will find a team that is willing and able to take on the burden of maintaining the Chromium ebuild up to the standards that Gentoo users expect. Whatever happens, it seems unlikely that Chromium will become any easier to maintain in the interim.
Beyond the &
Rust has a number of kinds of smart pointers, both in the standard library and defined by users. Still, some operations that are possible with built-in references are not possible to perform with user-defined smart pointers. Tyler Mandry, lead of the Rust project's language team, spoke at RustConf 2026 about the lengthy effort to change that, and make smart pointers just as flexible as built-in references.
He has been working on this problem all through 2026, Mandry said, alongside several other interested members of the language team, under the project name "Beyond the &". It took a good deal of thought, but the design that they have arrived at should allow a substantially simpler mental model of how pointers and references work. To illustrate the problem that this design solves, he put up an example of a simplified Rust program that calculates some dynamic content and caches it in a hash map. The example uses Rust's map-entry API, which provides a function called or_insert_with() that takes a callback to populate the hash-map entry if it is empty.
    struct RenderState {
        cache: HashMap<String, Arc<String>>,
        template: String,
    }

    fn render_page(state: &mut RenderState, name: &str) -> Arc<String> {
        // Mutably borrow `state.cache` using the Entry API.
        let entry = state.cache.entry(name.to_string());
        entry.or_insert_with(|| {
            // Create the entry if it doesn't exist.
            Arc::new(state.template.replace("$name", name))
        }).clone()
    }
This code looks up a cache key (name) in the hash map, and either returns a copy of the cached value, or calculates it by substituting name into a template if it doesn't exist. The shared state is accessed using a built-in mutable reference, &mut RenderState. The example works, but it can't safely be shared between threads. Adding a mutex, to allow the cache to be shared, causes the borrow checker to reject the program:
    fn render_page(state: &Mutex<RenderState>, name: &str) -> Arc<String> {
        let state: MutexGuard <' _ , RenderState> = state.lock().unwrap();

        // The borrow checker complains that "state" is mutably borrowed here:
        let entry = state.cache.entry(name.to_string());
        entry.or_insert_with(|| {
            // ... but then used here while it is still borrowed:
            Arc::new(state.template.replace("$name", name))
        }).clone()
    }
The original code worked, Mandry said, because the borrow checker was able to track that state.cache and state.template were separate fields, so it was safe to access them at the same time. With the addition of the mutex, the borrow checker just sees opaque accesses to a MutexGuard structure, and can no longer tell that the accesses are disjoint — it has to consider the case where the mutable borrow is used to edit the state at the same time that the callback reads from it, causing a potentially invalid data race. A simple fix in this case is to dereference the MutexGuard once, and reborrow the structure behind it:
let state: &mut RenderState = &mut *state.lock().unwrap();
This constructs a new built-in reference, just like the original code used, so the borrow checker can once again see that the accesses don't interfere with each other. That works, but it's not particularly intuitive. Mandry said that complexity like this contributes to Rust's difficult learning curve. It would be better if user-defined pointer types such as MutexGuard behaved more like built-in references.
Pointer types are everywhere, he continued. And all of them have slightly different semantics. Some pointers can't be safely dereferenced (raw pointers), or can be written to but not read from (MaybeUninit), etc. This demonstrates Rust's versatility, but it also makes it hard to come up with a design that works for the many possible pointer types.
The solution the language team settled on, based on the work of Nadrieril and Benno Lossin, was to expose the compiler's internal notion of a "place" to user code. A place is Rust's equivalent of C's left-hand sides (lvalues): a location that values can be read from or written to. The difference between a place and a pointer is that a place is an abstract expression that exists at compile time, such as state.cache, and a pointer is one way to represent a place at run time.
The idea is to create a new handle type for every smart pointer. Often the handle will simply be a wrapper around an unsafe pointer to the same location. Then, the compiler will automatically create handles to represent places referenced by the program. That allows user code to implement traits on a handle type that will affect how the borrow checker interacts with handles which correspond to a custom smart pointer, with a higher degree of flexibility than the existing Deref and DerefMut traits. As an example of what that would look like, Mandry showed how a library author might go about teaching the borrow checker how to handle writes to places that are accessed via a NonNull pointer:
    unsafe impl<T> WritePlace for NonNullHandle<T> {
        const SAFE: bool = false;
        unsafe fn write_place(self, value: T) {
            unsafe { self.0.write(value) }
        }
    }
The WritePlace trait would be used to tell the borrow checker that a particular kind of handle (in this case, a handle referencing a NonNull pointer) can be written to, and how. When SAFE is set to false, the borrow checker treats writing to the associated place as an unsafe operation. The actual write is forwarded through to the raw pointer that NonNull wraps. The whole trait implementation is unsafe because an incorrect implementation of the trait could cause the borrow checker to make a mistake and result in unsound behavior.
A corresponding ReadPlace trait encodes how to read from a handle. More interesting are ProjectPlace and BorrowPlace. The former tells the borrow checker how to turn a place containing a structure into a place containing one of its fields. For example, how to turn (the handle for) a MutexGuard<RenderState> into a MutexGuard<String> when the programmer writes state.template. The latter tells the borrow checker how to create a new smart pointer that borrows a given place, the same way that & works for built-in references.
The language team is still debating what the syntax for creating a new smart pointer with BorrowPlace should be. While it could use the same & symbol, that might be confusing and make it harder to use type inference. One proposal is to use an @ symbol instead, but people aren't entirely happy with that either. No matter what syntax is eventually decided on, the BorrowPlace trait encodes all of the information that the borrow checker needs to know in order to safely handle the pointer type. This means that currently built-in behavior can be defined via the same mechanism. For example, this is what an implementation for the built-in reference type &T would look like:
    unsafe impl<'a, T> BorrowPlace<&'a T> for RefHandle<'a, T> {
        // Tell the borrow checker that multiple references can be made to the
        // same place at the same time:
        const ACCESS: AccessKind = AccessKind::Shared;
        // And that the borrow lasts for the lifetime 'a:
        type Timing = Lifetime<'a>;
        // And that creating references is a safe operation:
        const SAFE: bool = true;

        unsafe fn borrow(self) -> &'a T {
            unsafe { &*self.ptr.as_ptr() }
        }
    }
That gives users an example of how to write their own smart pointers that act
like references, and gives the standard library maintainers a place to document
existing counterintuitive built-in behaviors.
With a similar implementation of a handle type for MutexGuard,
the earlier render_page() example
works without errors. Mandry called it "a small code change for this example,
but a big semantic shift.
"
Tying smart pointers more closely to the compiler's existing internals has other benefits, however. Currently, it is possible to use pattern matching on a value behind a reference, but not on a value behind a smart pointer — at least without dereferencing the pointer and reborrowing the value behind it. The details exposed by BorrowPlace would be enough to let the compiler safely implement those pattern matches.
One of the criteria that the language team looks for in new features is
composability, Mandry said: how well the prospective feature integrates into
the existing structures of the language, and how well multiple uses of the
feature compose with each other. Handles and places "compose beautifully
"
because it is just exposing some details of how the compiler already
understands and processes the language.
Despite that, exposing places and handles to library code is still a
prototype. Mandry asked for help ensuring that the design would work for
everyone's use cases; he asked the audience to look at
the design documentation and add their own examples of smart pointers with
weird semantics. "If you have an abstraction that you want to have more
deeply integrated into the language, please help us out by trying this, and
telling us about any roadblocks.
"
The next part of the design that he intends to flesh out is errors and
diagnostic messages. Ideally, users should never see errors mentioning the newly
added traits; those would remain internal, and the error messages would explain
the problem directly, as they do for built-in references. Even though there is
much more work to do before it can become a stable part of the language,
Mandry is optimistic about this design. "My hope is that it will let
libraries make Rust even more powerful and friendly.
"
One audience member wanted to know whether this design would also support destructive pattern matching (a combined operation that takes ownership of a value while matching it against possible patterns, pulling it apart into its component pieces). Mandry said that it would, as long as the developer implemented a VariantPlace trait for the appropriate handle. There are six to eight operations to implement to support every operation on a handle type, and that's one of them, he said.
Another audience member asked whether the
design would also work for enumerations in general. Mandry paused, stared out
into space for a moment, and then let out a hesitant and elongated yes.
Projecting a field from an enumeration in general will probably not be possible,
he elaborated, but there has been some exploratory work in that direction. For
example, should it be possible to project a field from inside an
Option
to obtain an Option of the field value? "I don't know the answer,
but it's an interesting question,
" Mandry remarked, just before time for the
session ran out.
[ Thanks to the Linux Foundation, LWN's travel sponsor, for assistance in traveling to Montreal for RustConf. ]
An update on the Sashiko patch-review system
Patch review has long been one of the limiting constraints for the kernel project (and most others); there just aren't enough people to properly review all of the code that is submitted for inclusion. The Sashiko system, which uses a large language model (LLM) to generate reviews automatically, offers the prospect of some relief, and has already become an important part of the kernel's development process. At the 2026 edition of Kernel Recipes, Roman Gushchin, the maintainer of Sashiko, provided an overview of how the system works and what is being done to improve it.The primary goal driving the development of Sashiko, he said, is preventing new bugs from entering the kernel. All of the code (excepting the LLM, of course) is open source and has been donated to the Linux Foundation. The main Sashiko instance runs on Google's Gemini LLM, but the code works with a number of popular models. It watches kernel mailing lists, and reviews all of the patches that it sees there. Those reviews show up in the central sashiko.dev site, which is sponsored by Google.
 There are a number of reasons to create a dedicated review harness for the
kernel, he said. Initially, this project started with a generic LLM, but
the quality of the reviews was not high enough. LLMs are highly dependent
on the context they are given. They need enough information, but not more;
providing too much information will lead to "
strange effects
".
Security is also a significant concern; maintainers rely on Sashiko to
judge code, and have to be confident that it has not been subverted. That
means, among other things, a fair amount of effort to protect the system
against prompt
injection. Efficiency is also a concern for a system that must be able
to review 1,500 or more patches every day.
The design principles behind Sashiko include "full transparency
";
everything is available. That includes the code, prompts,
thought chains, and generated reviews. Development is guided by benchmarks
that measure both the ability to detect problems and false positives. All
aspects of Sashiko are opt-in, he said, with developers able to control the
sending of email. The project aims for a "kernel-like development
culture
".
Sashiko is structured as a multi-stage pipeline; there are 11 stages now, with another one to be added soon. The first seven stages each review a patch from a different angle; one specializes in locking, another in resource control, one in security, and so on. Each stage produces "concerns" that are passed to the later stages, the eighth of which performs deduplication. Stage nine handles conflict resolution, stage ten performs validation and severity calibration, and the final stage generates the reports. It is important, he said, to separate discovery from verification. If the system is asked to only report bugs that it can absolutely prove to exist, it will miss a lot of problems; enumerating concerns then trying to falsify them afterward works better.
In its first six months, Sashiko has generated over 170,000 reviews across 91 mailing lists. That work has required over 18 million Git invocations to look up information. The early versions were slow; it turns out they were I/O bound due to all the checking of Git repositories. It took 15 hours to review a patch; now a review takes 15 to 30 minutes.
The benchmark works by taking 1,000 known regressions with known fixes; each patch that introduced a regression is re-reviewed without the fix, and an LLM scores the result. Currently Sashiko finds just over half of those bugs, all of which originally got past human review.
Evaluating the impact of Sashiko in the kernel community is difficult, he said; the system is still too new. It is also hard to measure; a lot of the bugs it finds are quietly fixed in subsequent patch postings. There are, he said, 1,215 commits in the kernel repository citing Sashiko, and its reviews have seen 6,600 email replies from 1,015 kernel developers. From this, he concludes that the system does, indeed, work. But whether it results in improved kernel code is harder to measure. He has spent some time looking at kernel commits fixing a patch that had been applied within the previous 60 days; it looks like there was less of that happening for 7.1, but it is too early to say for sure. But patches that were reported as "clean" by Sashiko had few fixes, while those with reported problems required more fixes.
A relatively new Sashiko feature is a local, terminal-based review mode. It can be installed with:
$ cargo install sashiko
After that, it's just a matter of configuring one's LLM key and running it in the terminal.
When Sashiko reviews a patch, it also tends to find existing bugs in the surrounding code. Developers have not always welcomed hearing about those bugs; fixing them is not part of what they set out to do. So now Sashiko is suppressing those reports and putting them into a separate database. There are about 5,000 bugs in that database now; anybody who is named in the MAINTAINERS file can query it to see the bugs that have been reported in their subsystems. One problem is that nobody has time to maintain this database and, for example, clear out entries for bugs that have been fixed; he is hoping to set up some agents to do that work.
Also new is "Sashiko for Sashiko", which reviews changes to Sashiko itself. Meanwhile, there is, evidently, somebody out there running a Sashiko instance to review OpenBSD patches; he does not know who that is, but would like to learn from their experience. In the future, Sashiko instances may be set up for projects like Git, LLVM, or QEMU. While many of the prompts used by Sashiko are kernel-specific, much of what is there is more general. He has also seen developers who are using Sashiko in their own workflow; Sashiko was meant for maintainers, but its use by developers is expanding as well.
There are, of course, always ways in which the tool can be improved. For example, reviews for large changes are notably worse than those for small ones. Developers can be frustrated by its tendency to keep finding new bugs in code it has reviewed before, even if the code itself has not changed. It still does not find all of the bugs, and it still makes up bugs that do not exist.
Gushchin concluded by saying that the Sashiko project could use more help; new contributors are welcome. Providing feedback on its reviews is perhaps the most important and helpful way to contribute. The development of subsystem-specific prompts is always welcome. Finally, there is always value in adapting Sashiko for other projects that might benefit from automated patch review.
A member of the audience (not me, surprisingly) remarked that many of the prompts appear to duplicate information that is in the kernel's documentation, and that some of the other information there would be useful to human developers as well. Perhaps, he suggested, the prompts should be a part of the kernel's documentation. Gushchin agreed in principle, but said that the situation is complicated. Sashiko is meant to work with older kernels as well as the current mainline, he said, and the prompts tend to change more quickly than the kernel's release cycle. Both of those points argue for keeping the prompts, or at least a subset of them, outside of the kernel.
Mark Brown remarked that, when Sashiko needs information from outside of the
kernel tree, the result is often "hot garbage
"; he wondered if that
situation could be improved. Architecture-specific code tends to be one
area where this behavior is seen. Gushchin suggested that giving the model
access to data sheets might help, though that may not always be legally
possible.
The video of this talk is available on YouTube.
[Thanks to the Linux Foundation, LWN's travel sponsor, for supporting my travel to this event.]
Analyzing Rust programs with Charon
Nadrieril is a long-time Rust contributor, and the maintainer of the rustc pattern-matching infrastructure. During his involvement with Rust, he has noticed a problem with the usability of the language: it is difficult to automatically extract information from a Rust crate for use with other tooling. The Charon project aims to fix that by providing a stable API for accessing internal information from the Rust compiler.
A lot of features in Rust are implicit or automatic, he explained, so it's hard to make a tool that interprets what Rust code does without reimplementing large parts of the Rust compiler (rustc). The normal way for tools to work around that is by using rustc's internal interfaces, but those interfaces can sometimes break without warning. The compiler binary is a thin wrapper around a library that can theoretically be linked to and used by other applications, but the entry points are explicitly documented to be unstable.
The aim of Charon is to "show you what rustc sees
" in a stable way,
centralizing all of the development work needed to keep up with changes in
rustc's internal interfaces.
Nadrieril thought that the Rust developers working on the kernel might have a
particular use for that when writing custom tooling that works as part of the
kernel build. To demonstrate exactly what Charon can do, Nadrieril had
a series of demos that started with
a tiny crate that "does basically nothing
". Running "charon
cargo" will compile a Rust project as cargo normally would, but with an
extra output: a .llbc file containing
JSON that has the complete contents of the crate in readable form. That includes
defined types, traits, and functions.
Charon can also pretty-print that JSON output for human readers. This output takes the form of a Rust-like language that marks the source of the program with additional comments and statements to show implicit features explicitly. For example, the output uses lightning bolt (⚡) symbols to show where control flow will go during stack unwinding. Even the output from the minimal example was a bit verbose, but it showed where values were dropped, the types of the variables involved, and even preserved comments from the source. The Rust function
fn consume(_: String) {}
becomes:
    // Full name: use_threads::consume
    fn consume(_1: String)
    {
        let _0: (); // return
        let _1: String; // arg #1

        storage_live(_0)
        _0 = ()
        _0 = ()
        conditional_drop[impl_Destruct_for_String::drop_glue<'0>] _1
        ↳⚡ unwind_continue
        return
    }
Nadrieril then went on to show how this kind of analysis can be useful for the kernel specifically. For one thing, Charon can be used to see how rustc has interpreted the output of bindgen, the program that generates Rust versions of the kernel's C structures. Charon's output shows both the specific layout that rustc chose, and which pieces of that layout are guaranteed to remain stable between compiler versions. As an example, he showed this piece of Charon's output for the kernel's list_head structure:
    // Full name: bindings::bindings_raw::list_head
    pub struct list_head {
      next: *mut list_head,
      prev: *mut list_head,
    }
    // layout:
    //     size: 16usize (guaranteed:
    //         at_least(align_to(max(size_of::<*mut list_head>(),
    //                               size_of::<*mut list_head>()),
    //                           max(align_of::<*mut list_head>(),
    //                               align_of::<*mut list_head>())))),
    //     align: 8usize (guaranteed:
    //         at_least(max(align_of::<*mut list_head>(),
    //                      align_of::<*mut list_head>()))),
    //     discriminator: _,
    //     inhabited: true,
    //     variants: [
    //         _: {
    //             offset of next: 0,
    //             offset of prev: 8,
    //             inhabited: true,
    //             tagger: [],
    //         },
    //     ],
    //     repr(C),
That information contains several redundant pieces, such as the variant information for a structure that is not an enumeration, and therefore only has one variant. The advantage is that the structure of the JSON Charon emits is extremely regular, which makes it easy to write simple tools that use it. Structures and enumerations always provide the same set of information. The same is true for functions, regardless of whether they are defined as closures, methods, or top-level functions. That makes code to iterate over the produced JSON simpler to write. For example, a custom linter that checks that a program does not call std::thread::spawn() comes to about 60 lines.
"If you've ever tried to look at rustc's ABI, you might be crying now. This
is not easy,
" Nadrieril said. Gary Guo asked how Charon compared to the
rustc_public project, which has a similar goal. The two projects are two ends
of a spectrum, Nadrieril replied. The rustc_public project does the minimum amount of
work necessary to expose rustc's interfaces, and also provides the minimum level of
abstraction. Charon does a certain amount of work to wrap the information that
rustc's interfaces provide in a nice,
simplified, easy-to-parse format, and to provide better tooling to work with
it. Guo agreed that Charon's approach was better.
Miguel Ojeda suggested that the Coccinelle for Rust project might want to use Charon in place of rust-analyzer. Nadrieril agreed that Charon would be a good fit for that use case. Kent Overstreet asked whether Charon could show what different optimization passes do to Rust code, which he thought would be useful for squeezing optimal performance out of the language without taking years to completely understand how the optimizations affect code generation. Nadrieril agreed that it would be useful, he just hadn't thought of that, so Charon doesn't do it yet. He didn't think it would be hard to add, however.
He had a few more demos of what is possible with Charon. One of them was to take a simple Rust function that performs 128-bit multiplication, and translate it to Python. That specific case is somewhat useless, because Python has native big integers, but it is sometimes useful to translate an algorithm from Rust to another language. For example, Charon exposes OCaml bindings that are generated by running Charon on its own source code. It has also been used to translate Rust into C or Lean.
Hindborg asked how good the Rust-to-C translation was. Nadrieril said that the tool only targets safe Rust, but within that domain it does pretty well, and generates legible C code. Microsoft has used it to translate some cryptography primitives implemented in Rust into C. Xong Fei Ding noted that BoringSSL had received a patch to convert libcrux from Rust to C and use it in place of BoringSSL's cryptographic code, but that it was rejected because the C version did not perform as well. Nadrieril said that there is a mismatch between which patterns are fast in Rust versus C, and that generating fast C code from Rust is much harder than generating readable C code.
Guo asked whether Charon based its output on the intermediate representation
that rustc constructs just after parsing the Rust code (medium-level
intermediate representation, abbreviated as MIR) or after it has
performed type checking and some optimizations (elaborated MIR). Charon can use
either — the former by default, and the latter when the user requests it with
the --precise-drops flag, since some optimizations can change where
drops occur, Nadrieril said. Guo explained that his interest came from having to
"hack around
" some of rustc's internals to make the
klint tool work.
After some back and forth, Guo concluded that Charon would not be able to
completely replace klint, but only because klint also checks some properties of
the generated binary.
Nadrieril concluded his presentation by saying that Charon has been in development for just over four years, and supports all Rust features except asynchronous code. There are still bugs, but other than the bugs, Charon produces correct output. The project will be ready for a 1.0 release soon. He requested that people try using Charon for their own use cases. The point of the project is to centralize the needed logic to interface with the compiler in one place; he would be pleased to see it adopted by all kinds of tools.
Evolving the LAVD scheduler from gaming to servers
The extensible scheduler class, which enables the creation of custom CPU schedulers with BPF, has led to a burst of innovation in this area; the LAVD scheduler has, perhaps, been one of the most noteworthy schedulers to emerge. Though it was originally designed for gaming applications, the LAVD scheduler has since grown to serve other types of workloads as well. At the 2026 edition of Kernel Recipes, Changwoo Min and Gavin Guo presented an overview of this scheduler and how it has evolved over time.
Games and criticality
Min started by saying that this scheduler was initially developed to address stuttering problems in games. Its core concept is urgency — which task most needs to be run next? It tries to infer the urgency of tasks automatically, then uses that calculation to adjust virtual deadlines. More recently, LAVD has grown more complex heuristics to determine which CPU a task should run on, and to minimize the number of active CPUs in the system.
 The project was started in 2023, initially aimed at SteamOS systems. Those
systems had been using the default completely fair scheduler, but there
were persistent complaints about latency spikes, which can ruin the gaming
experience. A fair amount of effort went into tuning the scheduler, but
there are no tuning knobs that solve the problem in any universal sense;
the tuning was highly workload-specific. But the underlying problem often
has the same roots. When looking at what was
happening in gaming applications, it was observed that the most common
system call was futex();
there is a lot of communication going on between the (many) threads in a
typical game. That communication is the key to a better scheduler design.
The Linux scheduler tries to optimize average performance but, Min said, that is the wrong target for games (and many other workloads); tail latency matters more. The initial objective was to improve tail latency on Steam Deck devices, which are relatively simple systems with a single CPU type. To do that, the developers focused on determining the urgency of tasks. Later on, LAVD has been adapted to deal with other CPU types (particularly non-heterogeneous systems with CPUs of varying capabilities) and, eventually, to be useful for data-center workloads. At last count, 42 developers had made over 900 commits to the scheduler, which is now about 12,000 lines of code.
Games are generally structured as processing chains, where task A completes some work and notifies B, which then does further work and passes it on to C. Delaying B will thus also delay C. Capturing this "who wakes whom" pattern is at the core of the LAVD design; that is done by maintaining three signals for each task: the wait frequency (how often it sleeps waiting for others), the wake frequency (how often it wakes other tasks), and the average run time. Tasks with shorter average run times, he said, are more vulnerable to delays in the scheduler. From those parameters, the "criticality" of a task is calculated; it is proportional to the product of the wait and wake frequencies divided by the average run time. Later versions of LAVD have added criticality inheritance; a task's urgency can propagate to both the tasks it is blocked on and those that are blocked on it.
Deadlines and CPU selection
Guo took over to discuss some details, starting with the calculation of deadlines for tasks. As with other schedulers, LAVD will run the task with the earliest deadline first. The key point here is that, for each task, the calculation of the time to the next deadline has a final step, where that time is divided by the task's criticality. So, if two tasks are initially assigned the same deadline, but one task is ten times more critical than the other, that task's deadline will be ten times closer. That insures that the most critical tasks will run ahead of the others.
 In determining time slices, the scheduler aims to run every task once
within a 10ms window, so the default slice is just 10ms multiplied by the
number of active CPUs, then divided by the number of running tasks. When
the time comes to preempt a task, LAVD looks at the CPUs running within the
incoming task's cache domain, and tries to pick the CPU running the
lowest-criticality task. There are some qualifiers, though. If the target
task is about to finish its time slice anyway, it will not be preempted.
Lock holders are also never preempted; the scheduler watches
futex() calls to keep a handle on tasks waiting for locks. There
are no inter-processor interrupts used to force immediate preemption;
instead, the target task's time slice is shortened so that it will
naturally yield the CPU at the next scheduling point.
LAVD maintains one dispatch queue per L3 cache domain, so each queue holds tasks that share a cache and will thus run those tasks where they may have cached data. But, Guo said, CPUs should not sit idle while other domains have work waiting to run, so a CPU that runs out of work to do may try to pull tasks from another domain. In general, LAVD's load balancing tries to balance work across CPUs. Rather than balancing by the number of tasks in the run queues, though, it tries to keep the same weight (amount of work being done) on each CPU.
There is more that goes into picking a CPU for a task to run on, though. Some CPUs are deemed to be "turbulent", meaning that it is harder to guarantee deadlines there. CPUs that are handling a lot of interrupts or which are running realtime tasks can fall into that category. LAVD, when placing a high-criticality task, will try to pick a "steady" CPU, avoiding the turbulent ones if possible.
A related question is when an idle CPU should be brought back up to run a task. Placing tasks on idle CPUs is good for work conservation (maximizing the amount of throughput a system can create) but it can also create poor cache behavior, hurting performance. LAVD tracks the amount of time a task has been running on a given CPU, and uses that to calculate a cache "warmness" value; that value decays when the task is out of the CPU. The warmness is used to decide whether the benefit of moving a task to a new CPU outweighs the cost.
Task spreading
Min returned to discuss a related topic: how many CPUs should the scheduler keep busy at any given time? Spreading tasks maximally to use all CPUs can actually hurt performance; cores that are not heavily used will sit in low-power states, and often move between power states as tasks come and go, resulting in the unfortunate combination of low performance and high power consumption. It is better, he said, to use fewer CPUs and let the rest of them sleep.
To that end, LAVD analyzes the data in the kernel's energy model (which describes how much work each CPU can do at each of its supported power levels) on startup and builds a table indicating which CPUs should be used at each level of load. When the system is running, the scheduler just has to calculate the total utilization and use that to look up which CPUs it should be placing tasks on. One other heuristic is to calculate the "performance criticality" of each task, which is a function of its latency criticality and overall CPU use. Tasks with a high performance criticality are preferentially placed on the larger (faster) CPUs.
Finally, there is ongoing work to integrate LAVD with control groups to allow the system administrator to place limits on CPU usage. There is a new library (called scx_cgroup) that provides control-group support for custom schedulers. The goal is to make this enforcement cheap, so the model chosen is "eventual enforcement"; no group is throttled during a single enforcement period. Instead, the objective is to make the averages balance out over the longer term. Among other things, that allows the relatively expensive usage accounting to happen outside of the critical scheduler paths.
In closing, Min said that the LAVD scheduler has evolved from its original use case for gaming into supporting workloads on server fleets; Meta is exploring its use internally. For the future, there is interest in better supporting AI workloads, which are often more concerned about GPU scheduling than CPU scheduling. In the meantime, though, LAVD has proved to be useful in a number of situations; its core critical-path heuristic was never specific to gaming.
An audience member asked whether any of the ideas developed in LAVD would eventually be contributed back to the kernel's EEVDF scheduler; Min answered that those ideas are still being stabilized, but that an attempt will eventually be made to upstream some of them.
The video of this talk is available on YouTube.
[Thanks to the Linux Foundation, LWN's travel sponsor, for supporting my travel to this event.]
Python's two modules for random numbers
Python's random and secrets modules both include utilities for obtaining random values, but only one of them is suitable for generating passwords and security tokens. For much of Python's history, random was used for passwords and tokens anyway, despite documentation that called it unsuitable for cryptography. In 2015, Python's core team debated whether to fix that misuse by making random secure by default. Instead, in 2016, Python 3.6 added a second module: secrets. The random module is still misused at times, so it is instructive to look into how the random-number modules should be used.
random is predictable on purpose
Python's random module provides low-level functions, like random(), which generates a random float between 0.0 (inclusive) and 1.0 (exclusive). It also provides much more commonly used high-level functions, including randint() for generating a random integer and choice() for selecting a random item from a sequence.
The random module is not designed for cryptographically secure randomness. It generates pseudorandom numbers using the Mersenne Twister algorithm, which it adopted in Python 2.3, and its API has changed little since then.
A random seed is used by the random module to generate its numbers. After the seed is set, each call to one of the module's functions consumes one or more numbers from that seeded state, which is an array of 624 32-bit numbers. After all 624 numbers have been used, the next 624 numbers are computed from the previous state.
Speed and reproducibility are the hallmarks of the design of the random module. Computing numbers with the Mersenne Twister is much faster than asking the operating system for each new random number. The random.seed() function sets the Mersenne Twister to a specific state, ensuring that subsequent calls to functions in the random module will produce predictable outputs. Automated tests often rely on this reproducibility, since testing is easier with deterministic output.
For example, this test_roll_die() function calls random.seed():
    import random

    def roll_die(rolls):
        return [random.randint(1, 6) for _ in range(rolls)]

    def test_roll_die():
        random.seed(0)
        assert roll_die(10) == [4, 4, 1, 3, 5, 4, 4, 3, 4, 3]
The roll_die() function call in test_roll_die() will always produce the same output because that seed() call pinned Python's Mersenne Twister to a specific state.
Predictability is at odds with security
Until Python 2.4, Python used the system clock to generate the random module's initial seed if none was specified. If an attacker could guess the moment that the seeding was done, they would know all subsequent random numbers generated within that Python process. For Python 2.4, the default initial seed was instead generated from 16 bytes read from the operating system's random-number generator (via os.urandom()). The clock time was used for the random seed only on operating systems that don't provide their own random-number generator.
That release also added the random module's SystemRandom class, which included utilities for obtaining unpredictable randomness from the operating system.
The 2.4 documentation described os.urandom() as "suitable for cryptographic use
", but its description of SystemRandom said nothing about security, noting only that its sequences were not reproducible.
By Python 3.5, OS-generated random numbers were used for the full 2,496 bytes needed to fill the Mersenne Twister's 624 slots. The random module's initial seed is much more secure than it used to be, except in the rare case that the current time and process identifier fallback kicks in.
Even with a secure initial seed, if an attacker was able to observe 624 consecutive random 32-bit outputs generated by Python's random module, they could reconstruct the Mersenne Twister's state and compute all past and future generated values. The high-level random module functions, such as randint() and choice(), return only part of the Mersenne Twister's output bits, so reconstructing the state takes more output and more computation. But this extra difficulty does not make them unpredictable.
The module's documentation has called its generator "completely unsuitable for cryptographic purposes
" since at least Python 2.2.
But the documentation did not point readers to SystemRandom for
security purposes until Python 3.3.3 in late 2013.
Should the default be secure?
In September 2015, Guido van Rossum, Python's benevolent dictator for life (BDFL) at the time, started a discussion about how people were using the random module for cryptographic purposes when they shouldn't be.
That discussion was inspired by several emails from OpenBSD founder Theo de Raadt, and was covered by LWN at the time.
Van Rossum acknowledged the documentation's warning against using the module for security, but noted that "nobody reads the docs
".
Six days later, Alyssa Coghlan authored PEP 504 ("Using the System RNG
by default"), proposing that the random module default to using
the random.SystemRandom generator class instead of the default random.Random
generator class.
Under that proposal, a Python user who specifically desired the deterministic behavior of the Mersenne Twister could call random.seed() to switch back to using a random.Random instance.
Van Rossum did not want the random module's default behavior to change, stating "MT [Mersenne Twister] is also over an order of magnitude faster than os.urandom() or SystemRandom
".
In that first message, he noted that "we already have random.SystemRandom()
", so he saw no reason to hurry to a solution.
Shortly after PEP 504 was introduced, Steven D'Aprano wrote PEP 506 ("Adding A Secrets Module To The Standard Library"), which proposed adding a new module for cryptographic-strength random numbers to Python. Coghlan (using her former name) withdrew PEP 504 in favor of PEP 506, which was accepted for inclusion into Python 3.6.
secrets: the secure random module
Python's secrets module provides choice() for selecting a random item from a sequence, randbelow() for generating a random integer below a given number, and randbits() for generating an integer with a given number of bits (an analogue of random.getrandbits()). It also provides functions for generating random tokens and performing equality comparisons that are safe from timing attacks.
Unlike the random module, secrets does not use the Mersenne Twister to generate pseudorandom numbers. Every function in the secrets module generates randomness solely from the operating system's random-number generator, which is continually reseeded with bits sampled from unpredictable events, like hardware-interrupt timing.
However, the secrets module has two main drawbacks when compared to random: there is no way to force reproducibility for automated tests, and the functions in secrets are slower than their random counterparts. The secrets module produces unpredictable numbers by design, so a loss of reproducibility is a necessary cost.
I generated ten million random numbers from zero to 99 using both random and secrets on my machine, running Python 3.15.0rc2. Using random.randint(0, 99) produced over five million numbers per second while secrets.randbelow(100) produced fewer than one million numbers per second, making secrets.randbelow() nearly seven times slower:
    >>> from timeit import timeit
    >>> n = 10**7
    >>> for statement, setup in [
    ...     ("random.randint(0, 99)", "import random"),
    ...     ("secrets.randbelow(100)", "import secrets"),
    ... ]:
    ...     seconds = timeit(statement, setup, number=n)
    ...     print(f"{statement}: {n / seconds:,.0f} per second")
    random.randint(0, 99): 5,866,763 per second
    secrets.randbelow(100): 891,087 per second
The speed difference between secrets functions and random ones is measurable, but probably negligible for most applications. Code that requires secure randomness rarely needs many random numbers at a time, but it definitely needs them to be unpredictable.
The secrets module has a smaller API
The secrets module is not a drop-in replacement for the random module, which includes choices(), sample(), shuffle(), and various other functions that the secrets module lacks. Python users cannot use those other random functions if they need unpredictable randomness, at least not directly from the random module. Instead, they can use the SystemRandom class, which both the random and secrets modules provide.
All of the top-level functions in Python's random module are implemented as methods on a specific instance of the random.Random class:
    >>> import random
    >>> random.choice
    <bound method Random.choice of <random.Random object at 0x25c2e9f0>>
    >>> random.seed
    <bound method Random.seed of <random.Random object at 0x25c2e9f0>>
    >>> random.choice.__self__ is random._inst  # private implementation detail
    True
The random._inst object is the default instance of random.Random that all random module functions are bound to. This allows one random.seed() call to affect the output of every module-level function call after it. The secrets module's choice() function is implemented in a similar way:
    >>> import secrets
    >>> secrets.choice
    <bound method Random.choice of <random.SystemRandom object at 0x25c3ac20>>
    >>> secrets.choice.__self__ is secrets._sysrand  # private implementation detail
    True
But while the random module binds these names to methods on a random.Random class instance, the secrets module binds them to a random.SystemRandom instance. The SystemRandom class inherits from random.Random, providing the same API, but all of its methods rely on os.urandom(). So, by making an instance of SystemRandom, Python users can still generate unpredictable randomness using random utilities that the secrets module does not provide:
    >>> import secrets
    >>> system_random = secrets.SystemRandom()
    >>> system_random.sample(range(100), k=5)
    [90, 64, 94, 74, 36]
secrets is for secrets and random for the rest
Today, the random module's documentation shows a warning that points those wanting random numbers for security and cryptographic purposes at its sibling, the secrets module. But the utilities in Python's random module are still occasionally misused for cryptographic purposes, as demonstrated by an advisory from the urwid project earlier this year. That kind of misuse is what the secrets module was meant to reduce, but unpredictable randomness has been available in the standard library since Python 2.4 using SystemRandom. The secrets module mostly just added an easier-to-discover API. Coghlan explained the reasoning in a 2015 email:
I see the core goal here as being to help guide folks towards using the right random number generator [RNG] for security sensitive tasks, and "use the RNG in the secrets module for random secrets, and the RNG in the random module for modelling and simulation" is a much easier story to tell than explaining the technical differences between random.Random and random.SystemRandom.
Even if a random-number generator that is fast, reproducible, and secure were possible, the Python core team did not want to change the existing random API by switching away from Mersenne Twister. So Python has two modules for generating randomness: secrets is for random secrets and random is for everything else.
Brief items
Security
OpenSSH 10.6 released
Version 10.6 of OpenSSH has been released. The announcement notes that the OpenSSH team has been receiving a large number of AI-assisted security bug reports. "We very much welcome these reports, especially when combined with human triage, analysis, test-cases and particularly when accompanied by proposed fixes". As a result, the project expects to be making more frequent releases to get updates to users more quickly rather than batching the bug fixes until the next planned release.
Notable changes in this release include enabling the hybrid post-quantum ssh-mldsa44-ed25519 signature algorithm, addition of a -p option for sftp's lmkdir/mkdir commands, as well as disabling the LZ77 dictionary coder in ssh and sshd to mitigate side-channel leaks (which will result in reduced effectiveness of the Compression option). The scp -R option, which allows copies between two remote hosts, is being deprecated due to security risks; the option will be ignored in the future. See the announcement for full details of all changes and bug fixes.
Security quote of the week
Closing the bug bounty program because it found too many vulnerabilities is not a particularly pleasant result.— Michael Catanzaro
Kernel development
Kernel release status
The current development kernel is 7.3-rc6, released on October 4. Linus said:
Next week might look a bit different: we've got the annual maintainer summit and the Linux plumbers conference going on , so I'll be on the road, as will a number of other maintainers. That may or may not end up changing the stats for -rc7. But it's unlikely to affect the release schedule, although the fact that I have my yearly family vacation the week after that might make the next merge window a bit wonky.
This release has seen 18,168 non-merge changesets from 2,926 developers, 764 of whom were first-time kernel contributors. The release history looks like:
RC Date Commits v7.3-rc1 2026-08-30 16267 16267 v7.3-rc2 2026-09-06 681 681 v7.3-rc3 2026-09-13 733 733 v7.3-rc4 2026-09-20 598 598 v7.3-rc5 2026-09-27 649 649 v7.3-rc6 2026-10-04 596 596
See the LWN KSDB v7.3 page for a lot more details.
Stable updates: 7.2.9, 6.18.55, 6.12.112, 6.6.158, 6.1.189, 5.15.222, and 5.10.271 were released on October 3.
Linux Test Project suite stable release for September 2026
The Linux Test Project has announced its latest stable release for September 2026. There have been 382 patches from 41 authors since the May 2026 release. See the announcement for a list of new tests, changes, and more.
Distributions
A new Raspberry Pi Desktop release is finally available for x86-64
Simon Long has announced a long-awaited release of Raspberry Pi OS, based on Debian 13 ("trixie"), for x86-64 systems.
We managed to find the time to update the Desktop for the Buster and Bullseye releases of Debian, but then we all just got too busy with other things, and, while we left the Bullseye version on the website for anyone who wanted it, we simply didn't have time to release any newer versions. But people kept on asking for it – we get two or three emails every week asking when the PC Desktop will be updated, and we haven't had an answer, because we honestly didn't know when we might get a chance to do it. We've continually tried to allocate time to be able to work on this, but it hasn't been easy. [...]
Earlier this year, we (or rather Serge) finally got the latest version of the Desktop running on top of a Debian Trixie image. It's now based on 64-bit Debian (the amd64 architecture) rather than the older 32-bit version, as Debian itself has stopped supporting 32-bit for PC architectures. This shouldn't be a major problem – most PCs made in the last 15 years or so will quite happily run the 64-bit version of Debian, as will most Intel-based Macs. (Debian support for Apple Silicon is still experimental, so unfortunately those of you with the latest and greatest shiny fruit products will not be able to run this.)
Development
RustConf recordings
The Rust Foundation has posted the recordings from RustConf 2026 in Montreal, Canada. Photos of the event are also available. LWN covered four talks from RustConf this year.
Rust 1.99.0 released
Version 1.99.0 of the Rust language has been released. Changes this time include support for extern "C" variadic functions, the establishment of functions for obtaining the size and alignment of raw pointers, a number of stabilized APIs, and more.Picard 3.0 released
Version
3.0 of the MusicBrainz Picard
tag editor has been released. "This release brings many changes, including an
upgrade to Qt6, a completely new plugin system, several improvements to the user
interface, cover art processing, [International Standard Recording
Code (ISRC)] submission and many more.
"
LWN covered Picard in April.
Zig 0.17 released
Version 0.17 of the Zig programming language has been released.
This release features 5 months of work: changes from 206 different contributors, spread among 925 commits.
Originally predicted to be shorter, this release cycle ended up [being] substantial, with the Build System reworked, including the introduction of the Build Server Protocol, and the ELF Linker enhanced to the point where we expect Incremental Compilation to work for everyone on x86_64-linux.
LWN last covered Zig in December 2025.
Development quotes of the week
It's fine to leave a community because it's not aligned with your strategic outlook or your values, or simply because the community moved on. You joined a community because you were aligned to it, and you can leave when that ceases to be the case. The project is the ship of Theseus, and we are all the rotten planks getting replaced over time.— Emmanuele Bassi
— Luciano MamminoI started with what felt like a fairly mundane question: "how does Docker delete a file?". The answer turned out to involve magic file names, opaque directories, an entire reserved namespace of file names, and a Docker image that changes its filesystem after being exported and imported again. Not bad for one innocent question!
If I had to condense everything into a mental model, it would be this: layers aren't miniature filesystems. They are ordered filesystem changesets. The filesystem a container sees is what you get after interpreting all those changesets, in order, following the OCI [Open Container Initiative] rules. Additions and modifications are plain tar entries, deletions are whiteouts, and that convention means that a regular file whose name starts with .wh. can't survive the round trip through an OCI image.
I still think tar was a brilliant choice. It's simple, boring, ubiquitous technology, and boring technology tends to survive. Whiteouts are the little bit of protocol glue needed to stretch it beyond what tar knows how to express on its own.
Page editor: Daroc Alden
Announcements
Newsletters
Distributions and system administration
Development
Meeting minutes
Miscellaneous
Calls for Presentations
CFP Deadlines: October 8, 2026 to December 7, 2026
The following listing of CFP deadlines is taken from the LWN.net CFP Calendar.
| Deadline | Event Dates | Event | Location |
|---|---|---|---|
| October 9 | November 20 November 21 |
OLF Conference | Columbus, Ohio, US |
| October 26 | December 1 December 3 |
Yocto Project Virtual Summit 2026.12 | Online, Online |
| November 1 | April 1 April 4 |
Southern California Linux Expo | Pasadena, CA, US |
| November 2 | February 23 | AlpOSS 2027 | Echirolles (Grenoble), France |
If the CFP deadline for your event does not appear here, please tell us about it.
Upcoming Events
Events: October 8, 2026 to December 7, 2026
The following event listing is taken from the LWN.net Calendar.
| Date(s) | Event | Location |
|---|---|---|
| October 7 October 9 |
Open Source Summit Europe | Prague, Czech Republic |
| October 7 October 9 |
Embedded Linux Conference Europe | Prague, Czech Republic |
| October 8 | Linux Security Summit Europe | Prague, Czechia |
| October 10 October 11 |
GStreamer Conference 2026 | Prague, Czech Republic |
| October 13 October 15 |
OpenSSL Conference | Prague, Czech Republic |
| October 14 October 17 |
PyCon South Africa | Cape Town, South Africa |
| October 16 October 18 |
VideoLAN Developers' Days | Rome, Italy |
| October 18 October 20 |
All Things Open | Raleigh, NC, US |
| October 20 October 23 |
The Matrix Conference | Malmö, Sweden |
| October 20 October 23 |
PostgreSQL Conference Europe | Valencia, Spain |
| October 30 November 1 |
Qubes OS Summit | Berlin, Germany |
| November 3 November 4 |
Open vSwitch and OVN 2026 Fall Conference | Heilbronn, Germany |
| November 6 November 7 |
Texas Linux Festival | Austin, TX, US |
| November 7 November 8 |
OpenFest 2026 | Sofia, Bulgaria |
| November 7 November 8 |
OpenALT | Brno, Czechia |
| November 12 November 13 |
Ubuntu Summit 26.10 | Online |
| November 12 November 13 |
KVM Forum | Vancouver, Canada |
| November 14 November 15 |
Capitole du Libre 2026 | Toulouse, France |
| November 17 November 19 |
Open Source Monitoring Conference | Nuremberg, Germany |
| November 20 November 21 |
OLF Conference | Columbus, Ohio, US |
| November 21 | LocHal Open Source Event 2026 | Tilburg, Netherlands |
| November 28 | FOSS for All Conference 2026 | Seoul, South Korea |
| December 1 December 3 |
Yocto Project Virtual Summit 2026.12 | Online, Online |
If your event does not appear here, please tell us about it.
Security updates
Alert summary October 1, 2026 to October 7, 2026
| Dist. | ID | Release | Package | Date |
|---|---|---|---|---|
| AlmaLinux | ALSA-2026:75577 | 10 | bind | 2026-10-06 |
| AlmaLinux | ALSA-2026:67872 | 10 | corosync | 2026-09-30 |
| AlmaLinux | ALSA-2026:73765 | 10 | dogtag-pki | 2026-10-01 |
| AlmaLinux | ALSA-2026:76763 | 8 | dovecot | 2026-10-07 |
| AlmaLinux | ALSA-2026:74001 | 10 | expat | 2026-10-01 |
| AlmaLinux | ALSA-2026:72663 | 9 | expat | 2026-10-01 |
| AlmaLinux | ALSA-2026:73979 | 10 | freerdp | 2026-10-01 |
| AlmaLinux | ALSA-2026:76747 | 8 | freerdp | 2026-10-07 |
| AlmaLinux | ALSA-2026:73429 | 10 | gawk | 2026-09-30 |
| AlmaLinux | ALSA-2026:73511 | 8 | gawk | 2026-10-01 |
| AlmaLinux | ALSA-2026:73512 | 9 | gawk | 2026-09-30 |
| AlmaLinux | ALSA-2026:75680 | 8 | gd | 2026-10-06 |
| AlmaLinux | ALSA-2026:73427 | 10 | gdb | 2026-09-30 |
| AlmaLinux | ALSA-2026:73425 | 8 | gdb | 2026-10-01 |
| AlmaLinux | ALSA-2026:73426 | 9 | gdb | 2026-09-30 |
| AlmaLinux | ALSA-2026:74464 | 10 | ghostscript | 2026-10-02 |
| AlmaLinux | ALSA-2026:74457 | 9 | ghostscript | 2026-10-05 |
| AlmaLinux | ALSA-2026:75575 | 9 | gimp | 2026-10-06 |
| AlmaLinux | ALSA-2026:73998 | 10 | gvfs | 2026-10-01 |
| AlmaLinux | ALSA-2026:73997 | 8 | gvfs | 2026-10-01 |
| AlmaLinux | ALSA-2026:74370 | 9 | gvfs | 2026-10-01 |
| AlmaLinux | ALSA-2026:71233 | 10 | kernel | 2026-10-05 |
| AlmaLinux | ALSA-2026:70498 | 10 | kernel | 2026-10-05 |
| AlmaLinux | ALSA-2026:72624 | 10 | kernel | 2026-10-05 |
| AlmaLinux | ALSA-2026:71602 | 10 | kernel | 2026-10-05 |
| AlmaLinux | ALSA-2026:74133 | 8 | kernel | 2026-10-01 |
| AlmaLinux | ALSA-2026:75747 | 8 | kernel | 2026-10-06 |
| AlmaLinux | ALSA-2026:72623 | 9 | kernel | 2026-10-01 |
| AlmaLinux | ALSA-2026:74438 | 9 | kernel | 2026-10-06 |
| AlmaLinux | ALSA-2026:74132 | 8 | kernel-rt | 2026-10-01 |
| AlmaLinux | ALSA-2026:75746 | 8 | kernel-rt | 2026-10-06 |
| AlmaLinux | ALSA-2026:74442 | 10 | libpcap | 2026-10-01 |
| AlmaLinux | ALSA-2026:76045 | 8 | libpcap | 2026-10-06 |
| AlmaLinux | ALSA-2026:75582 | 8 | librabbitmq | 2026-10-06 |
| AlmaLinux | ALSA-2026:74424 | 9 | libvirt | 2026-10-05 |
| AlmaLinux | ALSA-2026:75674 | 8 | mariadb-connector-c | 2026-10-06 |
| AlmaLinux | ALSA-2026:75673 | 9 | mariadb-connector-c | 2026-10-06 |
| AlmaLinux | ALSA-2026:75581 | 10 | mod_auth_openidc | 2026-10-06 |
| AlmaLinux | ALSA-2026:75864 | 10 | nodejs22 | 2026-10-06 |
| AlmaLinux | ALSA-2026:73428 | 10 | nodejs24 | 2026-09-30 |
| AlmaLinux | ALSA-2026:75870 | 8 | nodejs:22 | 2026-10-07 |
| AlmaLinux | ALSA-2026:73954 | 10 | openssh | 2026-10-01 |
| AlmaLinux | ALSA-2026:66432 | 10 | osbuild-composer | 2026-10-05 |
| AlmaLinux | ALSA-2026:69293 | 9 | osbuild-composer | 2026-10-05 |
| AlmaLinux | ALSA-2026:73766 | 9 | pki-core | 2026-10-01 |
| AlmaLinux | ALSA-2026:74095 | 8 | rsync | 2026-10-01 |
| AlmaLinux | ALSA-2026:73519 | 8 | ruby:2.5 | 2026-10-06 |
| AlmaLinux | ALSA-2026:75579 | 10 | sudo | 2026-10-06 |
| AlmaLinux | ALSA-2026:75580 | 8 | sudo | 2026-10-06 |
| AlmaLinux | ALSA-2026:75571 | 9 | sudo | 2026-10-06 |
| AlmaLinux | ALSA-2026:73130 | 10 | thunderbird | 2026-09-30 |
| AlmaLinux | ALSA-2026:73971 | 8 | thunderbird | 2026-10-01 |
| AlmaLinux | ALSA-2026:75769 | 10 | vim | 2026-10-06 |
| AlmaLinux | ALSA-2026:74084 | 8 | webkit2gtk3 | 2026-10-01 |
| Debian | DLA-4811-1 | LTS | chromium | 2026-10-02 |
| Debian | DSA-6535-1 | stable | chromium | 2026-10-01 |
| Debian | DLA-4807-1 | LTS | expat | 2026-10-01 |
| Debian | DLA-4814-1 | LTS | firefox-esr | 2026-10-02 |
| Debian | DSA-6533-1 | stable | firefox-esr | 2026-09-30 |
| Debian | DLA-4815-1 | LTS | freecad | 2026-10-03 |
| Debian | DLA-4812-1 | LTS | libio-compress-perl | 2026-10-02 |
| Debian | DLA-4821-2 | LTS | libmodule-cpants-analyse-perl | 2026-10-06 |
| Debian | DLA-4824-1 | LTS | libpng1.6 | 2026-10-06 |
| Debian | DSA-6537-1 | stable | libpng1.6 | 2026-10-01 |
| Debian | DSA-6543-1 | stable | libreoffice | 2026-10-05 |
| Debian | DLA-4804-1 | LTS | libsmpp34 | 2026-09-30 |
| Debian | DLA-4817-1 | LTS | linux-6.12 | 2026-10-04 |
| Debian | DLA-4805-1 | LTS | mkvtoolnix | 2026-09-30 |
| Debian | DLA-4808-1 | LTS | network-manager-l2tp | 2026-10-01 |
| Debian | DLA-4820-1 | LTS | node-lodash | 2026-10-05 |
| Debian | DSA-6548-1 | stable | node-shell-quote | 2026-10-06 |
| Debian | DLA-4809-1 | LTS | nodejs | 2026-10-01 |
| Debian | DLA-4813-1 | LTS | open-iscsi | 2026-10-02 |
| Debian | DLA-4816-1 | LTS | pcre2 | 2026-10-03 |
| Debian | DLA-4821-1 | LTS | perl | 2026-10-05 |
| Debian | DLA-4806-1 | LTS | pgextwlist | 2026-09-30 |
| Debian | DLA-4819-1 | LTS | php8.2 | 2026-10-05 |
| Debian | DLA-4826-1 | LTS | puma | 2026-10-07 |
| Debian | DLA-4802-1 | LTS | python-django | 2026-09-30 |
| Debian | DSA-6546-1 | stable | rails | 2026-10-06 |
| Debian | DSA-6538-1 | stable | redis | 2026-10-02 |
| Debian | DLA-4823-1 | LTS | roundcube | 2026-10-05 |
| Debian | DSA-6545-1 | stable | roundcube | 2026-10-06 |
| Debian | DSA-6547-1 | stable | ruby-jwt | 2026-10-06 |
| Debian | DLA-4822-1 | LTS | ruby-oauth2 | 2026-10-05 |
| Debian | DLA-4803-1 | LTS | ruby-oj | 2026-09-30 |
| Debian | DSA-6542-1 | stable | ruby-rack-session | 2026-10-04 |
| Debian | DSA-6544-1 | stable | sabnzbdplus | 2026-10-05 |
| Debian | DLA-4825-1 | LTS | suricata-update | 2026-10-06 |
| Debian | DLA-4810-1 | LTS | thunderbird | 2026-10-02 |
| Debian | DSA-6536-1 | stable | thunderbird | 2026-10-01 |
| Debian | DSA-6532-1 | stable | tor | 2026-09-30 |
| Debian | DSA-6534-1 | stable | webkit2gtk | 2026-10-01 |
| Debian | DSA-6541-1 | stable | wireshark | 2026-10-04 |
| Debian | DLA-4818-1 | LTS | xen | 2026-10-04 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | 0install | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | alt-ergo | 2026-10-06 |
| Fedora | FEDORA-2026-b38ba933a5 | F43 | apptainer | 2026-10-01 |
| Fedora | FEDORA-2026-e84de41d80 | F44 | apptainer | 2026-10-01 |
| Fedora | FEDORA-2026-e4b8799ad3 | F45 | apptainer | 2026-10-01 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | apron | 2026-10-06 |
| Fedora | FEDORA-2026-2d7847f75c | F43 | assimp | 2026-10-04 |
| Fedora | FEDORA-2026-492ca43634 | F44 | assimp | 2026-10-04 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | brltty | 2026-10-06 |
| Fedora | FEDORA-2026-1a5c7b6f1f | F45 | budgie-control-center | 2026-10-04 |
| Fedora | FEDORA-2026-1a5c7b6f1f | F45 | budgie-desktop | 2026-10-04 |
| Fedora | FEDORA-2026-1a5c7b6f1f | F45 | budgie-desktop-services | 2026-10-04 |
| Fedora | FEDORA-2026-1a5c7b6f1f | F45 | budgie-desktop-view | 2026-10-04 |
| Fedora | FEDORA-2026-cd4e714c4e | F43 | chromium | 2026-10-06 |
| Fedora | FEDORA-2026-35b989661c | F44 | chromium | 2026-10-05 |
| Fedora | FEDORA-2026-0daef29dc3 | F45 | chromium | 2026-10-05 |
| Fedora | FEDORA-2026-53c8aca50a | F45 | chromium | 2026-10-06 |
| Fedora | FEDORA-2026-58726b29bc | F45 | ckermit | 2026-10-01 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | coccinelle | 2026-10-06 |
| Fedora | FEDORA-2026-61b2a3477a | F44 | cockpit | 2026-10-07 |
| Fedora | FEDORA-2026-0025579bc9 | F43 | cri-o1.36 | 2026-10-05 |
| Fedora | FEDORA-2026-f5c88f763a | F44 | cri-o1.36 | 2026-10-05 |
| Fedora | FEDORA-2026-77abfa2cdd | F45 | cri-o1.36 | 2026-10-06 |
| Fedora | FEDORA-2026-663a2d0ba4 | F45 | curl | 2026-10-05 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | emacs-common-tuareg | 2026-10-06 |
| Fedora | FEDORA-2026-3e109a0c85 | F44 | ffmpeg | 2026-10-01 |
| Fedora | FEDORA-2026-7a31054ed6 | F44 | flatpak | 2026-10-04 |
| Fedora | FEDORA-2026-62bbabcf11 | F44 | flocq | 2026-10-07 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | flocq | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | frama-c | 2026-10-06 |
| Fedora | FEDORA-2026-9aca5215f2 | F44 | freerdp | 2026-10-07 |
| Fedora | FEDORA-2026-1d8e7b0fd5 | F45 | freerdp | 2026-10-01 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | freetennis | 2026-10-06 |
| Fedora | FEDORA-2026-62bbabcf11 | F44 | gappalib-coq | 2026-10-07 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | gappalib-coq | 2026-10-06 |
| Fedora | FEDORA-2026-203e30f5d8 | F43 | golang-x-mod | 2026-10-07 |
| Fedora | FEDORA-2026-9626645a48 | F44 | golang-x-mod | 2026-10-07 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | guestfs-tools | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | haxe | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | hevea | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | hivex | 2026-10-06 |
| Fedora | FEDORA-2026-34b2d69632 | F44 | httpd | 2026-10-07 |
| Fedora | FEDORA-2026-2a6ce5b288 | F43 | janus | 2026-10-07 |
| Fedora | FEDORA-2026-256bf09e34 | F44 | janus | 2026-10-07 |
| Fedora | FEDORA-2026-d58d30885a | F45 | janus | 2026-10-06 |
| Fedora | FEDORA-2026-754bab2c40 | F43 | kernel | 2026-10-06 |
| Fedora | FEDORA-2026-8dc7d1def3 | F45 | kernel | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | lem | 2026-10-06 |
| Fedora | FEDORA-2026-33dcab55b4 | F43 | lemonldap-ng | 2026-10-04 |
| Fedora | FEDORA-2026-827241e2de | F44 | lemonldap-ng | 2026-10-04 |
| Fedora | FEDORA-2026-0072911d9d | F45 | libX11 | 2026-10-05 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | libguestfs | 2026-10-06 |
| Fedora | FEDORA-2026-a76bba1412 | F44 | libical | 2026-10-07 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | libnbd | 2026-10-06 |
| Fedora | FEDORA-2026-3c05c90d12 | F43 | librabbitmq | 2026-10-01 |
| Fedora | FEDORA-2026-981119a846 | F44 | librabbitmq | 2026-10-01 |
| Fedora | FEDORA-2026-5ce63a9cfb | F45 | librabbitmq | 2026-10-01 |
| Fedora | FEDORA-2026-6debf34169 | F44 | musescore | 2026-10-07 |
| Fedora | FEDORA-2026-e5a087cb33 | F45 | musescore | 2026-10-06 |
| Fedora | FEDORA-2026-c213ad9471 | F45 | nagios-plugins | 2026-10-05 |
| Fedora | FEDORA-2026-aa32e385dc | F43 | nanosvg | 2026-10-04 |
| Fedora | FEDORA-2026-4718fc201a | F44 | nanosvg | 2026-10-04 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | nbdkit | 2026-10-06 |
| Fedora | FEDORA-2026-be2a2ca70a | F45 | noctalia | 2026-10-05 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | not-ocamlfind | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-SDL | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-afl-persistent | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-alcotest | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-astring | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-atd | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-augeas | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-b0 | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-base | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-base64 | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-benchmark | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-bin-prot | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-biniou | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-bisect-ppx | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-bos | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-cairo | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-calendar | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-camlbz2 | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-camlidl | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-camlimages | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-camlp-streams | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-camlp5 | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-camlp5-buildscripts | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-camlpdf | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-camomile | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-capitalization | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-cinaps | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-cmdliner | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-compiler-libs-janestreet | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-cpdf | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-cppo | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-crowbar | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-cryptokit | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-csexp | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-csv | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ctypes | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-cudf | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-curl | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-curses | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-dbus | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-domain-name | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-dose3 | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-dune | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-easy-format | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-expat | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-extlib | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-facile | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-fieldslib | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-fileutils | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-findlib | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-fmt | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-fpath | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-gen | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-gettext | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-graphics | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-gsl | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-integers | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-intrinsics-kernel | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-jane-street-headers | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-jsonm | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-jst-config | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-lablgl | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-lablgtk | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-lablgtk3 | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-labltk | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-lacaml | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-lambda-term | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-libvirt | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-linenoise | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-logs | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-luv | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-lwt | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-mccs | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-mdx | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-menhir | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-merlin | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-mew | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-mew-vi | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-mlgmpidl | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-mlmpfr | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-monolith | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-mtime | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-mysql | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-num | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-obuild | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ocamlbuild | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ocamlgraph | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ocamlnet | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ocp-indent | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ocplib-endian | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ocplib-simplex | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-omake | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-omd | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-opam-0install-cudf | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-opam-file-format | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ounit | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-parmap | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-parsexp | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-patch | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-pcre2 | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-perl4caml | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-postgresql | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-pp | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-pprint | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-assert | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-base | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-bench | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-bin-prot | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-cold | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-compare | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-custom-printf | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-derivers | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-deriving | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-deriving-yaml | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-deriving-yojson | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-enumerate | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-expect | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-fields-conv | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-globalize | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-hash | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-here | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-inline-test | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-let | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-optcomp | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-sexp-conv | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-stable-witness | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppx-variants-conv | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppxlib | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ppxlib-jane | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-psmt2-frontend | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ptmap | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-pyml | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-qcheck | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-qtest | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-re | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-react | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-res | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-result | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-rresult | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-sedlex | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-sexplib | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-sexplib0 | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-sha | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-spdx-licenses | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-sqlite | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-ssl | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-stdcompat | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-stdio | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-stdlib-random | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-store | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-swhid-core | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-testo | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-time-now | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-topkg | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-trie | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-unionfind | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-uucd | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-uucp | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-uunf | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-uuseg | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-uutf | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-variantslib | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-version | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-xml-light | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-xmlm | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-xmlrpc-light | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-yaml | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-yamlx | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-yojson | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-zarith | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-zed | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-zip | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocaml-zmq | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocamlify | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | ocamlmod | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | opam | 2026-10-06 |
| Fedora | FEDORA-2026-ccc419650a | F43 | openbao | 2026-10-01 |
| Fedora | FEDORA-2026-06c29a2cb4 | F45 | openssl | 2026-10-05 |
| Fedora | FEDORA-2026-5fb5fb6508 | F45 | perl-DBI | 2026-10-06 |
| Fedora | FEDORA-2026-6197f5c17e | F43 | pgbouncer | 2026-10-05 |
| Fedora | FEDORA-2026-99030761e8 | F44 | pgbouncer | 2026-10-05 |
| Fedora | FEDORA-2026-851c3ccde8 | F45 | pgbouncer | 2026-10-05 |
| Fedora | FEDORA-2026-d5e4829deb | F43 | php | 2026-10-01 |
| Fedora | FEDORA-2026-5f0023de35 | F44 | php | 2026-10-01 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | planets | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | plplot | 2026-10-06 |
| Fedora | FEDORA-2026-1a5c7b6f1f | F45 | pocillo-gtk-theme | 2026-10-04 |
| Fedora | FEDORA-2026-1e56ab167d | F44 | prometheus | 2026-10-04 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | prooftree | 2026-10-06 |
| Fedora | FEDORA-2026-05e36e4865 | F43 | python-cssselect2 | 2026-10-01 |
| Fedora | FEDORA-2026-2853ef7804 | F45 | python-cssselect2 | 2026-10-01 |
| Fedora | FEDORA-2026-72a7879d08 | F43 | python-streamlink | 2026-10-05 |
| Fedora | FEDORA-2026-72a7879d08 | F43 | python-urllib3 | 2026-10-05 |
| Fedora | FEDORA-2026-056196047a | F43 | python-uv-build | 2026-10-01 |
| Fedora | FEDORA-2026-407b957a3b | F44 | python-uv-build | 2026-10-01 |
| Fedora | FEDORA-2026-d1044d27b7 | F45 | python-uv-build | 2026-10-04 |
| Fedora | FEDORA-2026-6261b26f4e | F44 | python3-docs | 2026-10-07 |
| Fedora | FEDORA-2026-ab1400e97a | F45 | python3-docs | 2026-10-06 |
| Fedora | FEDORA-2026-f30cb310f9 | F43 | python3.12 | 2026-10-06 |
| Fedora | FEDORA-2026-b3da0d09be | F44 | python3.12 | 2026-10-04 |
| Fedora | FEDORA-2026-6261b26f4e | F44 | python3.14 | 2026-10-07 |
| Fedora | FEDORA-2026-ab1400e97a | F45 | python3.15 | 2026-10-06 |
| Fedora | FEDORA-2026-62bbabcf11 | F44 | rocq | 2026-10-07 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | rocq | 2026-10-06 |
| Fedora | FEDORA-2026-62bbabcf11 | F44 | rocq-stdlib | 2026-10-07 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | rocq-stdlib | 2026-10-06 |
| Fedora | FEDORA-2026-056196047a | F43 | ruff | 2026-10-01 |
| Fedora | FEDORA-2026-407b957a3b | F44 | ruff | 2026-10-01 |
| Fedora | FEDORA-2026-d1044d27b7 | F45 | ruff | 2026-10-04 |
| Fedora | FEDORA-2026-056196047a | F43 | rust-libcst | 2026-10-01 |
| Fedora | FEDORA-2026-407b957a3b | F44 | rust-libcst | 2026-10-01 |
| Fedora | FEDORA-2026-d1044d27b7 | F45 | rust-libcst | 2026-10-04 |
| Fedora | FEDORA-2026-056196047a | F43 | rust-libcst_derive | 2026-10-01 |
| Fedora | FEDORA-2026-407b957a3b | F44 | rust-libcst_derive | 2026-10-01 |
| Fedora | FEDORA-2026-d1044d27b7 | F45 | rust-libcst_derive | 2026-10-04 |
| Fedora | FEDORA-2026-056196047a | F43 | rust-salsa | 2026-10-01 |
| Fedora | FEDORA-2026-407b957a3b | F44 | rust-salsa | 2026-10-01 |
| Fedora | FEDORA-2026-d1044d27b7 | F45 | rust-salsa | 2026-10-04 |
| Fedora | FEDORA-2026-056196047a | F43 | rust-salsa-macro-rules | 2026-10-01 |
| Fedora | FEDORA-2026-407b957a3b | F44 | rust-salsa-macro-rules | 2026-10-01 |
| Fedora | FEDORA-2026-d1044d27b7 | F45 | rust-salsa-macro-rules | 2026-10-04 |
| Fedora | FEDORA-2026-056196047a | F43 | rust-salsa-macros | 2026-10-01 |
| Fedora | FEDORA-2026-407b957a3b | F44 | rust-salsa-macros | 2026-10-01 |
| Fedora | FEDORA-2026-d1044d27b7 | F45 | rust-salsa-macros | 2026-10-04 |
| Fedora | FEDORA-2026-594e78463a | F44 | sos | 2026-10-02 |
| Fedora | FEDORA-2026-cf80902877 | F45 | sos | 2026-10-01 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | supermin | 2026-10-06 |
| Fedora | FEDORA-2026-4585aba520 | F43 | tesseract | 2026-10-07 |
| Fedora | FEDORA-2026-fc27f09459 | F44 | tesseract | 2026-10-07 |
| Fedora | FEDORA-2026-056196047a | F43 | ty | 2026-10-01 |
| Fedora | FEDORA-2026-407b957a3b | F44 | ty | 2026-10-01 |
| Fedora | FEDORA-2026-d1044d27b7 | F45 | ty | 2026-10-04 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | unison | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | utop | 2026-10-06 |
| Fedora | FEDORA-2026-056196047a | F43 | uv | 2026-10-01 |
| Fedora | FEDORA-2026-407b957a3b | F44 | uv | 2026-10-01 |
| Fedora | FEDORA-2026-d1044d27b7 | F45 | uv | 2026-10-04 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | virt-top | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | virt-v2v | 2026-10-06 |
| Fedora | FEDORA-2026-05e36e4865 | F43 | weasyprint | 2026-10-01 |
| Fedora | FEDORA-2026-2853ef7804 | F45 | weasyprint | 2026-10-01 |
| Fedora | FEDORA-2026-62bbabcf11 | F44 | why3 | 2026-10-07 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | why3 | 2026-10-06 |
| Fedora | FEDORA-2026-93f562a43f | F44 | xdg-dbus-proxy | 2026-10-01 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | xen | 2026-10-06 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | z3 | 2026-10-06 |
| Fedora | FEDORA-2026-62bbabcf11 | F44 | zenon | 2026-10-07 |
| Fedora | FEDORA-2026-403bcf6fd8 | F45 | zenon | 2026-10-06 |
| Mageia | MGASA-2026-0464 | 10 | libgcrypt | 2026-10-02 |
| Mageia | MGASA-2026-0463 | 10 | python-pillow | 2026-10-01 |
| Mageia | MGASA-2026-0467 | 10 | python-tornado | 2026-10-02 |
| Mageia | MGASA-2026-0466 | 10 | python-urwid, python-wcwidth | 2026-10-02 |
| Mageia | MGASA-2026-0469 | 10 | srt | 2026-10-06 |
| Mageia | MGASA-2026-0468 | 10 | tor | 2026-10-06 |
| Mageia | MGASA-2026-0465 | 10 | wireshark | 2026-10-02 |
| Oracle | ELSA-2026-75577 | OL10 | bind | 2026-10-05 |
| Oracle | ELSA-2026-67872 | OL10 | corosync | 2026-10-01 |
| Oracle | ELSA-2026-73765 | OL10 | dogtag-pki | 2026-10-01 |
| Oracle | ELSA-2026-74001 | OL10 | expat | 2026-10-05 |
| Oracle | ELSA-2026-72448 | OL8 | expat | 2026-10-01 |
| Oracle | ELSA-2026-72663 | OL9 | expat | 2026-10-01 |
| Oracle | ELSA-2026-71652 | OL8 | firefox | 2026-10-01 |
| Oracle | ELSA-2026-73979 | OL10 | freerdp | 2026-10-01 |
| Oracle | ELSA-2026-75570 | OL10 | freerdp | 2026-10-06 |
| Oracle | ELSA-2026-68707 | OL7 | freerdp | 2026-10-01 |
| Oracle | ELSA-2026-73429 | OL10 | gawk | 2026-10-01 |
| Oracle | ELSA-2026-73511 | OL8 | gawk | 2026-10-05 |
| Oracle | ELSA-2026-73512 | OL9 | gawk | 2026-10-01 |
| Oracle | ELSA-2026-73427 | OL10 | gdb | 2026-10-05 |
| Oracle | ELSA-2026-73426 | OL9 | gdb | 2026-10-05 |
| Oracle | ELSA-2026-74464 | OL10 | ghostscript | 2026-10-05 |
| Oracle | ELSA-2026-74457 | OL9 | ghostscript | 2026-10-05 |
| Oracle | ELSA-2026-75575 | OL9 | gimp | 2026-10-05 |
| Oracle | ELSA-2026-65773-0 | OL7 | glib2 | 2026-10-01 |
| Oracle | ELSA-2026-73998 | OL10 | gvfs | 2026-10-05 |
| Oracle | ELSA-2026-73997 | OL8 | gvfs | 2026-10-05 |
| Oracle | ELSA-2026-74370 | OL9 | gvfs | 2026-10-05 |
| Oracle | ELSA-2026-72279 | OL10 | ipa | 2026-10-01 |
| Oracle | ELSA-2026-71233 | OL10 | kernel | 2026-10-05 |
| Oracle | ELSA-2026-72624 | OL10 | kernel | 2026-10-05 |
| Oracle | ELSA-2026-70402 | OL8 | kernel | 2026-10-05 |
| Oracle | ELSA-2026-71213 | OL8 | kernel | 2026-10-05 |
| Oracle | ELSA-2026-71329 | OL8 | kernel | 2026-10-05 |
| Oracle | ELSA-2026-74133 | OL8 | kernel | 2026-10-05 |
| Oracle | ELSA-2026-75747 | OL8 | kernel | 2026-10-06 |
| Oracle | ELSA-2026-71700 | OL9 | kernel | 2026-10-01 |
| Oracle | ELSA-2026-72623 | OL9 | kernel | 2026-10-01 |
| Oracle | ELSA-2026-74438 | OL9 | kernel | 2026-10-05 |
| Oracle | ELSA-2026-62231-0 | OL7 | libXfont2 | 2026-10-01 |
| Oracle | ELSA-2026-74442 | OL10 | libpcap | 2026-10-05 |
| Oracle | ELSA-2026-76045 | OL8 | libpcap | 2026-10-06 |
| Oracle | ELSA-2026-74441 | OL9 | libpcap | 2026-10-05 |
| Oracle | ELSA-2026-75583 | OL10 | libvirt | 2026-10-05 |
| Oracle | ELSA-2026-74424 | OL9 | libvirt | 2026-10-05 |
| Oracle | ELSA-2026-75674 | OL8 | mariadb-connector-c | 2026-10-06 |
| Oracle | ELSA-2026-75673 | OL9 | mariadb-connector-c | 2026-10-06 |
| Oracle | ELSA-2026-75581 | OL10 | mod_auth_openidc | 2026-10-05 |
| Oracle | ELSA-2026-75864 | OL10 | nodejs22 | 2026-10-06 |
| Oracle | ELSA-2026-73838 | OL9 | nodejs:24 | 2026-10-01 |
| Oracle | ELSA-2026-69129 | OL10 | openssh | 2026-10-01 |
| Oracle | ELSA-2026-73954 | OL10 | openssh | 2026-10-05 |
| Oracle | ELSA-2026-73955 | OL9 | openssh | 2026-10-05 |
| Oracle | ELSA-2026-67148-0 | OL8 | osbuild-composer | 2026-10-01 |
| Oracle | ELSA-2026-71608 | OL8 | perl-DBI | 2026-10-01 |
| Oracle | ELSA-2026-73766 | OL9 | pki-core | 2026-10-01 |
| Oracle | ELSA-2026-72274 | OL8 | postgresql:12 | 2026-10-01 |
| Oracle | ELSA-2026-71658 | OL10 | python-cryptography | 2026-10-01 |
| Oracle | ELSA-2026-72424 | OL9 | resteasy | 2026-10-01 |
| Oracle | ELSA-2026-74095 | OL8 | rsync | 2026-10-05 |
| Oracle | ELSA-2026-72785 | OL10 | ruby | 2026-10-01 |
| Oracle | ELSA-2026-72286 | OL9 | ruby | 2026-10-01 |
| Oracle | ELSA-2026-72427 | OL10 | ruby4.0 | 2026-10-01 |
| Oracle | ELSA-2026-72285 | OL8 | ruby:3.3 | 2026-10-01 |
| Oracle | ELSA-2026-72485 | OL9 | ruby:3.3 | 2026-10-01 |
| Oracle | ELSA-2026-72484 | OL9 | ruby:4.0 | 2026-10-01 |
| Oracle | ELSA-2026-75579 | OL10 | sudo | 2026-10-06 |
| Oracle | ELSA-2026-75580 | OL8 | sudo | 2026-10-06 |
| Oracle | ELSA-2026-75571 | OL9 | sudo | 2026-10-06 |
| Oracle | ELSA-2026-73130 | OL10 | thunderbird | 2026-10-01 |
| Oracle | ELSA-2026-73971 | OL8 | thunderbird | 2026-10-05 |
| Oracle | ELSA-2026-75768 | OL9 | vim | 2026-10-06 |
| Oracle | ELSA-2026-74084 | OL8 | webkit2gtk3 | 2026-10-05 |
| Oracle | ELSA-2026-61234-0 | OL7 | xmlrpc-c | 2026-10-01 |
| Red Hat | RHSA-2026:64805-01 | EL10.0 | acl | 2026-10-01 |
| Red Hat | RHSA-2026:72820-01 | EL8.4 | acl | 2026-10-01 |
| Red Hat | RHSA-2026:72819-01 | EL8.6 | acl | 2026-10-01 |
| Red Hat | RHSA-2026:71656-01 | EL8.8 | acl | 2026-10-01 |
| Red Hat | RHSA-2026:67142-01 | EL9.2 | acl | 2026-10-01 |
| Red Hat | RHSA-2026:67144-01 | EL9.4 | acl | 2026-10-01 |
| Red Hat | RHSA-2026:67140-01 | EL9.6 | acl | 2026-10-01 |
| Red Hat | RHSA-2026:74001-01 | EL10 | expat | 2026-10-07 |
| Red Hat | RHSA-2026:72448-01 | EL8 | expat | 2026-10-07 |
| Red Hat | RHSA-2026:72663-01 | EL9 | expat | 2026-10-07 |
| Red Hat | RHSA-2026:64799-01 | EL10 | glib2 | 2026-10-01 |
| Red Hat | RHSA-2026:71404-01 | EL10.0 | glib2 | 2026-10-01 |
| Red Hat | RHSA-2026:66451-01 | EL8 | glib2 | 2026-10-01 |
| Red Hat | RHSA-2026:64800-01 | EL9 | glib2 | 2026-10-01 |
| Red Hat | RHSA-2026:71405-01 | EL9.2 | glib2 | 2026-10-01 |
| Red Hat | RHSA-2026:70636-01 | EL9.4 | glib2 | 2026-10-01 |
| Red Hat | RHSA-2026:71403-01 | EL9.6 | glib2 | 2026-10-01 |
| Red Hat | RHSA-2026:22112-01 | EL8 | go-toolset:rhel8 | 2026-10-01 |
| Red Hat | RHSA-2026:22120-01 | EL10 | golang | 2026-10-01 |
| Red Hat | RHSA-2026:49702-01 | EL10.0 | golang | 2026-10-01 |
| Red Hat | RHSA-2026:22121-01 | EL9 | golang | 2026-10-01 |
| Red Hat | RHSA-2026:49712-01 | EL9.6 | golang | 2026-10-01 |
| Red Hat | RHSA-2026:76809-01 | EL9.2 | grafana | 2026-10-07 |
| Red Hat | RHSA-2026:76795-01 | EL9.4 | grafana | 2026-10-07 |
| Red Hat | RHSA-2026:70596-01 | EL10.0 | libxml2 | 2026-10-01 |
| Red Hat | RHSA-2026:70639-01 | EL9.6 | libxml2 | 2026-10-01 |
| Red Hat | RHSA-2026:61242-01 | EL8 | mingw-sqlite | 2026-10-01 |
| Red Hat | RHSA-2026:52841-01 | EL10 | nodejs-nodemon | 2026-10-01 |
| Red Hat | RHSA-2026:61374-01 | EL10.0 | nodejs-nodemon | 2026-10-01 |
| Red Hat | RHSA-2026:55541-01 | EL10 | nodejs22 | 2026-10-01 |
| Red Hat | RHSA-2026:64817-01 | EL10.0 | nodejs22 | 2026-10-01 |
| Red Hat | RHSA-2026:58819-01 | EL10 | nodejs24 | 2026-10-01 |
| Red Hat | RHSA-2026:54530-01 | EL8 | nodejs:22 | 2026-10-01 |
| Red Hat | RHSA-2026:55601-01 | EL9 | nodejs:22 | 2026-10-01 |
| Red Hat | RHSA-2026:62416-01 | EL9.6 | nodejs:22 | 2026-10-01 |
| Red Hat | RHSA-2026:54371-01 | EL8 | nodejs:24 | 2026-10-01 |
| Red Hat | RHSA-2026:55603-01 | EL9 | nodejs:24 | 2026-10-01 |
| Red Hat | RHSA-2026:75689-01 | EL7 | rhc-worker-script | 2026-10-05 |
| Red Hat | RHSA-2026:74581-01 | EL9.6 | skopeo | 2026-10-02 |
| Red Hat | RHSA-2026:58927-01 | EL10 | sqlite | 2026-10-01 |
| Red Hat | RHSA-2026:61697-01 | EL10.0 | sqlite | 2026-10-01 |
| Red Hat | RHSA-2026:58938-01 | EL8 | sqlite | 2026-10-01 |
| Red Hat | RHSA-2026:59024-01 | EL8.4 | sqlite | 2026-10-01 |
| Red Hat | RHSA-2026:59020-01 | EL8.6 | sqlite | 2026-10-01 |
| Red Hat | RHSA-2026:58939-01 | EL8.8 | sqlite | 2026-10-01 |
| Red Hat | RHSA-2026:58936-01 | EL9 | sqlite | 2026-10-01 |
| Red Hat | RHSA-2026:62232-01 | EL9.2 | sqlite | 2026-10-01 |
| Red Hat | RHSA-2026:62236-01 | EL9.4 | sqlite | 2026-10-01 |
| Red Hat | RHSA-2026:59956-01 | EL9.6 | sqlite | 2026-10-01 |
| Red Hat | RHSA-2026:67830-01 | EL10 | tesseract | 2026-10-01 |
| Red Hat | RHSA-2026:71566-01 | EL10.0 | tesseract | 2026-10-01 |
| Red Hat | RHSA-2026:67832-01 | EL8 | tesseract | 2026-10-01 |
| Red Hat | RHSA-2026:69495-01 | EL8.6 | tesseract | 2026-10-01 |
| Red Hat | RHSA-2026:69111-01 | EL8.8 | tesseract | 2026-10-01 |
| Red Hat | RHSA-2026:67831-01 | EL9 | tesseract | 2026-10-01 |
| Red Hat | RHSA-2026:72280-01 | EL9.2 | tesseract | 2026-10-01 |
| Red Hat | RHSA-2026:71568-01 | EL9.4 | tesseract | 2026-10-01 |
| Red Hat | RHSA-2026:71567-01 | EL9.6 | tesseract | 2026-10-01 |
| Red Hat | RHSA-2026:66336-01 | EL10 | vim | 2026-10-01 |
| Red Hat | RHSA-2026:75769-01 | EL10 | vim | 2026-10-06 |
| Red Hat | RHSA-2026:69128-01 | EL6 | vim | 2026-10-01 |
| Red Hat | RHSA-2026:66348-01 | EL8 | vim | 2026-10-01 |
| Red Hat | RHSA-2026:66366-01 | EL9 | vim | 2026-10-01 |
| Red Hat | RHSA-2026:75768-01 | EL9 | vim | 2026-10-06 |
| Red Hat | RHSA-2026:72466-01 | EL9.2 | vim | 2026-10-01 |
| Red Hat | RHSA-2026:72465-01 | EL9.4 | vim | 2026-10-01 |
| Red Hat | RHSA-2026:70818-01 | EL9.6 | vim | 2026-10-01 |
| Slackware | SSA:2026-278-01 | cups | 2026-10-05 | |
| Slackware | SSA:2026-273-01 | libpng | 2026-09-30 | |
| Slackware | SSA:2026-273-02 | mozilla-thunderbird | 2026-09-30 | |
| Slackware | SSA:2026-279-01 | openssh | 2026-10-06 | |
| SUSE | SUSE-SU-2026:23948-1 | SLE16.0 | ImageMagick | 2026-10-01 |
| SUSE | SUSE-SU-2026:4408-1 | SLE15 | alloy | 2026-10-01 |
| SUSE | openSUSE-SU-2026:11914-1 | TW | amazon-ecs-init | 2026-10-03 |
| SUSE | openSUSE-SU-2026:11940-1 | TW | apache-sshd | 2026-10-05 |
| SUSE | openSUSE-SU-2026:11915-1 | TW | binaryen-133 | 2026-10-03 |
| SUSE | openSUSE-SU-2026:11916-1 | TW | bind | 2026-10-03 |
| SUSE | openSUSE-SU-2026:11932-1 | TW | binutils | 2026-10-05 |
| SUSE | openSUSE-SU-2026:11888-1 | TW | chromedriver | 2026-09-30 |
| SUSE | openSUSE-SU-2026:21987-1 | oS16.0 | chromium | 2026-10-01 |
| SUSE | openSUSE-SU-2026:0343-1 | osB15 | chromium | 2026-10-01 |
| SUSE | openSUSE-SU-2026:0344-1 | osB15 | chromium | 2026-10-05 |
| SUSE | openSUSE-SU-2026:0345-1 | osB15 | chromium | 2026-10-06 |
| SUSE | SUSE-SU-2026:4447-1 | SLE12 | cups | 2026-10-05 |
| SUSE | SUSE-SU-2026:23990-1 | SLE16.0 | distribution | 2026-10-05 |
| SUSE | SUSE-SU-2026:4533-1 | SLE12 | docker-stable | 2026-10-06 |
| SUSE | SUSE-SU-2026:4535-1 | SLE15 | docker-stable | 2026-10-06 |
| SUSE | SUSE-SU-2026:23949-1 | SLE16.0 | emacs | 2026-10-01 |
| SUSE | openSUSE-SU-2026:11889-1 | TW | emacs | 2026-09-30 |
| SUSE | openSUSE-SU-2026:21974-1 | oS16.0 | emacs | 2026-10-01 |
| SUSE | SUSE-SU-2026:4543-1 | SLE12 | firefox | 2026-10-06 |
| SUSE | SUSE-SU-2026:4545-1 | SLE15 oS15.4 | firefox | 2026-10-06 |
| SUSE | SUSE-SU-2026:23981-1 | SLE16.0 | firefox | 2026-10-05 |
| SUSE | openSUSE-SU-2026:11917-1 | TW | firefox-esr | 2026-10-03 |
| SUSE | SUSE-SU-2026:4400-1 | SLE15 oS15.4 | gdb | 2026-09-30 |
| SUSE | SUSE-SU-2026:4409-1 | SLE15 oS15.4 | gimp | 2026-10-01 |
| SUSE | openSUSE-SU-2026:11890-1 | TW | gimp | 2026-09-30 |
| SUSE | SUSE-SU-2026:23971-1 | SLE-m6.2 | glib2 | 2026-10-05 |
| SUSE | SUSE-SU-2026:23980-1 | SLE16.0 | glib2 | 2026-10-05 |
| SUSE | openSUSE-SU-2026:21977-1 | oS16.0 | glib2 | 2026-10-01 |
| SUSE | SUSE-SU-2026:23957-1 | SLE-m6.2 | glibc | 2026-10-01 |
| SUSE | SUSE-SU-2026:23929-1 | SLE-m6.2 | glibc | 2026-10-01 |
| SUSE | SUSE-SU-2026:23934-1 | SLE16.0 | glibc | 2026-10-01 |
| SUSE | openSUSE-SU-2026:21968-1 | oS16.0 | glibc | 2026-10-01 |
| SUSE | SUSE-SU-2026:23950-1 | SLE16.0 | gnome-shell | 2026-10-01 |
| SUSE | openSUSE-SU-2026:11919-1 | TW | gnumeric | 2026-10-03 |
| SUSE | openSUSE-SU-2026:11891-1 | TW | gpsd | 2026-09-30 |
| SUSE | SUSE-SU-2026:23973-1 | SLE-m6.2 | helm | 2026-10-05 |
| SUSE | SUSE-SU-2026:23984-1 | SLE16.0 | helm | 2026-10-05 |
| SUSE | openSUSE-SU-2026:11892-1 | TW | helm3 | 2026-10-01 |
| SUSE | openSUSE-SU-2026:21973-1 | oS16.0 | imagemagick | 2026-10-01 |
| SUSE | SUSE-SU-2026:4515-1 | SLE12 | java-11-openjdk | 2026-10-05 |
| SUSE | SUSE-SU-2026:4407-1 | SLE15 | jawn | 2026-09-30 |
| SUSE | SUSE-SU-2026:23989-1 | SLE16.0 | jline3 | 2026-10-05 |
| SUSE | openSUSE-SU-2026:22009-1 | oS16.0 | jline3 | 2026-10-03 |
| SUSE | openSUSE-SU-2026:11945-1 | TW | jupyter-jupyterlab | 2026-10-06 |
| SUSE | openSUSE-SU-2026:11893-1 | TW | kernel-devel | 2026-10-01 |
| SUSE | SUSE-SU-2026:4441-1 | SLE15 | kubevirt-1.6 | 2026-10-05 |
| SUSE | openSUSE-SU-2026:11894-1 | TW | libX11-6 | 2026-10-01 |
| SUSE | SUSE-SU-2026:4410-1 | SLE12 | libX11 | 2026-10-01 |
| SUSE | SUSE-SU-2026:4502-1 | SLE15 | libX11 | 2026-10-05 |
| SUSE | SUSE-SU-2026:4500-1 | SLE15 SLE5.3 SLE5.4 SLE5.5 SLE-m5.3 SLE-m5.4 SLE-m5.5 | libX11 | 2026-10-05 |
| SUSE | SUSE-SU-2026:4501-1 | SLE15 oS15.6 | libX11 | 2026-10-05 |
| SUSE | openSUSE-SU-2026:11895-1 | TW | libXi-devel | 2026-10-01 |
| SUSE | openSUSE-SU-2026:11896-1 | TW | libXpm-devel | 2026-10-01 |
| SUSE | openSUSE-SU-2026:11897-1 | TW | libXtst-devel | 2026-10-01 |
| SUSE | openSUSE-SU-2026:11924-1 | TW | libparted-fs-resize0 | 2026-10-04 |
| SUSE | openSUSE-SU-2026:11885-1 | TW | libpoppler-cpp3 | 2026-09-30 |
| SUSE | openSUSE-SU-2026:11933-1 | TW | libraw-devel | 2026-10-05 |
| SUSE | openSUSE-SU-2026:11922-1 | TW | libslirp-devel | 2026-10-04 |
| SUSE | SUSE-SU-2026:23985-1 | SLE16.0 | libtcnative-1-0, libtcnative-2-0, tomcat, tomcat10, tomcat11 | 2026-10-05 |
| SUSE | openSUSE-SU-2026:21984-1 | oS16.0 | libtcnative-1-0, libtcnative-2-0, tomcat, tomcat10, | 2026-10-01 |
| SUSE | SUSE-SU-2026:4546-1 | SLE15 | libtcnative-1-0, tomcat, tomcat10 | 2026-10-06 |
| SUSE | SUSE-SU-2026:4544-1 | SLE15 oS15.6 | libtcnative-1-0, tomcat11 | 2026-10-06 |
| SUSE | openSUSE-SU-2026:11898-1 | TW | libtcnative-1-0 | 2026-10-01 |
| SUSE | openSUSE-SU-2026:11899-1 | TW | libtcnative-2-0 | 2026-10-01 |
| SUSE | openSUSE-SU-2026:11887-1 | TW | libtesseract5 | 2026-09-30 |
| SUSE | openSUSE-SU-2026:11912-1 | TW | libwireshark19 | 2026-10-03 |
| SUSE | openSUSE-SU-2026:11900-1 | TW | mistral-vibe | 2026-10-01 |
| SUSE | SUSE-SU-2026:4406-1 | SLE15 | multipath-tools | 2026-09-30 |
| SUSE | openSUSE-SU-2026:11882-1 | TW | netty | 2026-09-30 |
| SUSE | SUSE-SU-2026:4399-1 | SLE12 | ntfs-3g_ntfsprogs | 2026-09-30 |
| SUSE | openSUSE-SU-2026:11923-1 | TW | openai-codex | 2026-10-04 |
| SUSE | SUSE-SU-2026:4532-1 | SLE12 | openexr | 2026-10-06 |
| SUSE | SUSE-SU-2026:4414-1 | SLE15 | openssl-3 | 2026-10-02 |
| SUSE | SUSE-SU-2026:4413-1 | SLE15 SLE5.3 SLE5.4 SLE-m5.3 SLE-m5.4 oS15.4 | openssl-3 | 2026-10-02 |
| SUSE | SUSE-SU-2026:4412-1 | SLE15 oS15.5 | openssl-3 | 2026-10-02 |
| SUSE | openSUSE-SU-2026:11883-1 | TW | pcapplusplus-devel | 2026-09-30 |
| SUSE | SUSE-SU-2026:4458-1 | SLE15 SLE5.3 SLE5.4 SLE5.5 SLE-m5.3 SLE-m5.4 SLE-m5.5 oS15.4 | pcre2 | 2026-10-05 |
| SUSE | SUSE-SU-2026:23952-1 | SLE-m6.2 | perl-DBI | 2026-10-01 |
| SUSE | SUSE-SU-2026:4442-1 | SLE12 | perl-DBI | 2026-10-05 |
| SUSE | SUSE-SU-2026:23945-1 | SLE16.0 | perl-Protocol-HTTP2 | 2026-10-01 |
| SUSE | SUSE-SU-2026:23943-1 | SLE16.0 | php-composer2 | 2026-10-01 |
| SUSE | openSUSE-SU-2026:11901-1 | TW | php8 | 2026-10-01 |
| SUSE | openSUSE-SU-2026:11884-1 | TW | pi-coding-agent | 2026-09-30 |
| SUSE | SUSE-SU-2026:4402-1 | SLE12 | python-PyYAML | 2026-09-30 |
| SUSE | SUSE-SU-2026:4411-1 | SLE15 | python | 2026-10-01 |
| SUSE | SUSE-SU-2026:4443-1 | SLE15 oS15.6 | python-msgpack | 2026-10-05 |
| SUSE | SUSE-SU-2026:4404-1 | SLE15 SLE5.3 SLE5.4 SLE5.5 SLE-m5.3 SLE-m5.4 SLE-m5.5 | python-tornado | 2026-09-30 |
| SUSE | SUSE-SU-2026:4403-1 | SLE15 oS15.4 | python-tornado6 | 2026-09-30 |
| SUSE | openSUSE-SU-2026:11949-1 | TW | python310 | 2026-10-06 |
| SUSE | openSUSE-SU-2026:11886-1 | TW | python311 | 2026-09-30 |
| SUSE | SUSE-SU-2026:4534-1 | SLE15 oS15.6 | python312 | 2026-10-06 |
| SUSE | SUSE-SU-2026:4401-1 | SLE15 | python313 | 2026-09-30 |
| SUSE | openSUSE-SU-2026:11943-1 | TW | python313-Werkzeug | 2026-10-06 |
| SUSE | openSUSE-SU-2026:11944-1 | TW | python313-azure-storage-queue | 2026-10-06 |
| SUSE | openSUSE-SU-2026:11946-1 | TW | python313-langchain-anthropic | 2026-10-06 |
| SUSE | openSUSE-SU-2026:11927-1 | TW | python313-litellm | 2026-10-04 |
| SUSE | openSUSE-SU-2026:11947-1 | TW | python313-sglang | 2026-10-06 |
| SUSE | openSUSE-SU-2026:11936-1 | TW | python313-tokenizers | 2026-10-05 |
| SUSE | SUSE-SU-2026:23959-1 | SLE-m6.2 | rpcbind | 2026-10-01 |
| SUSE | SUSE-SU-2026:4446-1 | SLE12 | rpcbind | 2026-10-05 |
| SUSE | SUSE-SU-2026:23946-1 | SLE16.0 | rpcbind | 2026-10-01 |
| SUSE | openSUSE-SU-2026:11929-1 | TW | rpcbind | 2026-10-04 |
| SUSE | SUSE-SU-2026:4457-1 | SLE5.3 SLE-m5.3 oS15.3 | rpm | 2026-10-05 |
| SUSE | SUSE-SU-2026:4445-1 | MP4.3 SLE15 | rubygem-rails-html-sanitizer | 2026-10-05 |
| SUSE | openSUSE-SU-2026:22016-1 | oS16.0 | rustup | 2026-10-03 |
| SUSE | SUSE-SU-2026:23983-1 | SLE16.0 | sccache | 2026-10-05 |
| SUSE | openSUSE-SU-2026:21982-1 | oS16.0 | sccache | 2026-10-01 |
| SUSE | openSUSE-SU-2026:11937-1 | TW | squid | 2026-10-05 |
| SUSE | SUSE-SU-2026:4456-1 | SLE5.5 SLE-m5.5 oS15.5 | sssd | 2026-10-05 |
| SUSE | SUSE-SU-2026:3961-2 | SLE15 | suseconnect-ng | 2026-10-05 |
| SUSE | SUSE-SU-2026:4444-1 | MP4.3 SLE15 | terraform-provider-susepubliccloud | 2026-10-05 |
| SUSE | SUSE-SU-2026:4493-1 | SLE15 | valkey | 2026-10-05 |
| SUSE | SUSE-SU-2026:4491-1 | SLE15 oS15.6 | valkey | 2026-10-05 |
| SUSE | SUSE-SU-2026:23986-1 | SLE16.0 | valkey | 2026-10-05 |
| SUSE | openSUSE-SU-2026:11951-1 | TW | valkey | 2026-10-06 |
| SUSE | openSUSE-SU-2026:21985-1 | oS16.0 | valkey | 2026-10-01 |
| SUSE | SUSE-SU-2026:23975-1 | SLE-m6.2 | wget | 2026-10-05 |
| SUSE | SUSE-SU-2026:23991-1 | SLE16.0 | wget | 2026-10-05 |
| SUSE | SUSE-SU-2026:4405-1 | SLE15 oS15.5 | wicked2nm | 2026-09-30 |
| SUSE | SUSE-SU-2026:4494-1 | SLE12 | wpa_supplicant | 2026-10-05 |
| SUSE | SUSE-SU-2026:4492-1 | SLE15 oS15.6 | wpa_supplicant | 2026-10-05 |
| SUSE | openSUSE-SU-2026:11913-1 | TW | xdg-dbus-proxy | 2026-10-03 |
| Ubuntu | USN-8870-1 | 20.04 22.04 24.04 26.04 | aodh, watcher | 2026-10-05 |
| Ubuntu | USN-8867-1 | 18.04 20.04 22.04 26.04 | ceph | 2026-10-05 |
| Ubuntu | USN-8860-1 | 16.04 18.04 20.04 22.04 24.04 26.04 | designate | 2026-10-01 |
| Ubuntu | USN-8865-1 | 16.04 18.04 20.04 22.04 24.04 26.04 | edk2 | 2026-10-05 |
| Ubuntu | USN-8885-1 | 14.04 16.04 18.04 20.04 22.04 24.04 26.04 | fluidsynth | 2026-10-06 |
| Ubuntu | USN-8880-1 | 24.04 26.04 | freerdp3 | 2026-10-06 |
| Ubuntu | USN-8880-1 | 24.04 26.04 | freerdp3 | 2026-10-07 |
| Ubuntu | USN-8880-1 | 24.04 26.04 | freerdp3 | 2026-10-07 |
| Ubuntu | USN-8881-1 | 22.04 24.04 26.04 | freetype | 2026-10-06 |
| Ubuntu | USN-8881-1 | 22.04 24.04 26.04 | freetype | 2026-10-07 |
| Ubuntu | USN-8883-1 | 22.04 | golang-1.18, golang-1.21, golang-1.24 | 2026-10-06 |
| Ubuntu | USN-8855-1 | 14.04 16.04 18.04 20.04 22.04 24.04 26.04 | gst-plugins-bad1.0 | 2026-10-01 |
| Ubuntu | USN-8863-1 | 16.04 18.04 20.04 22.04 24.04 26.04 | gst-plugins-good1.0 | 2026-10-07 |
| Ubuntu | USN-8845-1 | 16.04 18.04 20.04 22.04 24.04 26.04 | gvfs | 2026-09-30 |
| Ubuntu | USN-8859-1 | 14.04 16.04 18.04 20.04 22.04 24.04 26.04 | imagemagick | 2026-09-30 |
| Ubuntu | USN-8856-1 | 26.04 | kdenlive, mlt | 2026-09-30 |
| Ubuntu | USN-8854-1 | 16.04 18.04 20.04 22.04 24.04 26.04 | keystone | 2026-09-30 |
| Ubuntu | USN-8857-1 | 26.04 | kf6-kcoreaddons | 2026-10-01 |
| Ubuntu | USN-8858-1 | 14.04 16.04 18.04 20.04 22.04 24.04 26.04 | libauthen-sasl-perl | 2026-09-30 |
| Ubuntu | USN-8868-1 | 22.04 24.04 26.04 | libreoffice | 2026-10-05 |
| Ubuntu | USN-8890-1 | 16.04 18.04 20.04 22.04 24.04 26.04 | libsoup2.4, libsoup3 | 2026-10-06 |
| Ubuntu | USN-8893-1 | 16.04 18.04 20.04 22.04 24.04 26.04 | libwebsockets | 2026-10-07 |
| Ubuntu | USN-8872-1 | 16.04 18.04 20.04 22.04 24.04 | libxmltok | 2026-10-06 |
| Ubuntu | USN-8862-1 | 22.04 24.04 26.04 | libxpm | 2026-10-01 |
| Ubuntu | USN-8875-1 | 20.04 22.04 | linux, linux-aws, linux-aws-5.15, linux-aws-fips, linux-azure, linux-azure-5.15, linux-azure-fde-5.15, linux-azure-fips, linux-fips, linux-gke, linux-gkeop, linux-hwe-5.15, linux-ibm, linux-ibm-5.15, linux-intel-iot-realtime, linux-intel-iotg, linux-intel-iotg-5.15, linux-kvm, linux-lowlatency, linux-lowlatency-hwe-5.15, linux-oracle, linux-realtime, linux-xilinx-zynqmp | 2026-10-06 |
| Ubuntu | USN-8864-1 | 14.04 16.04 | linux, linux-aws, linux-fips, linux-kvm, linux-lts-xenial | 2026-10-02 |
| Ubuntu | USN-8887-1 | 26.04 | linux, linux-aws, linux-gcp, linux-gke, linux-ibm, linux-oracle, linux-realtime | 2026-10-06 |
| Ubuntu | USN-8817-3 | 22.04 24.04 | linux-aws, linux-aws-6.8 | 2026-09-30 |
| Ubuntu | USN-8888-1 | 26.04 | linux-azure, linux-azure-fde | 2026-10-06 |
| Ubuntu | USN-8851-3 | 18.04 | linux-azure-5.4 | 2026-10-05 |
| Ubuntu | USN-8876-1 | 22.04 | linux-azure-fde | 2026-10-06 |
| Ubuntu | USN-8818-6 | 22.04 | linux-fips | 2026-10-02 |
| Ubuntu | USN-8877-1 | 22.04 | linux-gcp, linux-gcp-fips | 2026-10-06 |
| Ubuntu | USN-8878-1 | 20.04 | linux-gcp-5.15 | 2026-10-06 |
| Ubuntu | USN-8816-4 | 26.04 | linux-gke | 2026-10-02 |
| Ubuntu | USN-8818-5 | 22.04 | linux-nvidia-tegra, linux-nvidia-tegra-igx | 2026-09-30 |
| Ubuntu | USN-8886-1 | 24.04 | linux-nvidia-tegra | 2026-10-06 |
| Ubuntu | USN-8889-1 | 26.04 | linux-oem-7.0 | 2026-10-06 |
| Ubuntu | USN-8879-1 | 20.04 | linux-oracle-5.15 | 2026-10-06 |
| Ubuntu | USN-8816-3 | 24.04 | linux-oracle-7.0 | 2026-09-30 |
| Ubuntu | USN-8871-1 | 22.04 | linux-raspi | 2026-10-05 |
| Ubuntu | USN-8851-2 | 18.04 | linux-raspi-5.4 | 2026-10-02 |
| Ubuntu | USN-8853-1 | 22.04 | opensbi | 2026-09-30 |
| Ubuntu | USN-8861-1 | 26.04 | openssl | 2026-10-01 |
| Ubuntu | USN-8852-1 | 22.04 24.04 26.04 | openvpn | 2026-09-30 |
| Ubuntu | USN-8848-1 | 14.04 16.04 18.04 20.04 22.04 24.04 26.04 | python-django | 2026-10-01 |
| Ubuntu | USN-8869-1 | 20.04 22.04 24.04 26.04 | rabbitmq-server | 2026-10-06 |
| Ubuntu | USN-8866-1 | 22.04 24.04 26.04 | redis | 2026-10-07 |
| Ubuntu | USN-8874-1 | 14.04 16.04 18.04 20.04 22.04 24.04 26.04 | sg3-utils | 2026-10-06 |
| Ubuntu | USN-8882-1 | 14.04 16.04 18.04 20.04 22.04 24.04 26.04 | tesseract | 2026-10-06 |
| Ubuntu | USN-8884-1 | 16.04 18.04 20.04 22.04 24.04 26.04 | u-boot | 2026-10-06 |
| Ubuntu | USN-8873-1 | 14.04 16.04 18.04 20.04 22.04 24.04 26.04 | unbound | 2026-10-06 |
Kernel patches of interest
Kernel releases
Architecture-specific
BPF-related
Core kernel
Development tools
Device drivers
Device-driver infrastructure
Documentation
Filesystems and block layer
Memory management
Networking
Security-related
Virtualization and containers
Miscellaneous
Page editor: Joe Brockmeier